US English


7 Senior GRC Analyst - SOX IT Controls Resume Templates with Example
By Ria · Last Updated On October 23, 2026
Resume example — page 1

This guide shows you how to create a Senior GRC Analyst - SOX IT Controls resume that presents audit ownership and control work with clarity. Learn how to organize evidence so reviewers can quickly find relevant experience and key qualifications.

A strong resume for this role connects SOX 404 IT general controls with clear examples of control testing, access reviews, audit evidence, and remediation. Use focused skills and achievement bullets to show work across audits, GRC platforms, customer due diligence, and cloud or financial systems.

The resume example is presented in 7 layouts, with PNG image previews to compare. Review each format, then open the example in the editor to explore its structure and customize the resume.

What Makes a Great Senior GRC Analyst - SOX IT Controls Resume in 2026

A strong resume makes SOX 404 and ITGC work easy to scan, with clear sections for experience, skills, education, and certifications. Specific bullets show how you tested controls, coordinated audits, and moved remediation toward closure.

Use accurate terms such as access management, change management, computer operations, SOC 2, ISO 27001, and user access reviews. Add tools and measurable outcomes only when they reflect your own work.

Note: Resume examples are for educational purposes only. Use only information that accurately reflects your experience and qualifications. References to real organizations do not imply affiliation or endorsement.

#1 Plain Two Column Format Resume Example

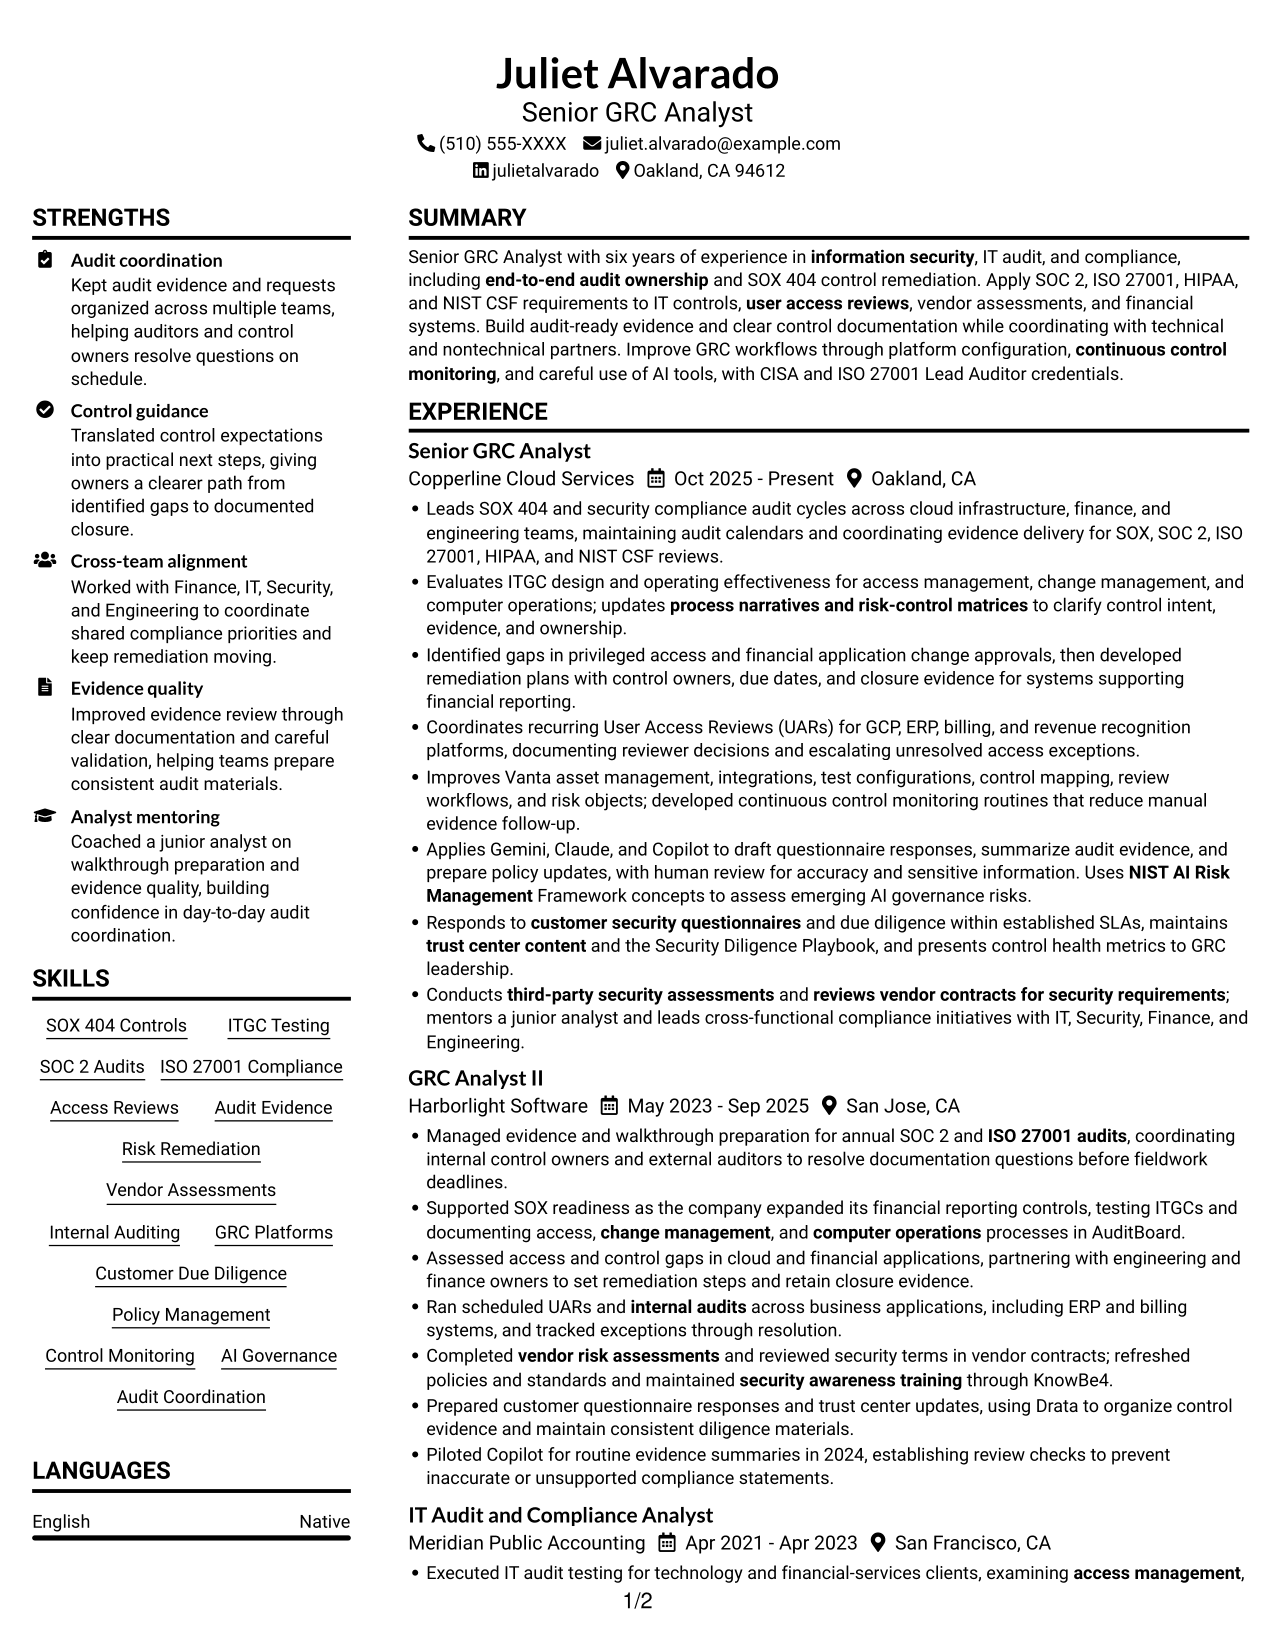
Plain Two Column Format places resume content in two columns, giving reviewers a divided reading path through the sections.
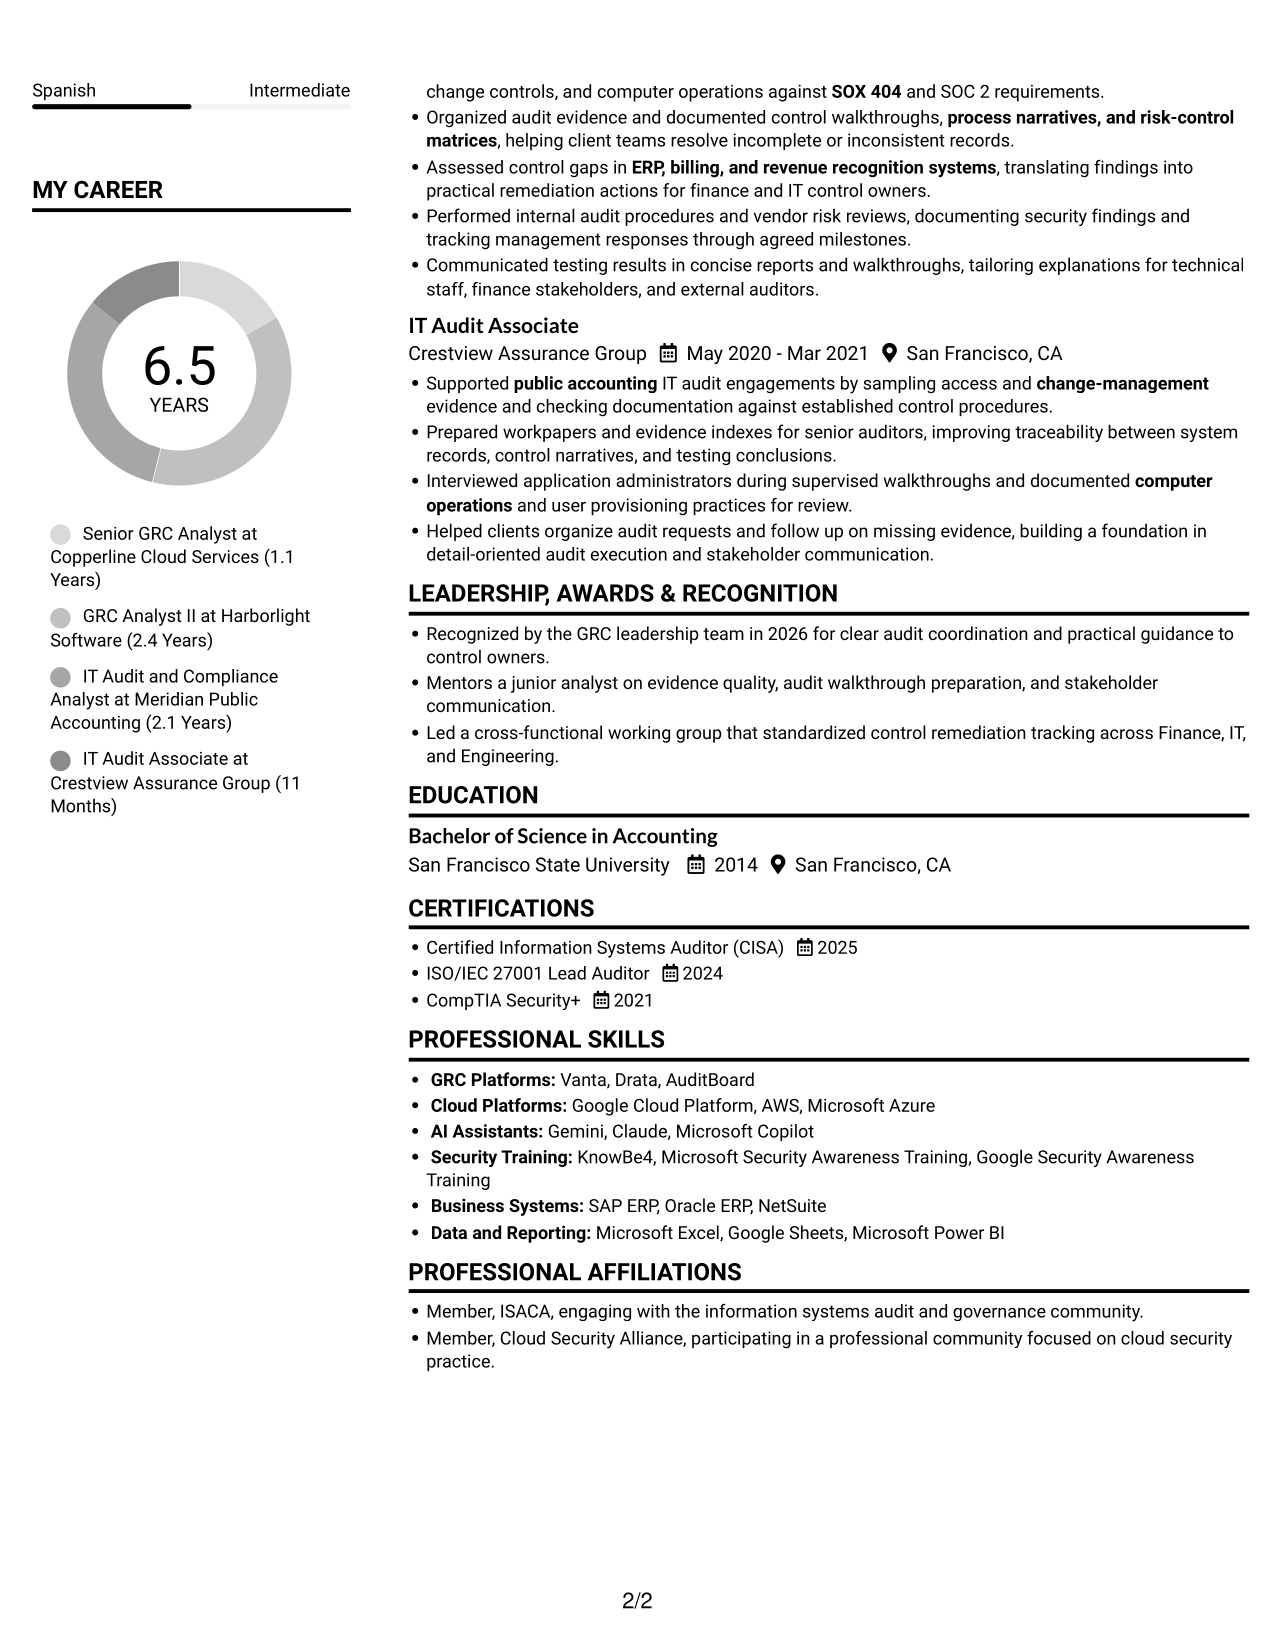
 
Resume example — page 1   Resume example — page 2

Resume Snapshot

  • Six years in information security, IT audit, and compliance
  • End-to-end audit ownership and SOX 404 remediation
  • CISA and ISO/IEC 27001 Lead Auditor credentials
  • Experience across GRC platforms, cloud systems, and financial applications

Why This Format Works

  • The two-column reading order lets reviewers move between career history and supporting sections.
  • Separate column areas can keep skills visible beside more detailed experience entries.
  • Education and credentials remain easy to locate among the resume's other sections.

Best For

  • Resumes with several distinct sections
  • Longer work histories beside supporting details
  • Skills and credentials needing quick access
  • Reviews that compare experience across roles
  • Readers who prefer divided content areas

Resume Keywords

  • six years of experience in information security, IT audit, and compliance
  • end-to-end audit ownership
  • SOX 404
  • Evaluates ITGC design and operating effectiveness
  • SOC 2
  • ISO 27001
  • HIPAA
  • NIST CSF
  • Evaluates ITGC design and operating effectiveness for access management, change management, and computer operations
  • Identified gaps in privileged access and financial application change approvals, then developed remediation plans with control owners, due dates, and closure evidence for systems supporting financial reporting.
  • user access reviews
  • vendor risk assessments
  • internal audits
  • AuditBoard
  • Managed evidence
See all keywords
 

#2 Simple One Column Format Resume Example

Simple One Column Format keeps the resume body in one column, so reviewers can follow each section from top to bottom.
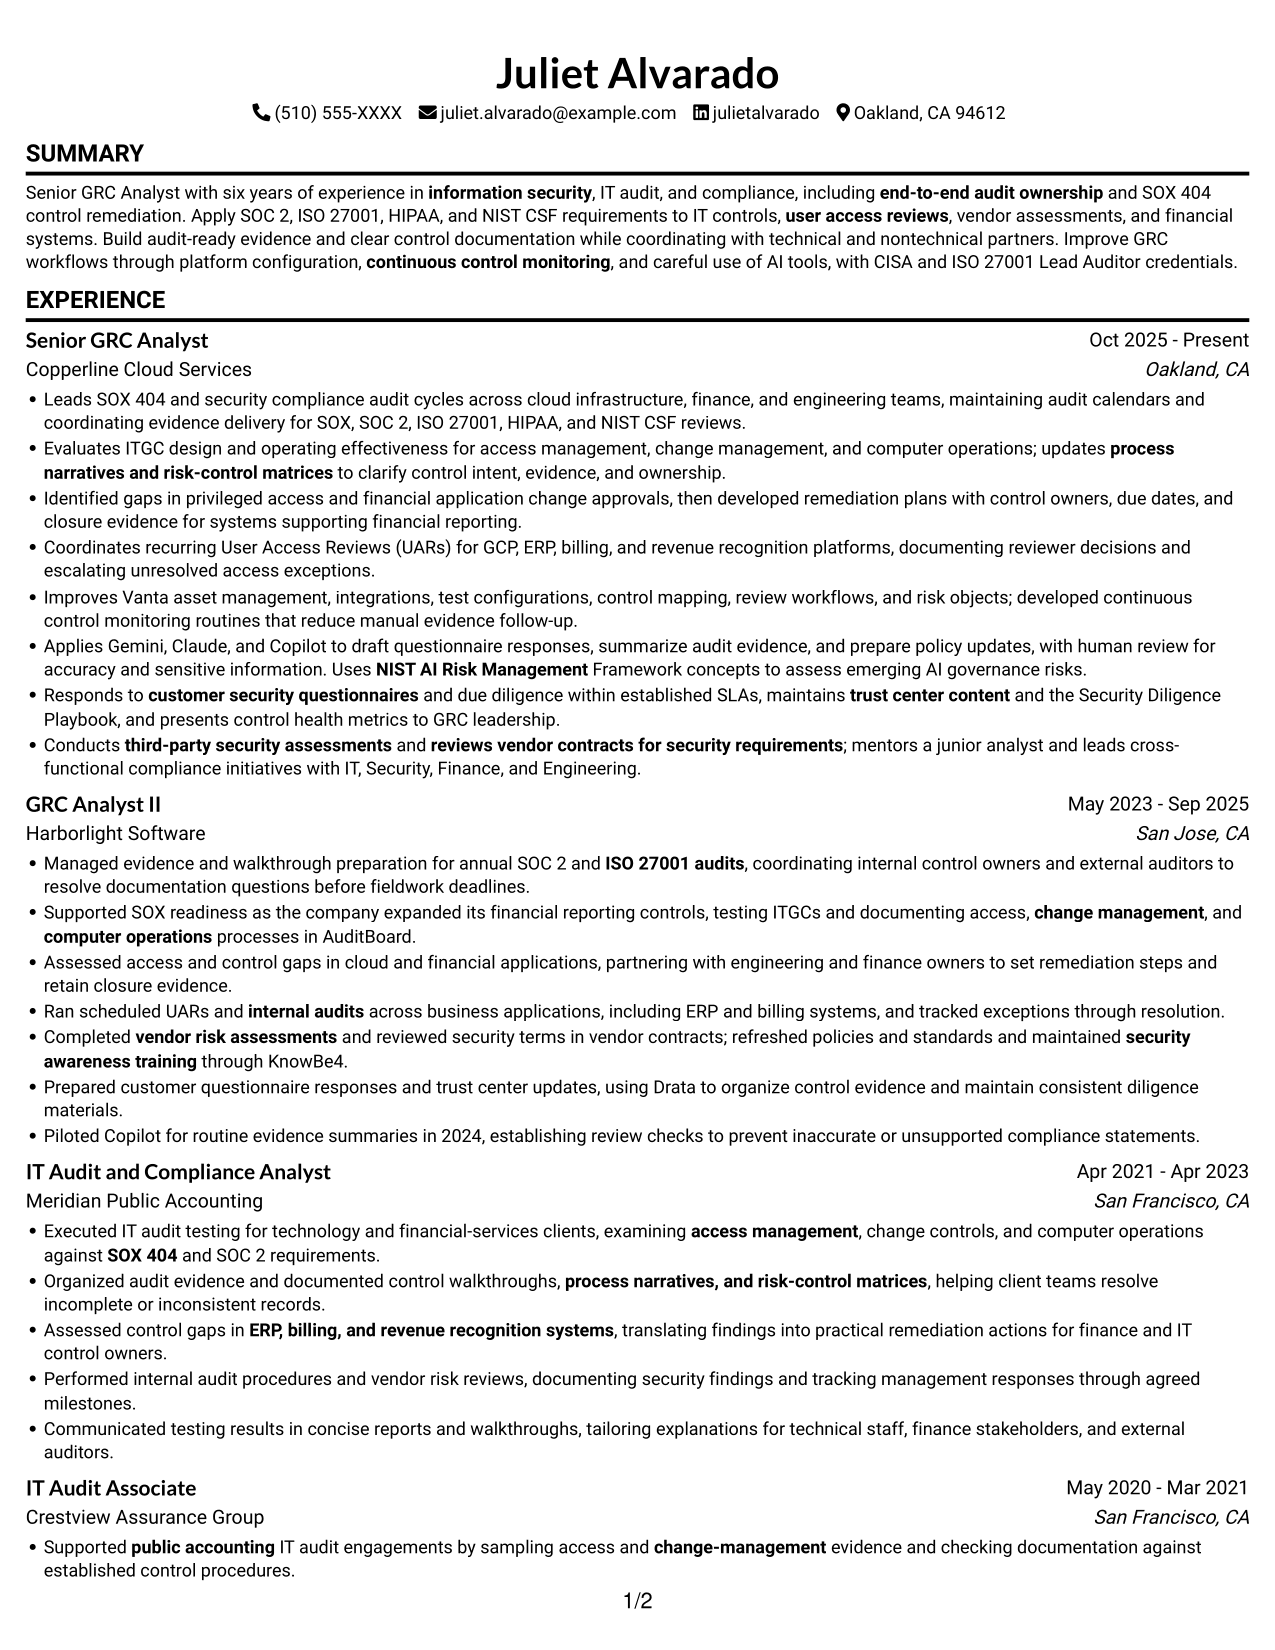
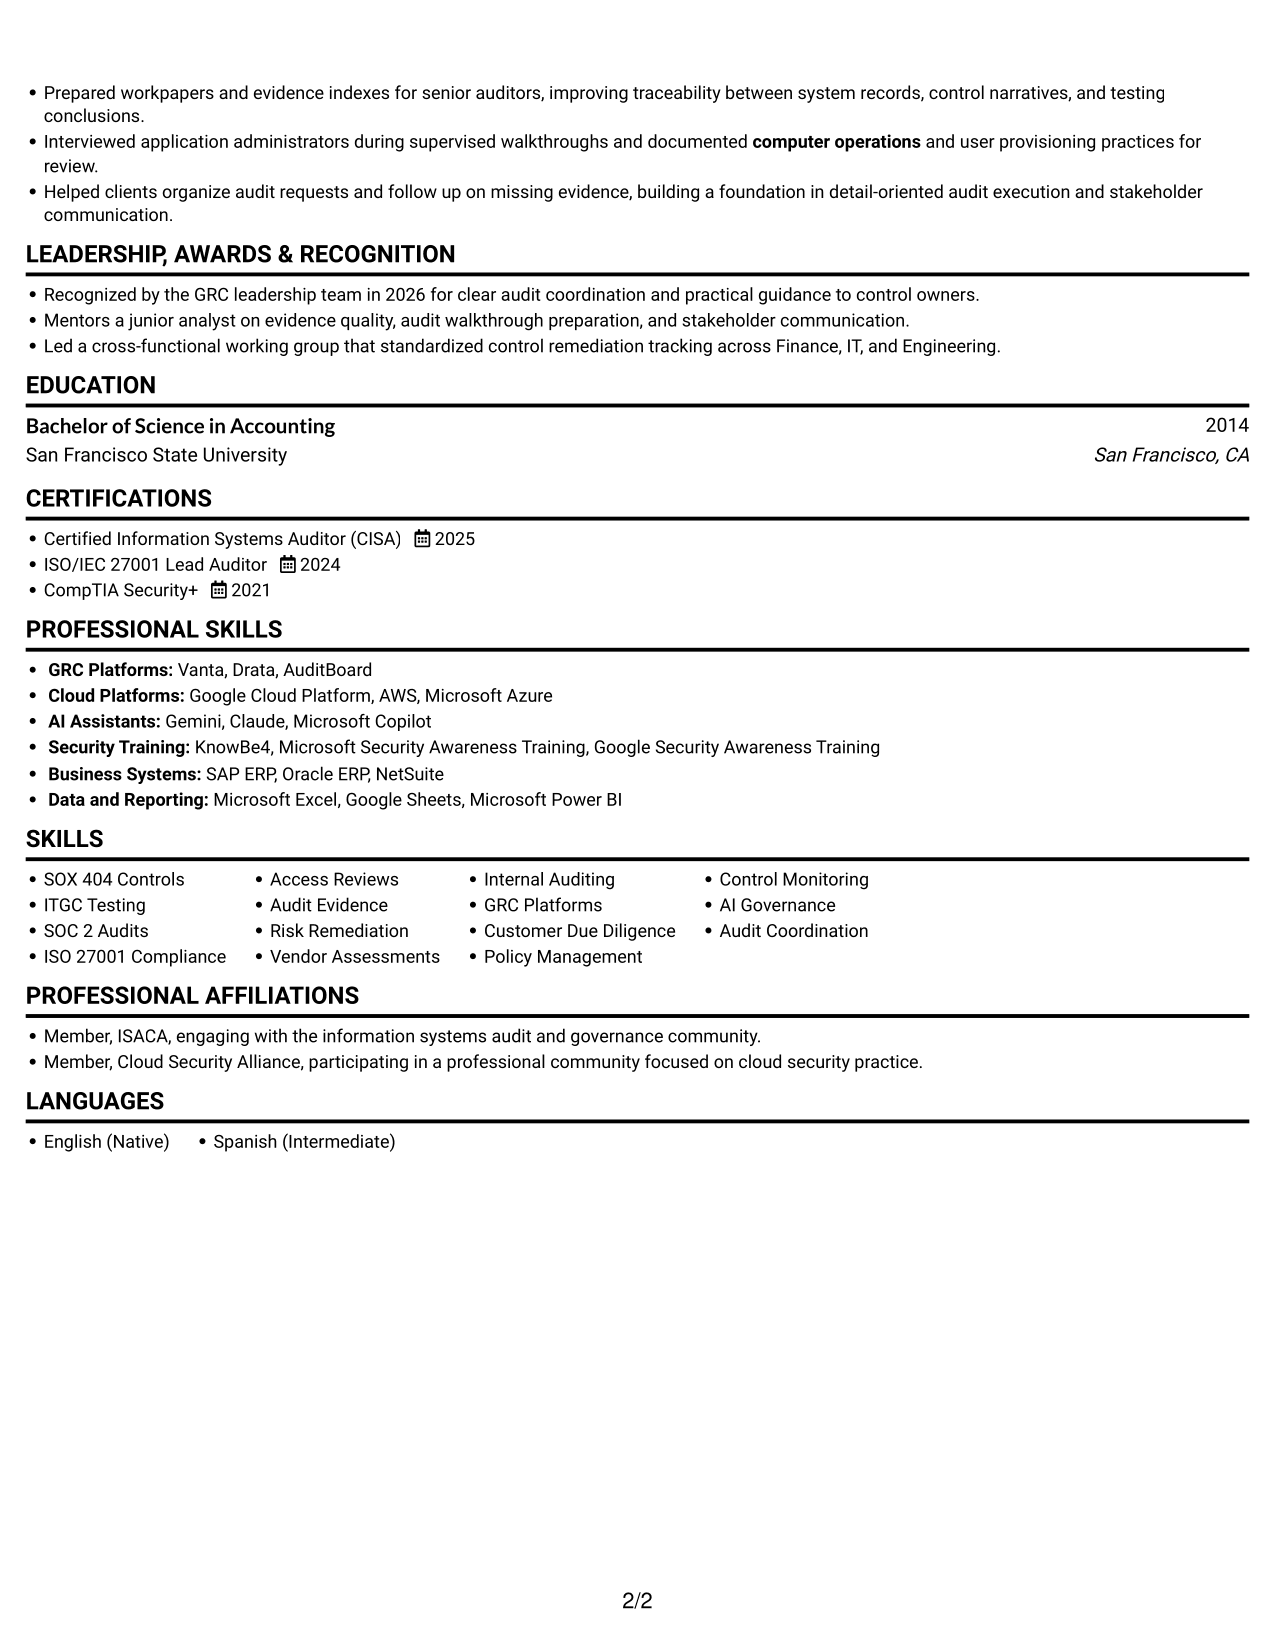
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • One vertical reading path lets reviewers follow experience in sequence without switching columns.
  • Skills and credentials can appear as distinct sections within the same clear flow.
  • Section headings can lead reviewers from work history to education and credentials.

Best For

  • Top-to-bottom resume review
  • Work histories presented in sequence
  • Detailed experience entries
  • Clear section-by-section reading
  • Distinct skills and credential sections
 

#3 Clean Two Column Sidebar Format Resume Example

Clean Two Column Sidebar Format uses two body columns to give reviewers a clear way to move among resume sections.
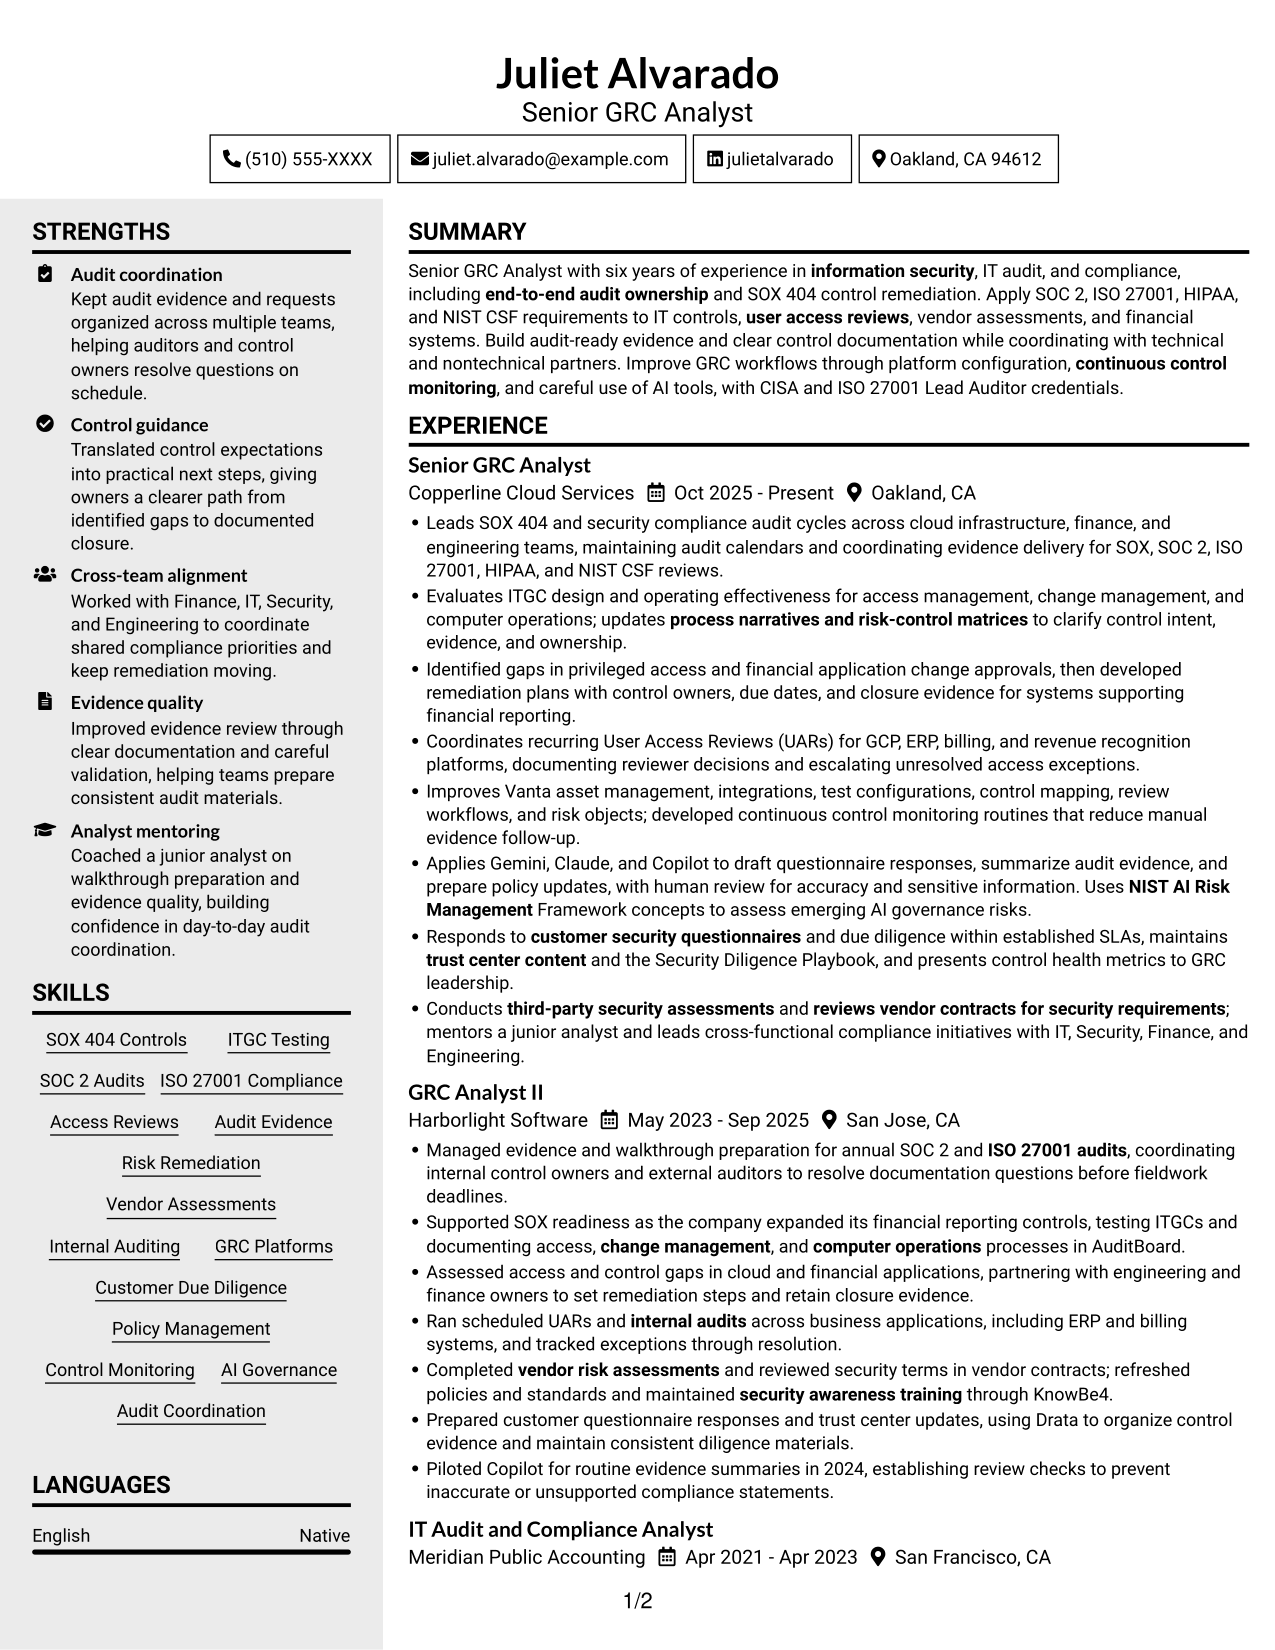
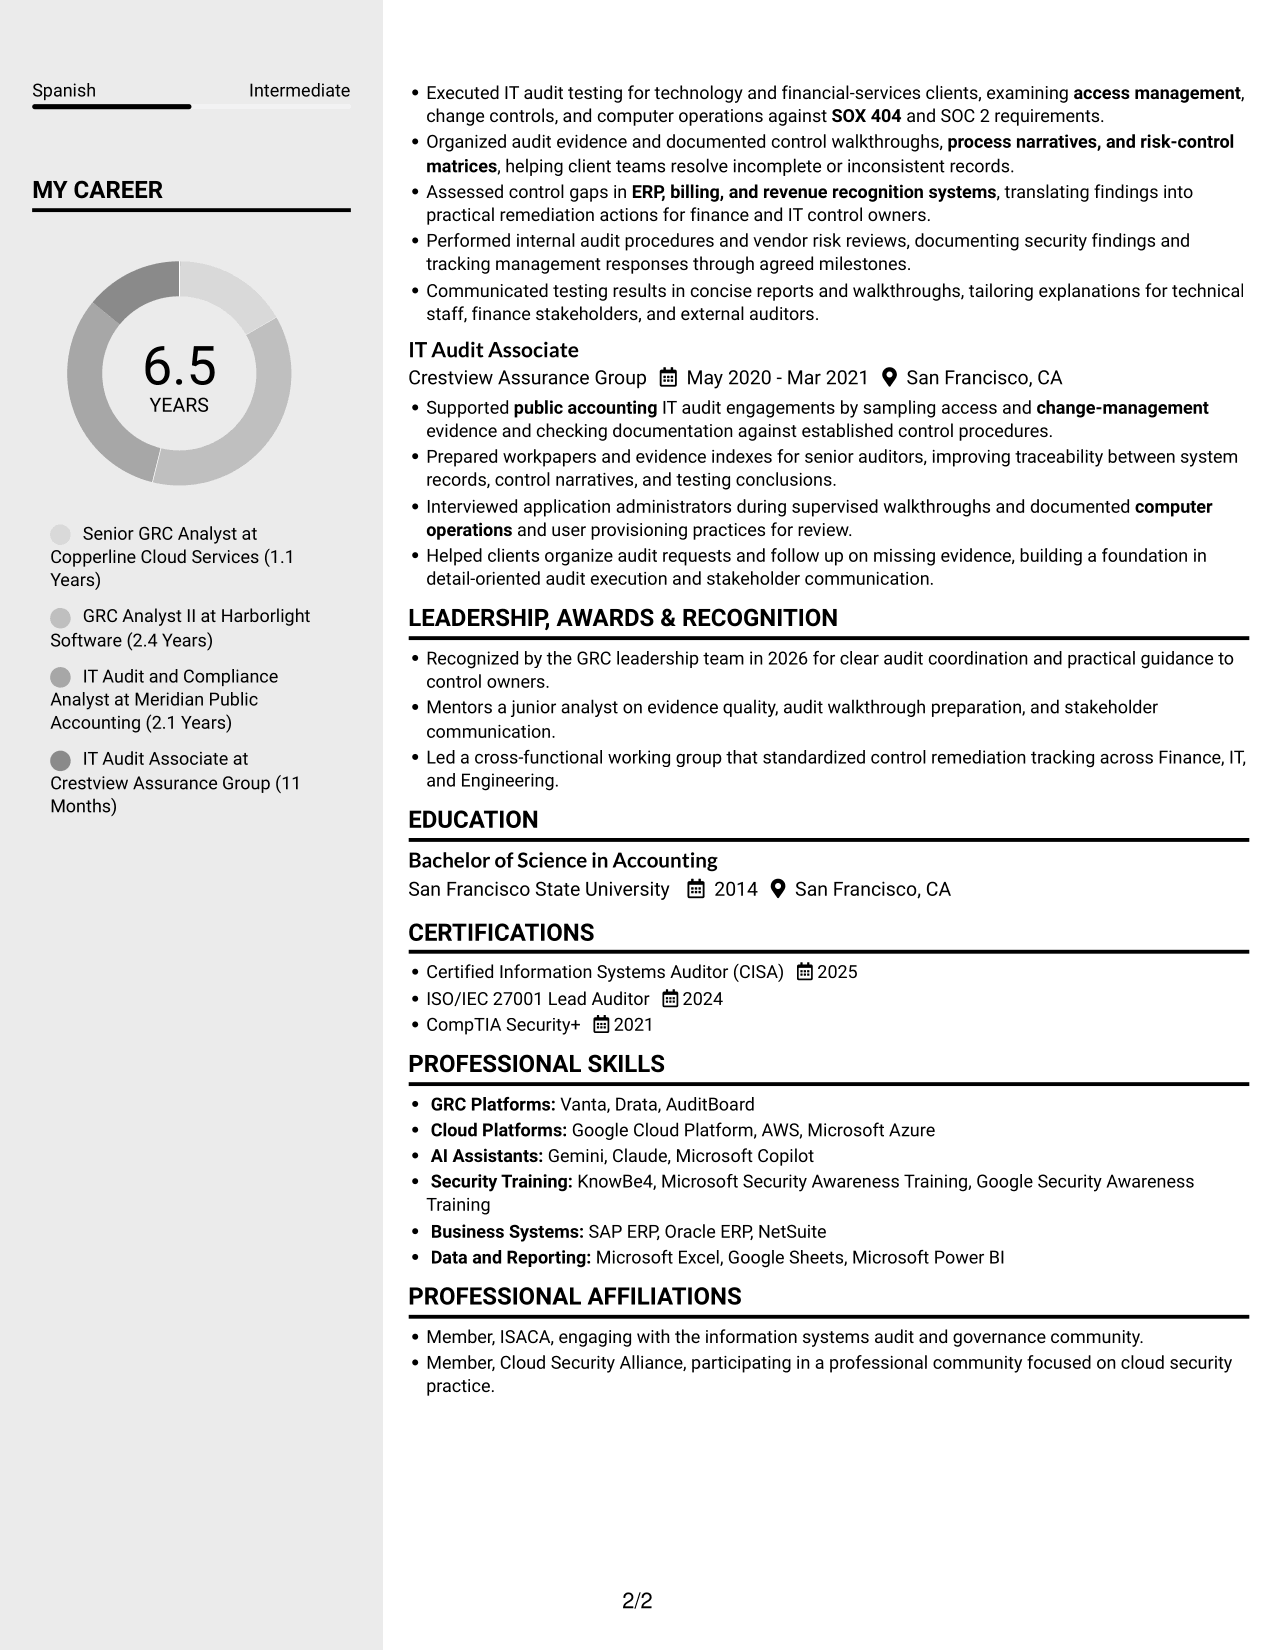
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two columns give reviewers separate areas for career history and supporting sections.
  • Skills can be located apart from detailed experience entries in the divided layout.
  • Education and credentials remain part of the same organized resume for review.

Best For

  • Resumes with several section types
  • Career histories paired with supporting details
  • Separate skills and experience areas
  • Readers comparing roles and credentials
  • Applications with varied resume sections
 

#4 Two Column Format Resume Example

Two Column Format presents resume content in two columns, a practical choice when readers need to navigate several sections.
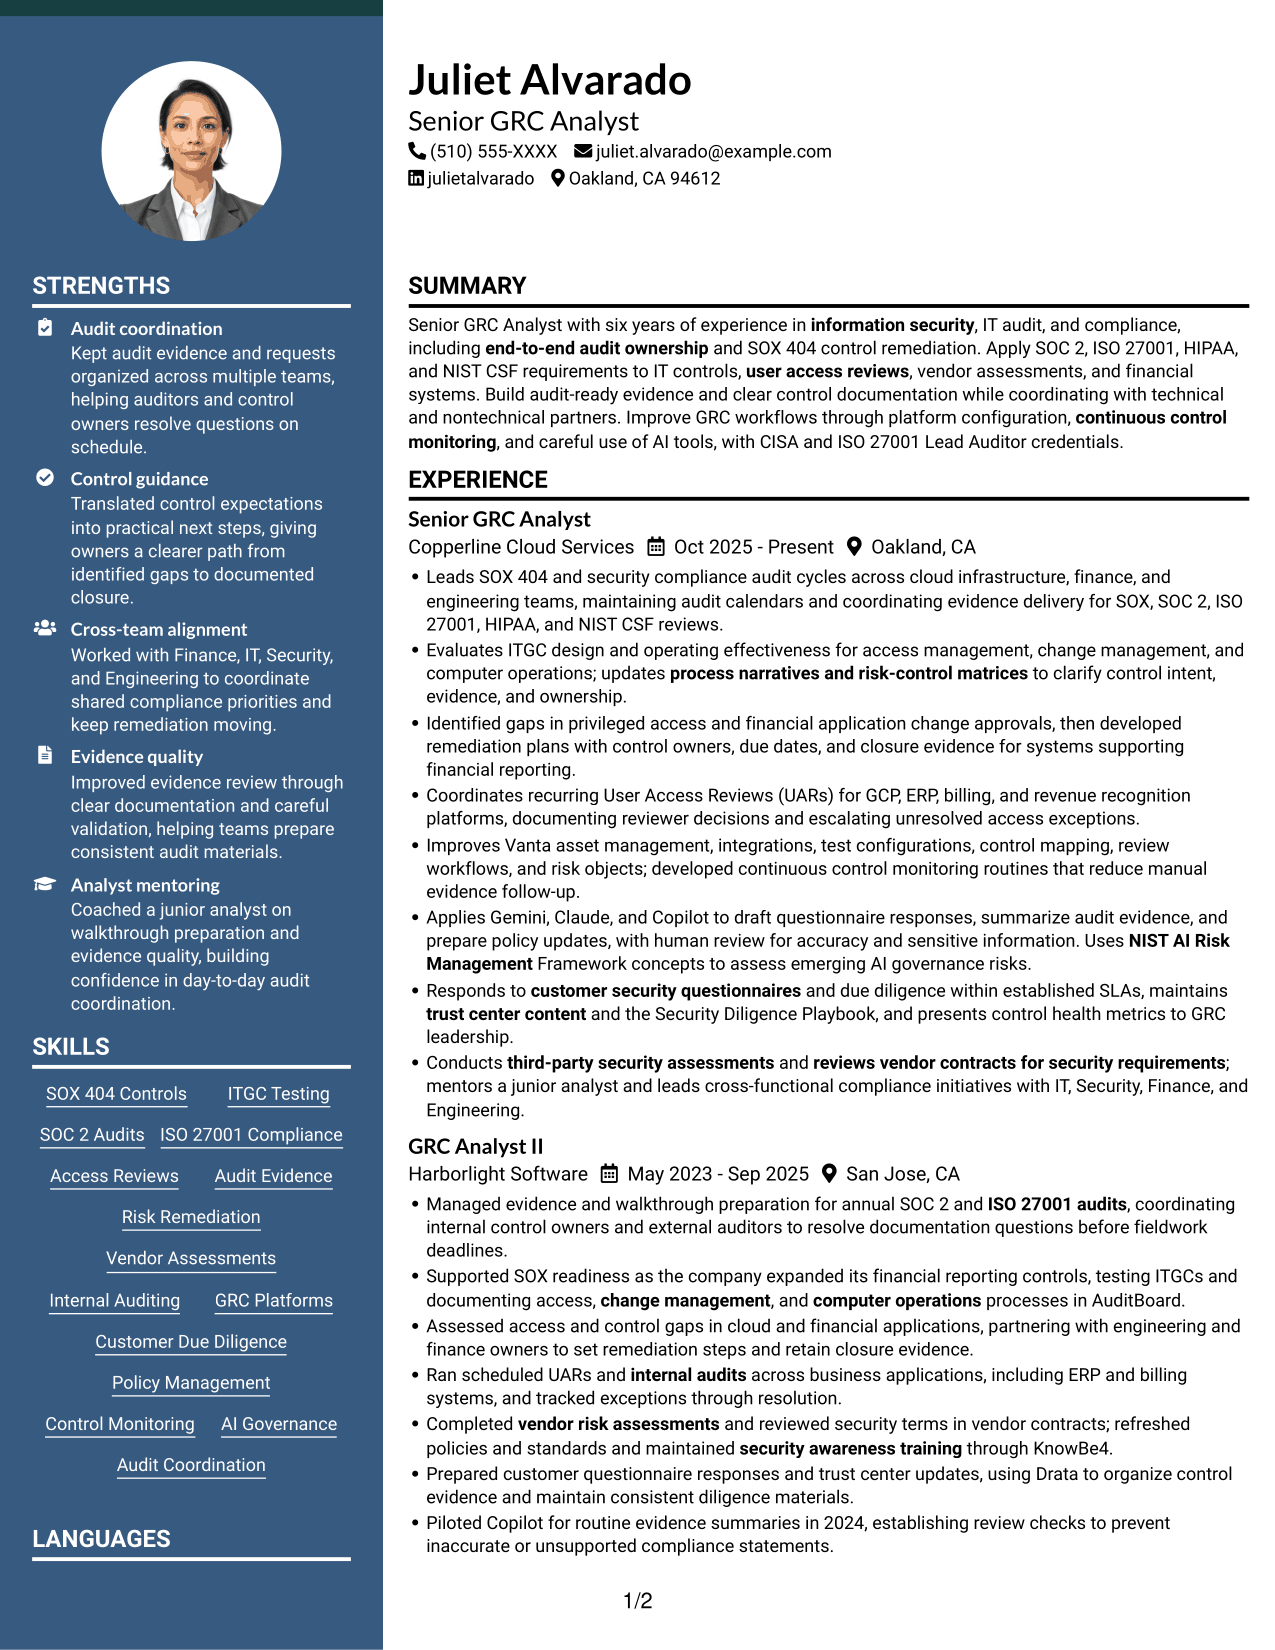
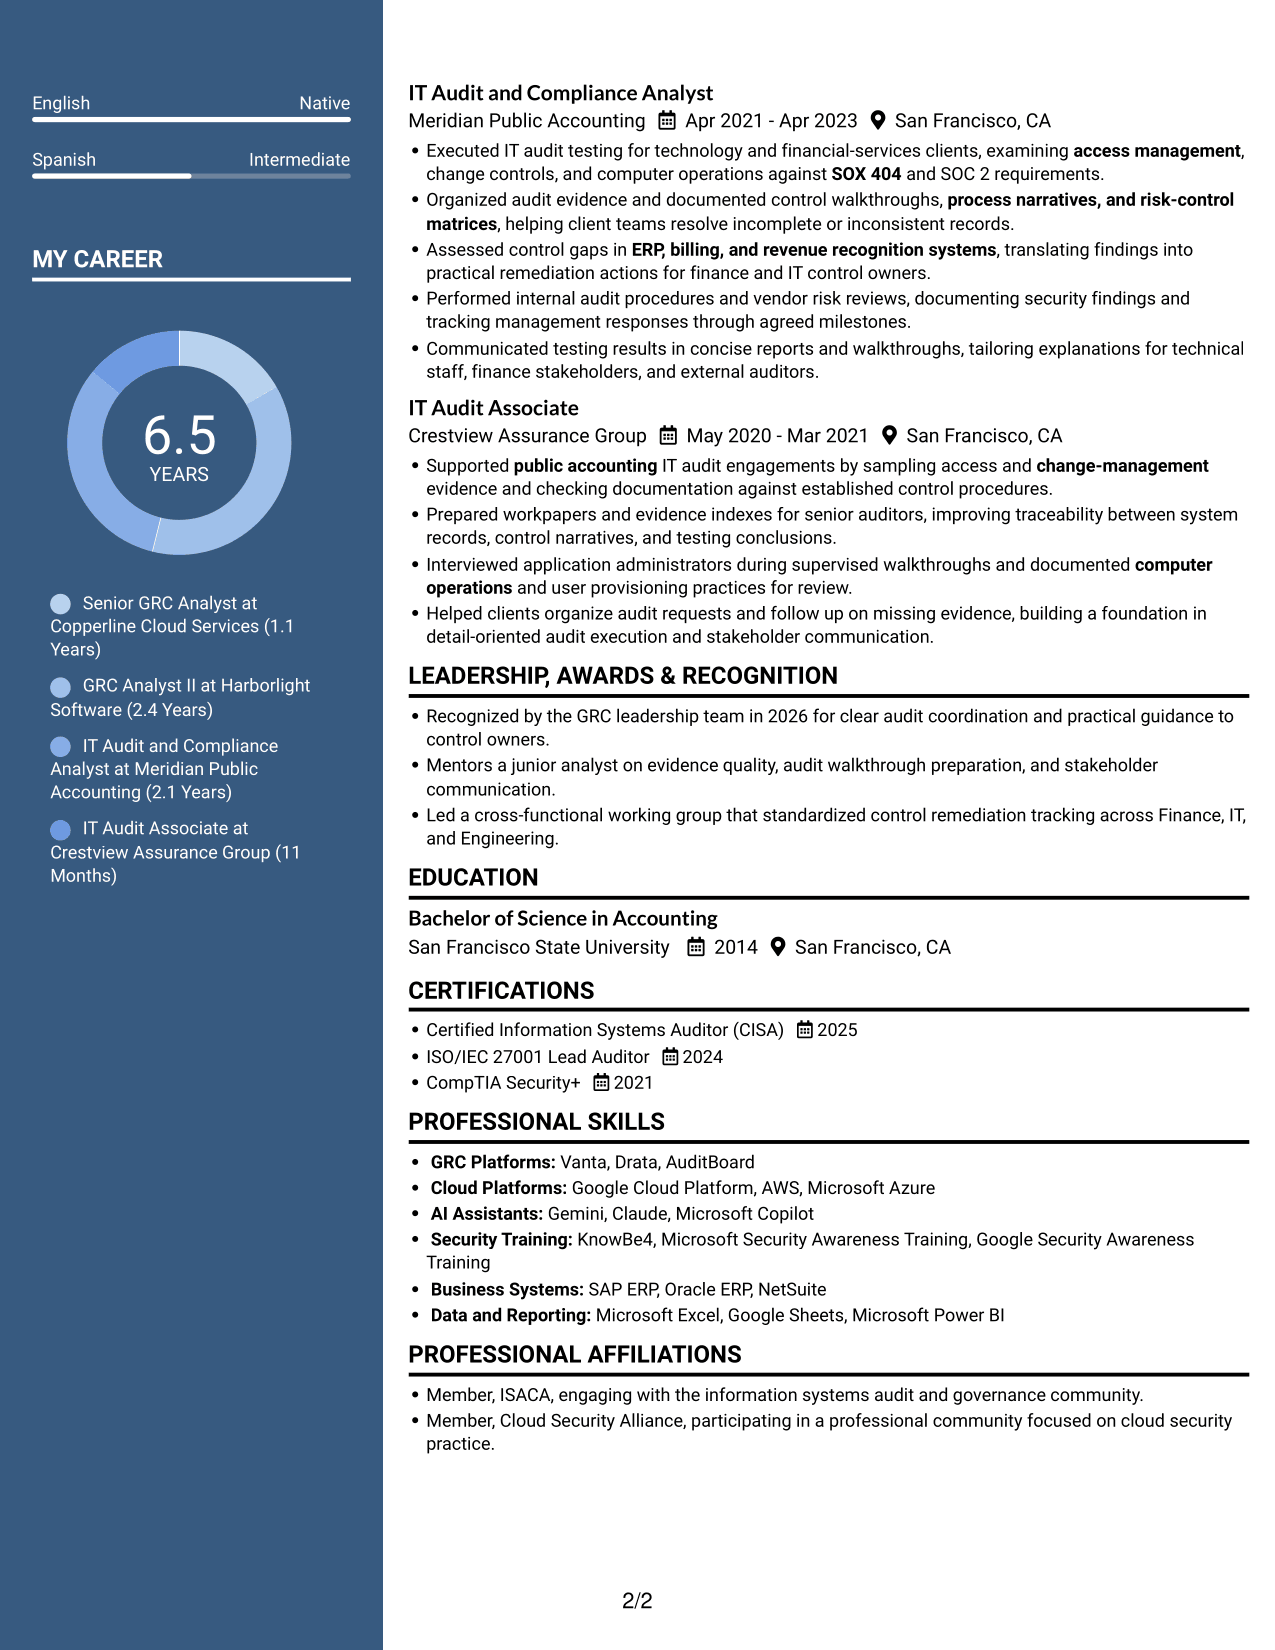
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Reviewers can move between work history and supporting sections across two columns.
  • Column separation helps keep skills distinct from detailed career entries.
  • Education and credentials have defined places within the resume's section structure.

Best For

  • Multi-section resume content
  • Work history with supporting details
  • Skills kept apart from long entries
  • Quick access to education and credentials
  • Readers scanning several content areas


#5 Photo Header Two Column Format Resume Example

Photo Header Two Column Format pairs a photo header with a two-column body, combining a personal image with divided section navigation.
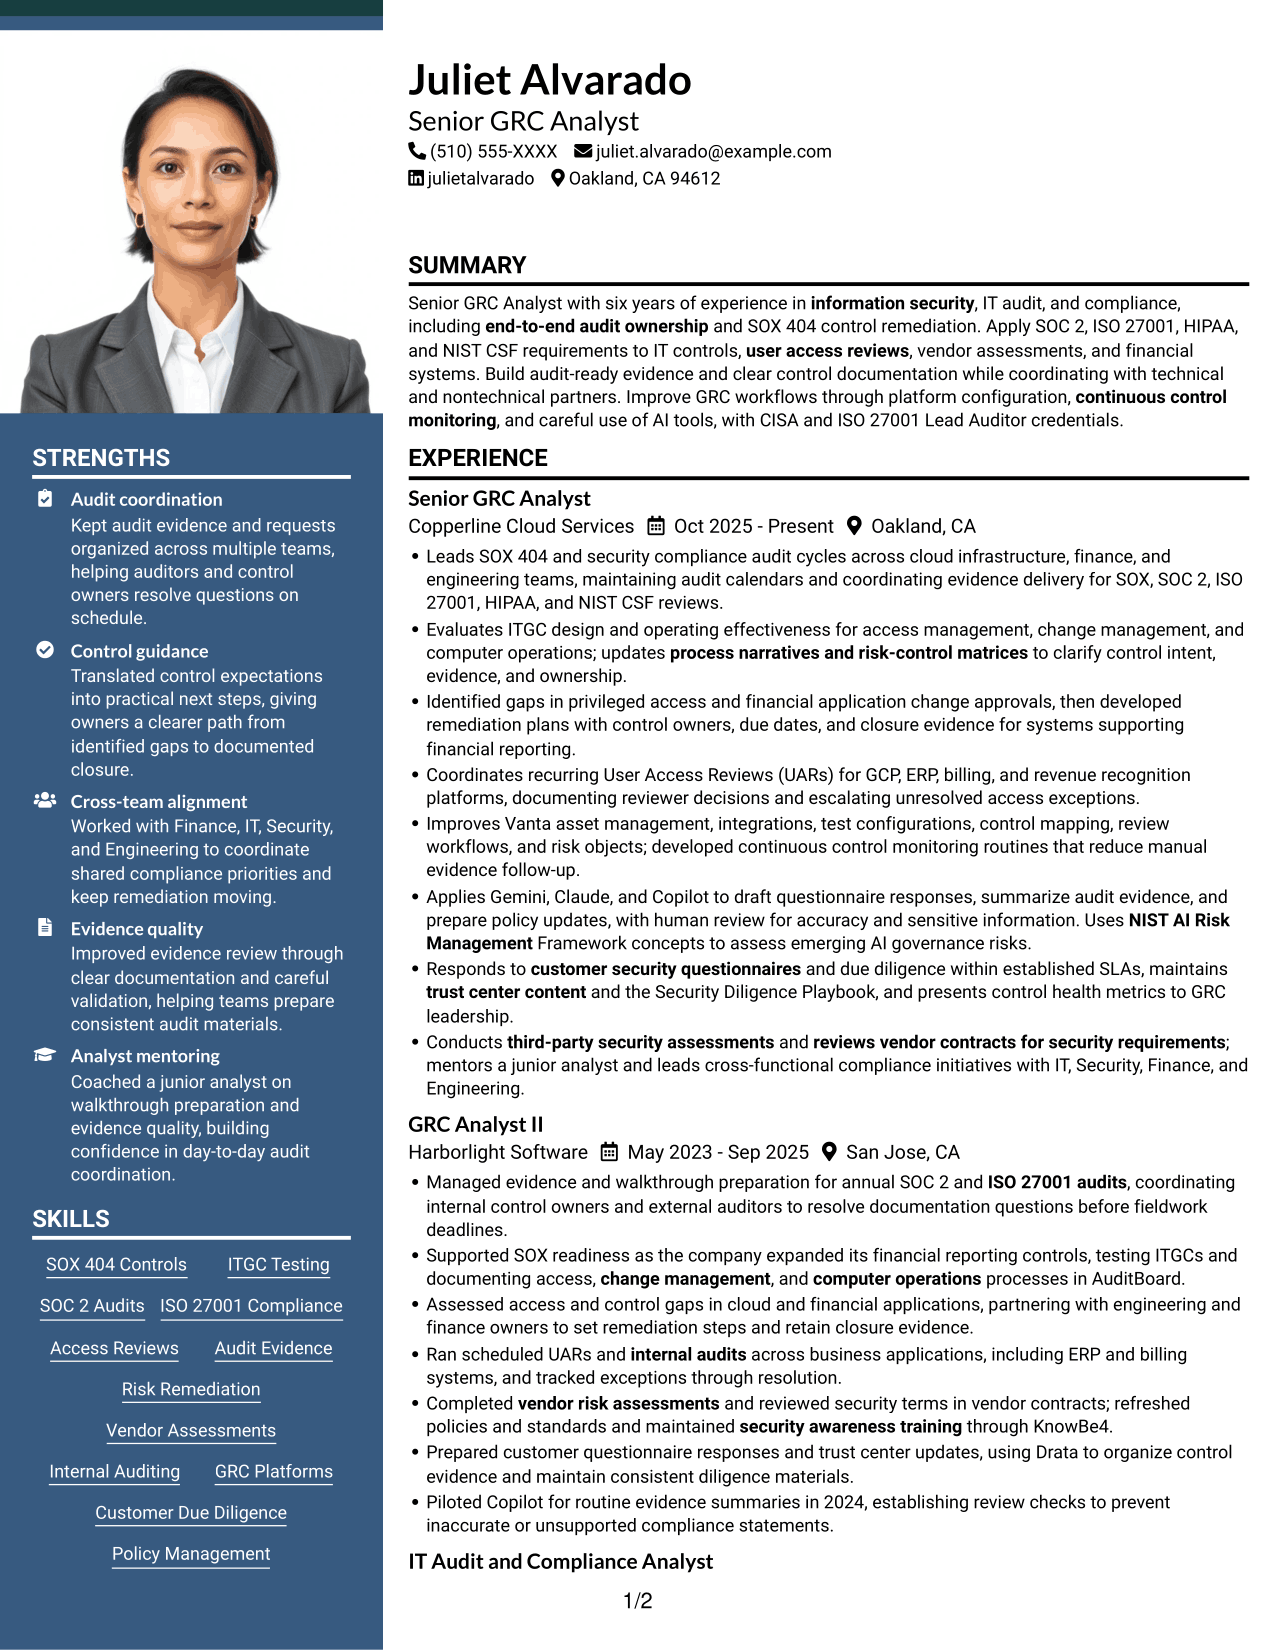
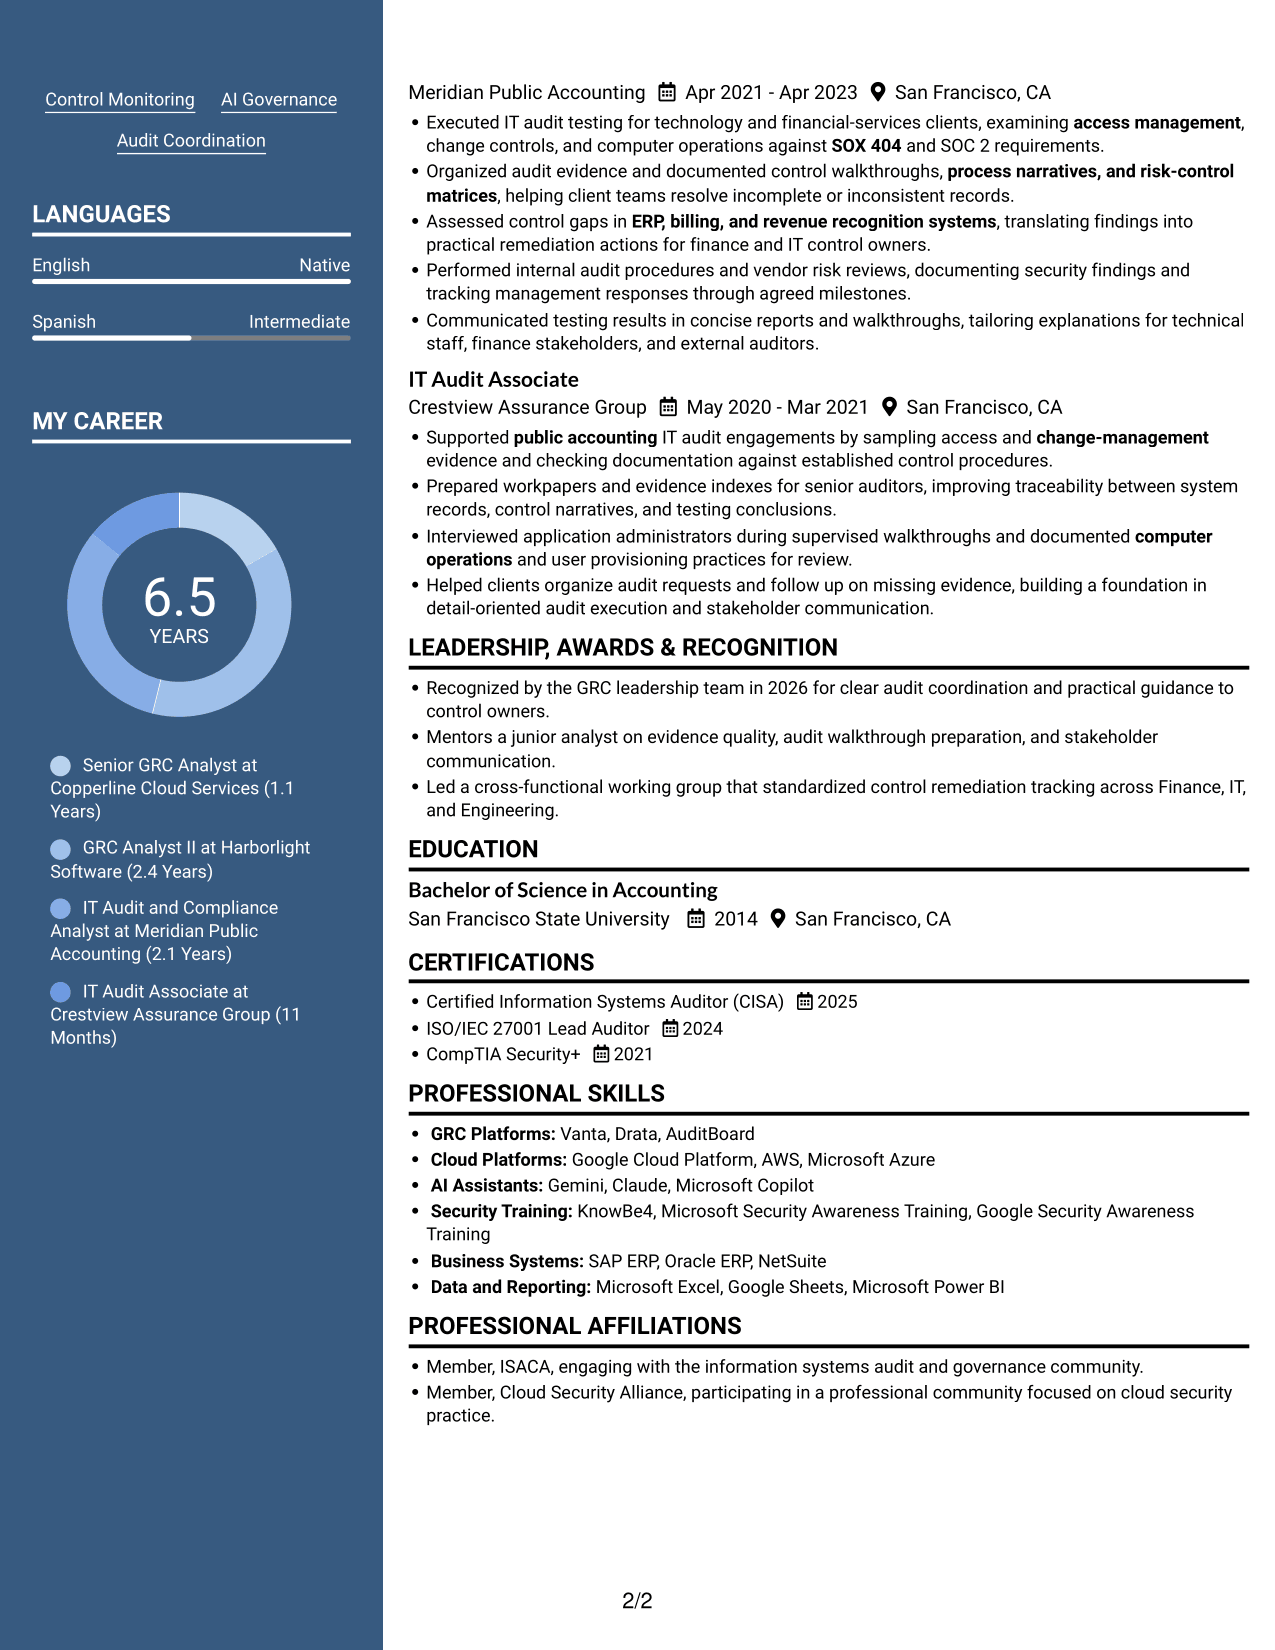
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • The two-column body gives work history and supporting information distinct reading areas.
  • Reviewers can find skills without losing the sequence of experience entries.
  • Education and certifications stay within the same resume alongside its career record.

Best For

  • Resumes using a photo header
  • Two-column section organization
  • Career histories with supporting information
  • Experience entries kept in sequence
  • Readers who prefer a photo presentation
 

#6 Colored Two Column Format Resume Example

Colored Two Column Format organizes the resume body in two columns, giving reviewers a divided route through its content.
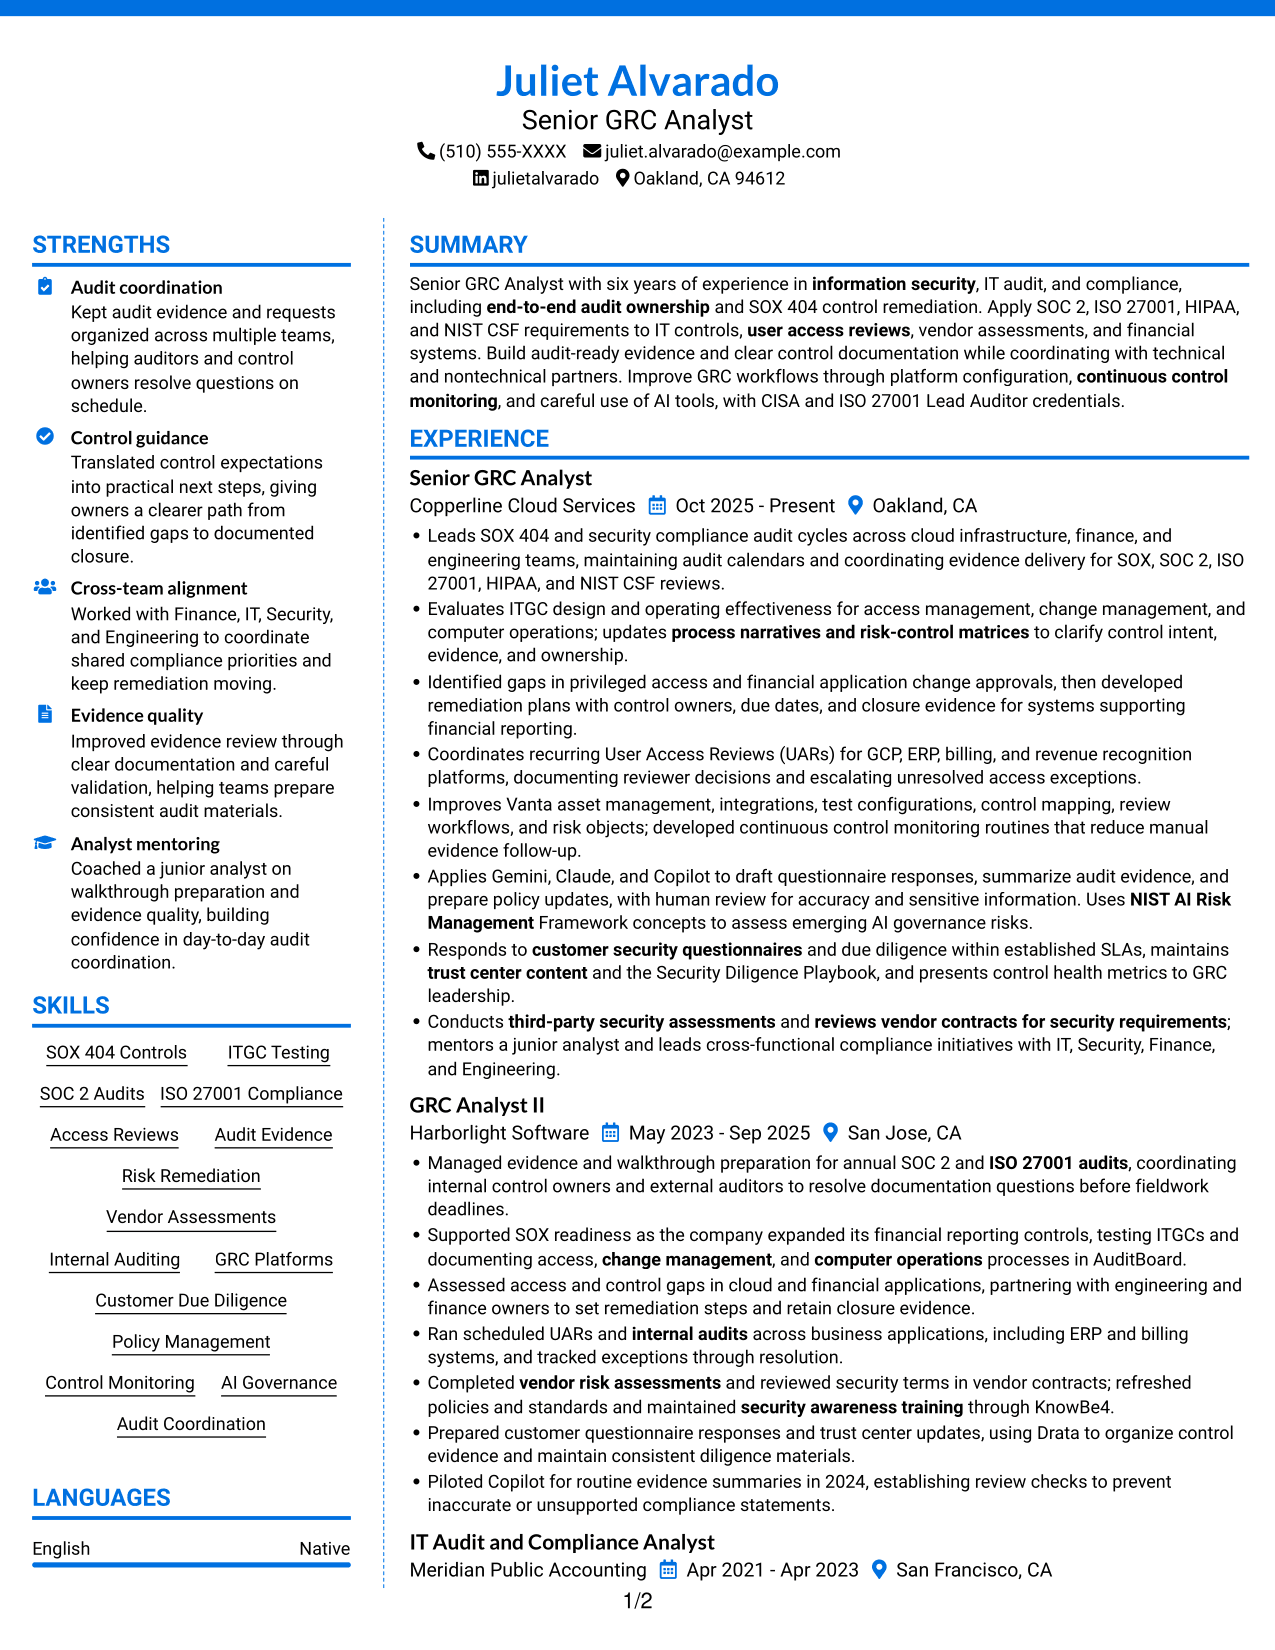
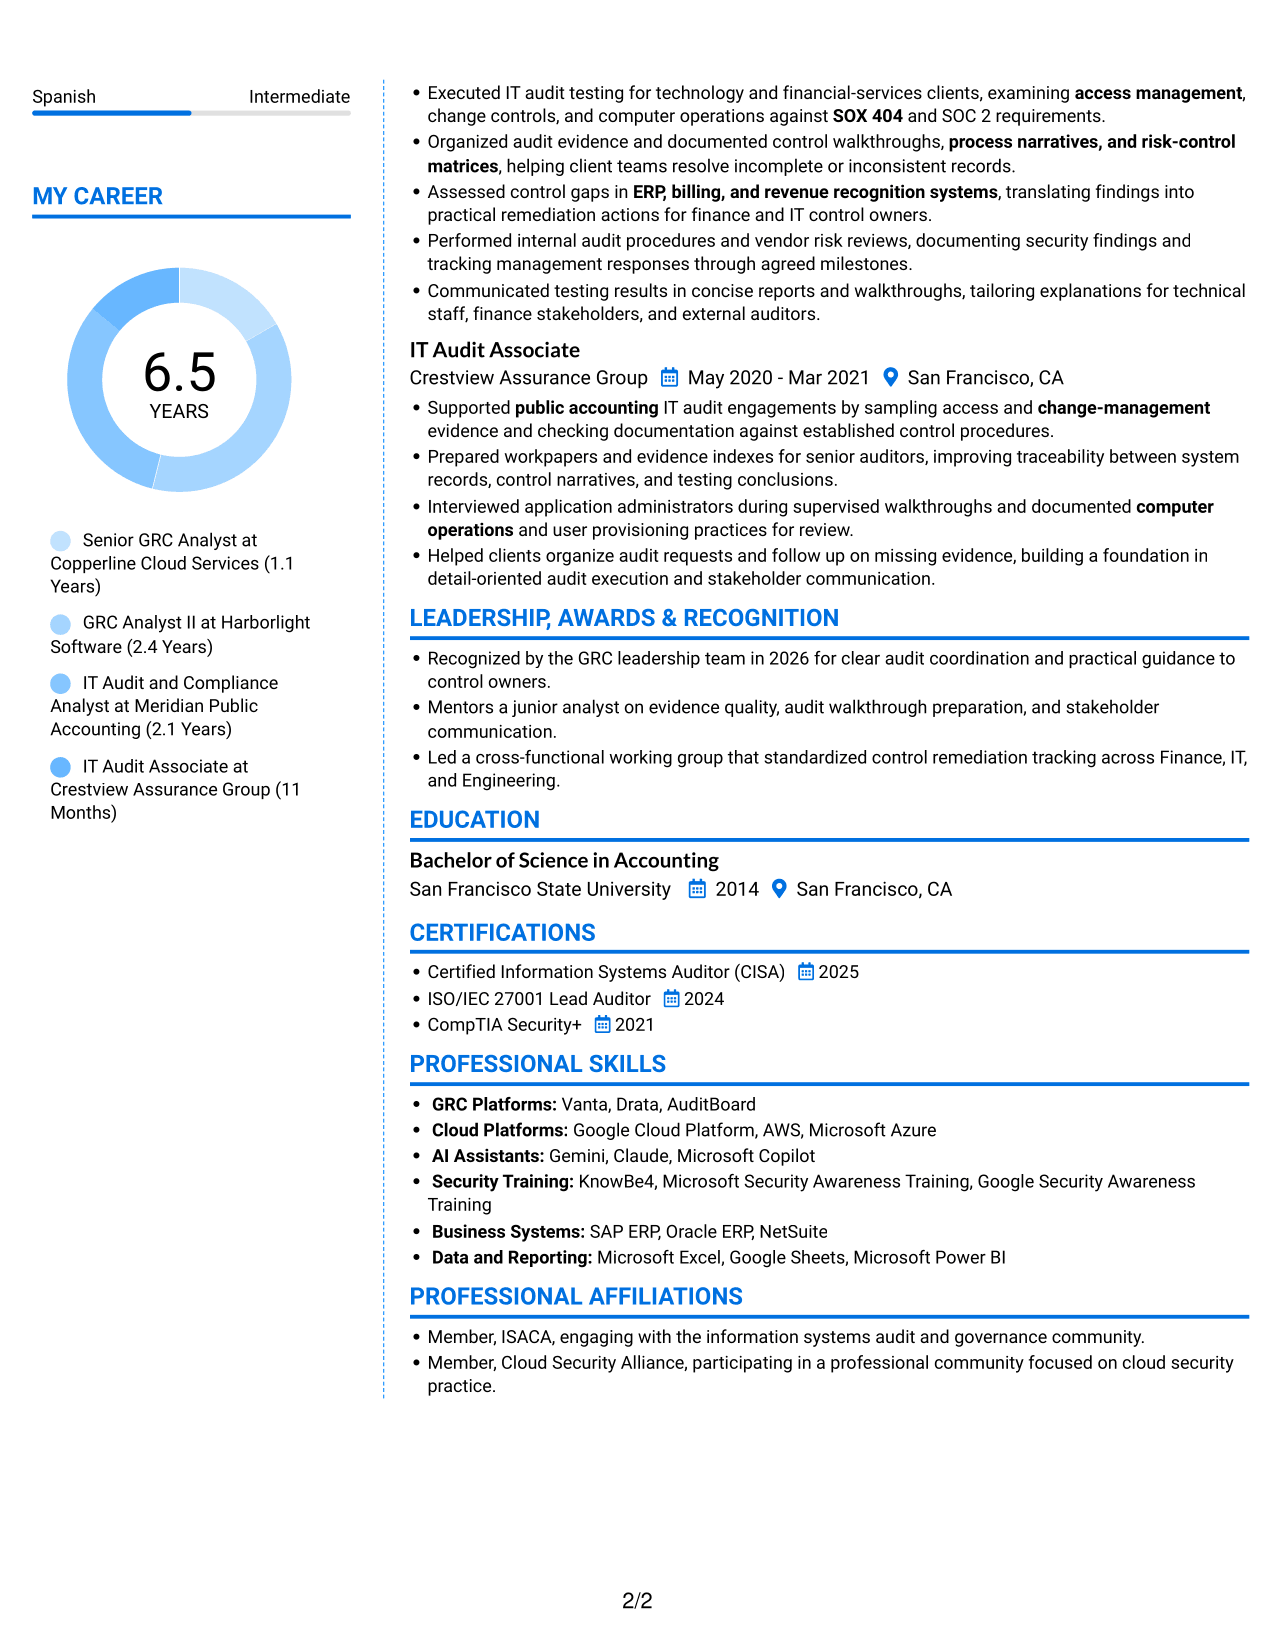
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two body columns let reviewers compare career history with other resume sections.
  • Skills and credentials can occupy a distinct area from longer experience details.
  • Education remains easy to locate without interrupting the work history sequence.

Best For

  • Divided resume content
  • Several sections to review
  • Detailed experience alongside other information
  • Skills and credentials in distinct areas
  • Readers comparing education with work history
 

#7 Stylish Two Column Designer Format Resume Example

Stylish Two Column Designer Format uses two columns to distinguish resume sections while keeping the content organized for review.
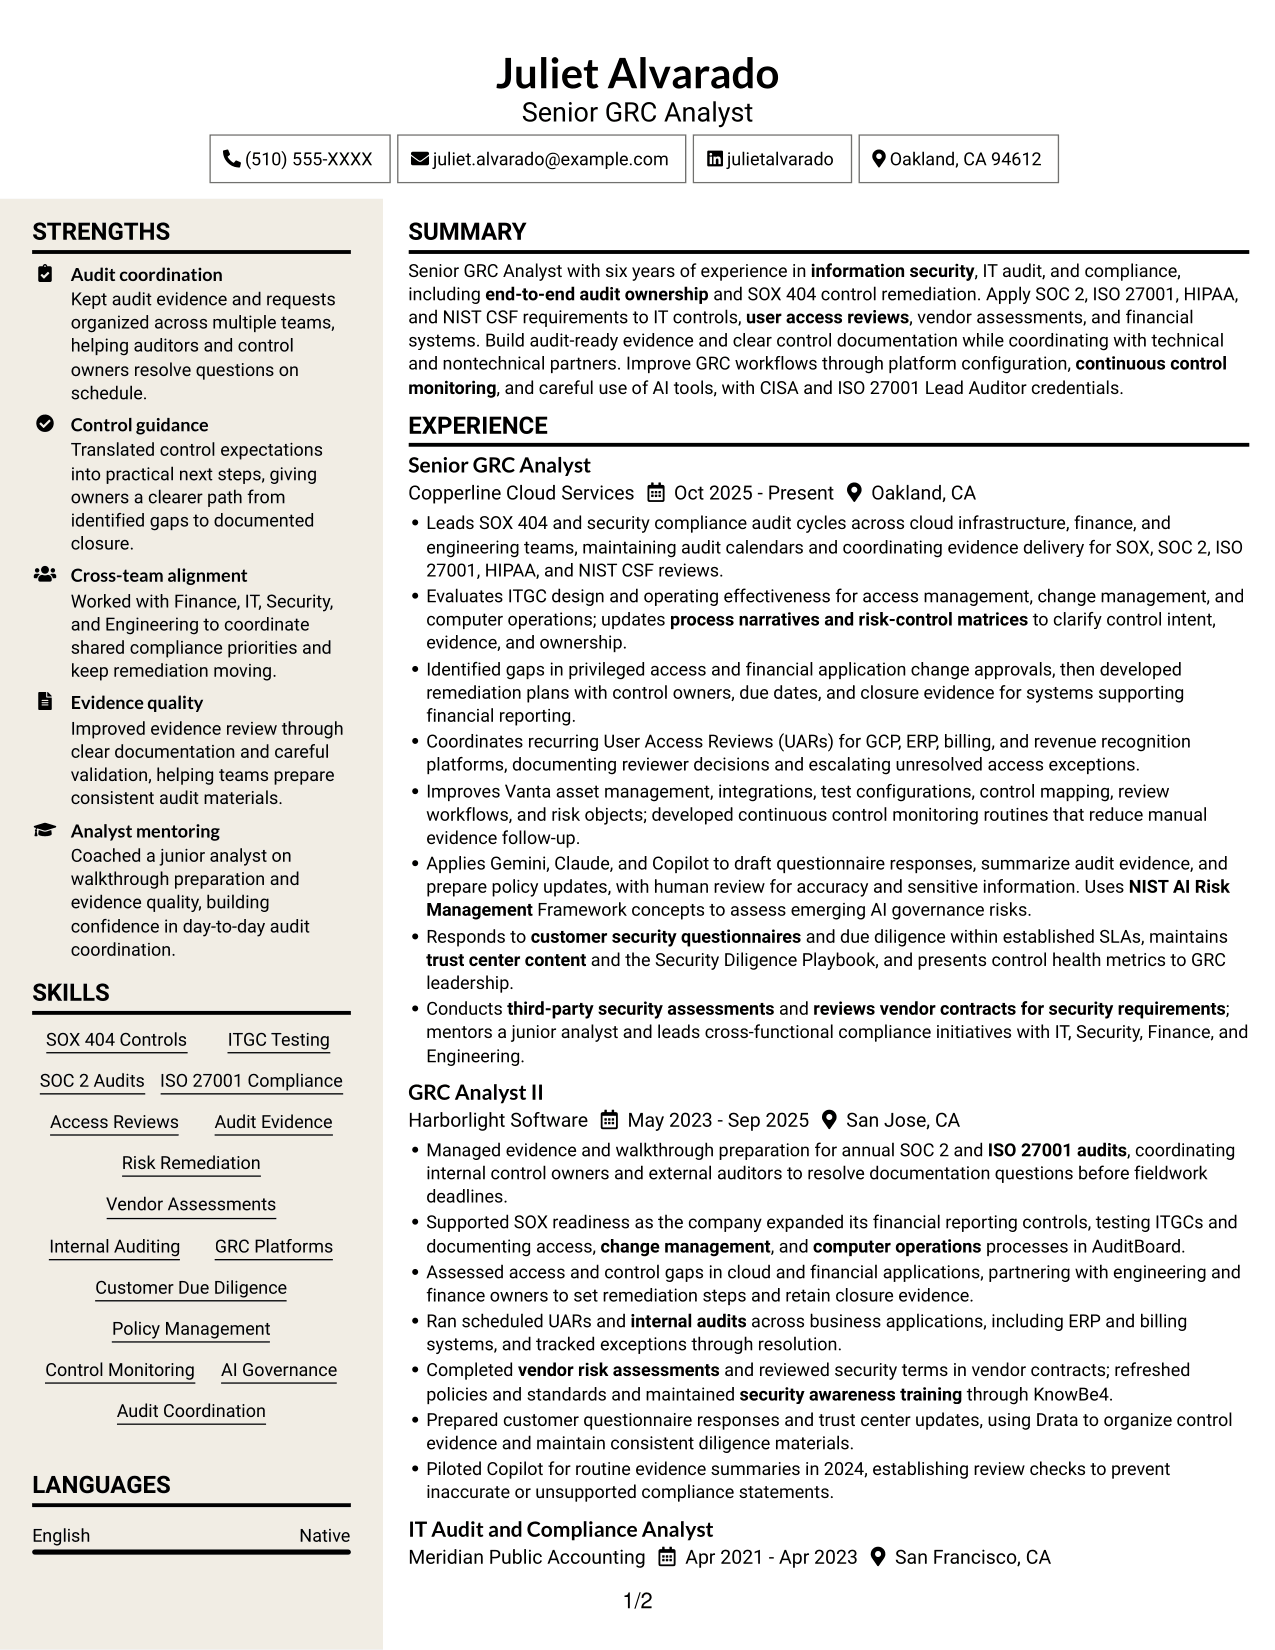
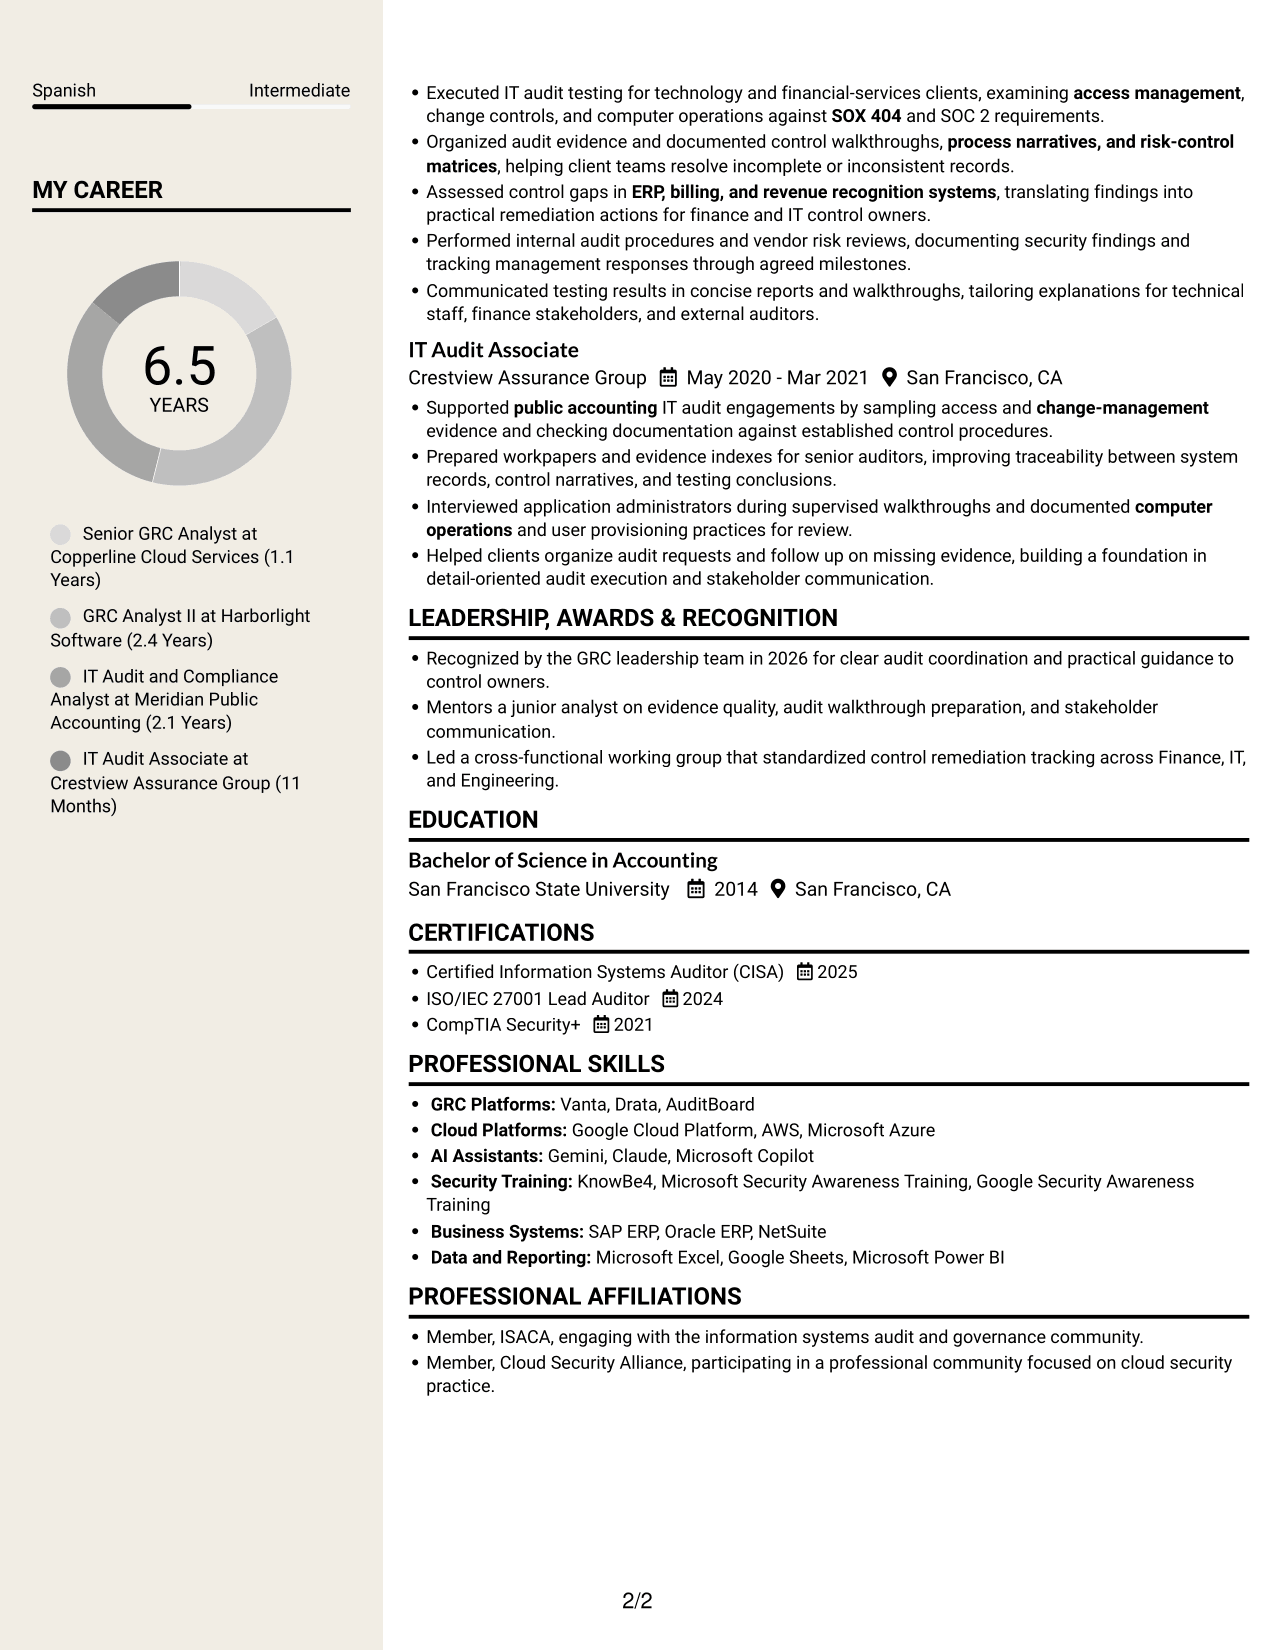
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Reviewers can scan work history and supporting sections through a divided page structure.
  • Column organization keeps skills distinct from the detail in experience entries.
  • Separate content areas help reviewers locate education and credentials during review.

Best For

  • Two-column resume organization
  • Work histories with supporting sections
  • Experience details alongside skills
  • Readers locating credentials across sections
  • Resume reviews that compare career stages


Why Build Your Senior GRC Analyst - SOX IT Controls Resume with ResumeInMinutes

ResumeInMinutes helps you arrange GRC experience, audit evidence, control skills, and certifications in a clear resume. Compare the PNG image previews, then open an example in the editor to review its layout and customize your content.

  • Professional resume layouts
  • Clear, ATS-aware section structure
  • Role-specific control and audit keywords
  • Organized skills and platform details
  • PNG image previews
  • Resume editing in the editor

Use concise bullets to connect SOX 404 control work with the evidence, decisions, and results you can support. Keep each section focused on the qualifications most relevant to the Senior GRC Analyst - SOX IT Controls role.


See Also


Frequently Asked Questions

Are these Senior GRC Analyst - SOX IT Controls resume templates ATS-friendly?

The examples use clear section labels and readable content. For stronger ATS matching, include accurate terms from your experience, such as SOX 404, ITGC testing, access reviews, audit evidence, and control remediation.

Do these examples show different candidates?

No. The page presents one resume example in different layouts. Compare the PNG image previews to see how each design arranges the same type of information.

What should a Senior GRC Analyst - SOX IT Controls resume include?

Include a focused summary, relevant work experience, skills, education, and certifications. Show examples of SOX 404 and ITGC work, audit cycles, user access reviews, evidence management, and remediation when these match your background.

Which resume format works well for this role?

A simple layout with familiar headings helps reviewers and ATS tools find your experience and skills. Choose a format that gives audit achievements and control responsibilities enough space without crowding the page.

How can I show control remediation clearly?

Describe the control gap, your part in the response, and the follow-through. Include an outcome or measure when you can support it with accurate details.

Should I include GRC platforms and AI tools on my resume?

Yes, when they are relevant to your work. Name platforms such as Vanta, Drata, or AuditBoard, and describe how you used tools such as Gemini, Claude, or Copilot with appropriate review.
ATS Score 91%

How we calculate this score

  • Keywords: 60% of the total. AI extracts keywords from your job description. If you do not provide one, a standard job description for the title matching your resume is used. This is not a match to a specific vacancy.
  • Text-based resume: 20%. The text resume assessed here receives 100 for this part.
  • Resume quality: 20%. We start at 100 and subtract points for issues found by our resume checks, down to a minimum of zero.
  • Keyword coverage = round(100 × confirmed matches ÷ total keywords). Exact matches and supported equivalents verified by AI receive full credit; unsupported keywords receive none. Live text checks use the saved equivalents and do not request a new AI review. Without keywords, no overall ATS score is available.
  • Final score = 60% of keyword coverage + 20% of the text score + 20% of the quality score, rounded to a whole number. Without keywords, no overall ATS score is available.

What this score means

Our scores are estimates, not employer ratings. They may contain errors and do not guarantee accurate parsing, a ranking, an interview, or a job. Check your document against the employer’s requirements. You are responsible for relying on this score.

Terms and Conditions

Score weights: Keywords 60% · Text based resume 20% · Resume quality 20%

Keyword coverage: 40 of 47 (85%) · Resume quality: 100%

Resume quality 100% · Weight 20% · Issues (0)

Details
  • ✓Name present: Juliet Alvarado
  • ✓Email format: juliet.alvarado@example.com
  • ✓Phone format: (510) 555-XXXX
  • ✓Experience 1: Job title: Senior GRC Analyst
  • ✓Experience 1: Company name: Copperline Cloud Services
  • ✓Experience 1: Work location: Oakland, CA
  • ✓Experience 1: Employment dates: Oct 2025 - Present
  • ✓Experience 1: Description or achievements: Present
  • ✓Experience 2: Job title: GRC Analyst II
  • ✓Experience 2: Company name: Harborlight Software
  • ✓Experience 2: Work location: San Jose, CA
  • ✓Experience 2: Employment dates: May 2023 - Sep 2025
  • ✓Experience 2: Description or achievements: Present
  • ✓Experience 3: Job title: IT Audit and Compliance Analyst
  • ✓Experience 3: Company name: Meridian Public Accounting
  • ✓Experience 3: Work location: San Francisco, CA
  • ✓Experience 3: Employment dates: Apr 2021 - Apr 2023
  • ✓Experience 3: Description or achievements: Present
  • ✓Experience 4: Job title: IT Audit Associate
  • ✓Experience 4: Company name: Crestview Assurance Group
  • ✓Experience 4: Work location: San Francisco, CA
  • ✓Experience 4: Employment dates: May 2020 - Mar 2021
  • ✓Experience 4: Description or achievements: Present
  • ✓No placeholder fields
  • ✓No repeated achievement bullets
  • ✓No empty bullets

No issues found by the current checks.

Text Based Resume 100% · Weight 20%

Parsed text
Juliet Alvarado
Senior GRC Analyst
(510) 555-XXXX
julietalvarado
juliet.alvarado@example.com
Oakland, CA 94612
STRENGTHS
Audit coordination
Kept audit evidence and requests organized across multiple teams, helping auditors and control owners resolve questions on schedule.
Control guidance
Translated control expectations into practical next steps, giving owners a clearer path from identified gaps to documented closure.
Cross-team alignment
Worked with Finance, IT, Security, and Engineering to coordinate shared compliance priorities and keep remediation moving.
Evidence quality
Improved evidence review through clear documentation and careful validation, helping teams prepare consistent audit materials.
Analyst mentoring
Coached a junior analyst on walkthrough preparation and evidence quality, building confidence in day-to-day audit coordination.
SUMMARY
Senior GRC Analyst with six years of experience in information security, IT audit, and compliance, including end-to-end audit ownership and SOX 404 control remediation. Apply SOC 2, ISO 27001, HIPAA, and NIST CSF requirements to IT controls, user access reviews, vendor assessments, and financial systems. Build audit-ready evidence and clear control documentation while coordinating with technical and nontechnical partners. Improve GRC workflows through platform configuration, continuous control monitoring, and careful use of AI tools, with CISA and ISO 27001 Lead Auditor credentials.
EXPERIENCE
Senior GRC Analyst
Copperline Cloud Services
Oct 2025 - Present
Oakland, CA
Leads SOX 404 and security compliance audit cycles across cloud infrastructure, finance, and engineering teams, maintaining audit calendars and coordinating evidence delivery for SOX, SOC 2, ISO 27001, HIPAA, and NIST CSF reviews.
Evaluates ITGC design and operating effectiveness for access management, change management, and computer operations; updates process narratives and risk-control matrices to clarify control intent, evidence, and ownership.
Identified gaps in privileged access and financial application change approvals, then developed remediation plans with control owners, due dates, and closure evidence for systems supporting financial reporting.
Coordinates recurring User Access Reviews (UARs) for GCP, ERP, billing, and revenue recognition platforms, documenting reviewer decisions and escalating unresolved access exceptions.
Improves Vanta asset management, integrations, test configurations, control mapping, review workflows, and risk objects; developed continuous control monitoring routines that reduce manual evidence follow-up.
Applies Gemini, Claude, and Copilot to draft questionnaire responses, summarize audit evidence, and prepare policy updates, with human review for accuracy and sensitive information. Uses NIST AI Risk Management Framework concepts to assess emerging AI governance risks.
Responds to customer security questionnaires and due diligence within established SLAs, maintains trust center content and the Security Diligence Playbook, and presents control health metrics to GRC leadership.
Conducts third-party security assessments and reviews vendor contracts for security requirements; mentors a junior analyst and leads cross-functional compliance initiatives with IT, Security, Finance, and Engineering.
GRC Analyst II
Harborlight Software
May 2023 - Sep 2025
San Jose, CA
Managed evidence and walkthrough preparation for annual SOC 2 and ISO 27001 audits, coordinating internal control owners and external auditors to resolve documentation questions before fieldwork deadlines.
Supported SOX readiness as the company expanded its financial reporting controls, testing ITGCs and documenting access, change management, and computer operations processes in AuditBoard.
Assessed access and control gaps in cloud and financial applications, partnering with engineering and finance owners to set remediation steps and retain closure evidence.
Ran scheduled UARs and internal audits across business applications, including ERP and billing systems, and tracked exceptions through resolution.
Completed vendor risk assessments and reviewed security terms in vendor contracts; refreshed policies and standards and maintained security awareness training through KnowBe4.
Prepared customer questionnaire responses and trust center updates, using Drata to organize control evidence and maintain consistent diligence materials.
Piloted Copilot for routine evidence summaries in 2024, establishing review checks to prevent inaccurate or unsupported compliance statements.
IT Audit and Compliance Analyst
Meridian Public Accounting
Apr 2021 - Apr 2023
San Francisco, CA
Executed IT audit testing for technology and financial-services clients, examining access management, change controls, and computer operations against SOX 404 and SOC 2 requirements.
Organized audit evidence and documented control walkthroughs, process narratives, and risk-control matrices, helping client teams resolve incomplete or inconsistent records.
Assessed control gaps in ERP, billing, and revenue recognition systems, translating findings into practical remediation actions for finance and IT control owners.
Performed internal audit procedures and vendor risk reviews, documenting security findings and tracking management responses through agreed milestones.
Communicated testing results in concise reports and walkthroughs, tailoring explanations for technical staff, finance stakeholders, and external auditors.
IT Audit Associate
Crestview Assurance Group
May 2020 - Mar 2021
San Francisco, CA
Supported public accounting IT audit engagements by sampling access and change-management evidence and checking documentation against established control procedures.
Prepared workpapers and evidence indexes for senior auditors, improving traceability between system records, control narratives, and testing conclusions.
Interviewed application administrators during supervised walkthroughs and documented computer operations and user provisioning practices for review.
Helped clients organize audit requests and follow up on missing evidence, building a foundation in detail-oriented audit execution and stakeholder communication.
SKILLS
SOC 2 Audits
Control Monitoring
SOX 404 Controls
Internal Auditing
Access Reviews
Customer Due Diligence
Vendor Assessments
Policy Management
Audit Coordination
Risk Remediation
ISO 27001 Compliance
Audit Evidence
GRC Platforms
AI Governance
ITGC Testing
LANGUAGES
English
Native
Spanish
Intermediate
MY CAREER
6.5Years
Senior GRC Analyst at Copperline Cloud Services (1.1 Years)
GRC Analyst II at Harborlight Software (2.4 Years)
IT Audit and Compliance Analyst at Meridian Public Accounting (2.1 Years)
IT Audit Associate at Crestview Assurance Group (11 Months)
LEADERSHIP, AWARDS & RECOGNITION
Recognized by the GRC leadership team in 2026 for clear audit coordination and practical guidance to control owners.
Mentors a junior analyst on evidence quality, audit walkthrough preparation, and stakeholder communication.
Led a cross-functional working group that standardized control remediation tracking across Finance, IT, and Engineering.
EDUCATION
Bachelor of Science in Accounting
San Francisco State University
2014
San Francisco, CA
CERTIFICATIONS
Certified Information Systems Auditor (CISA)
2025
ISO/IEC 27001 Lead Auditor
2024
CompTIA Security+
2021
PROFESSIONAL SKILLS
GRC Platforms: Vanta, Drata, AuditBoard
Cloud Platforms: Google Cloud Platform, AWS, Microsoft Azure
AI Assistants: Gemini, Claude, Microsoft Copilot
Security Training: KnowBe4, Microsoft Security Awareness Training, Google Security Awareness Training
Business Systems: SAP ERP, Oracle ERP, NetSuite
Data and Reporting: Microsoft Excel, Google Sheets, Microsoft Power BI
PROFESSIONAL AFFILIATIONS
Member, ISACA, engaging with the information systems audit and governance community.
Member, Cloud Security Alliance, participating in a professional community focused on cloud security practice.

Matched keywords (40)

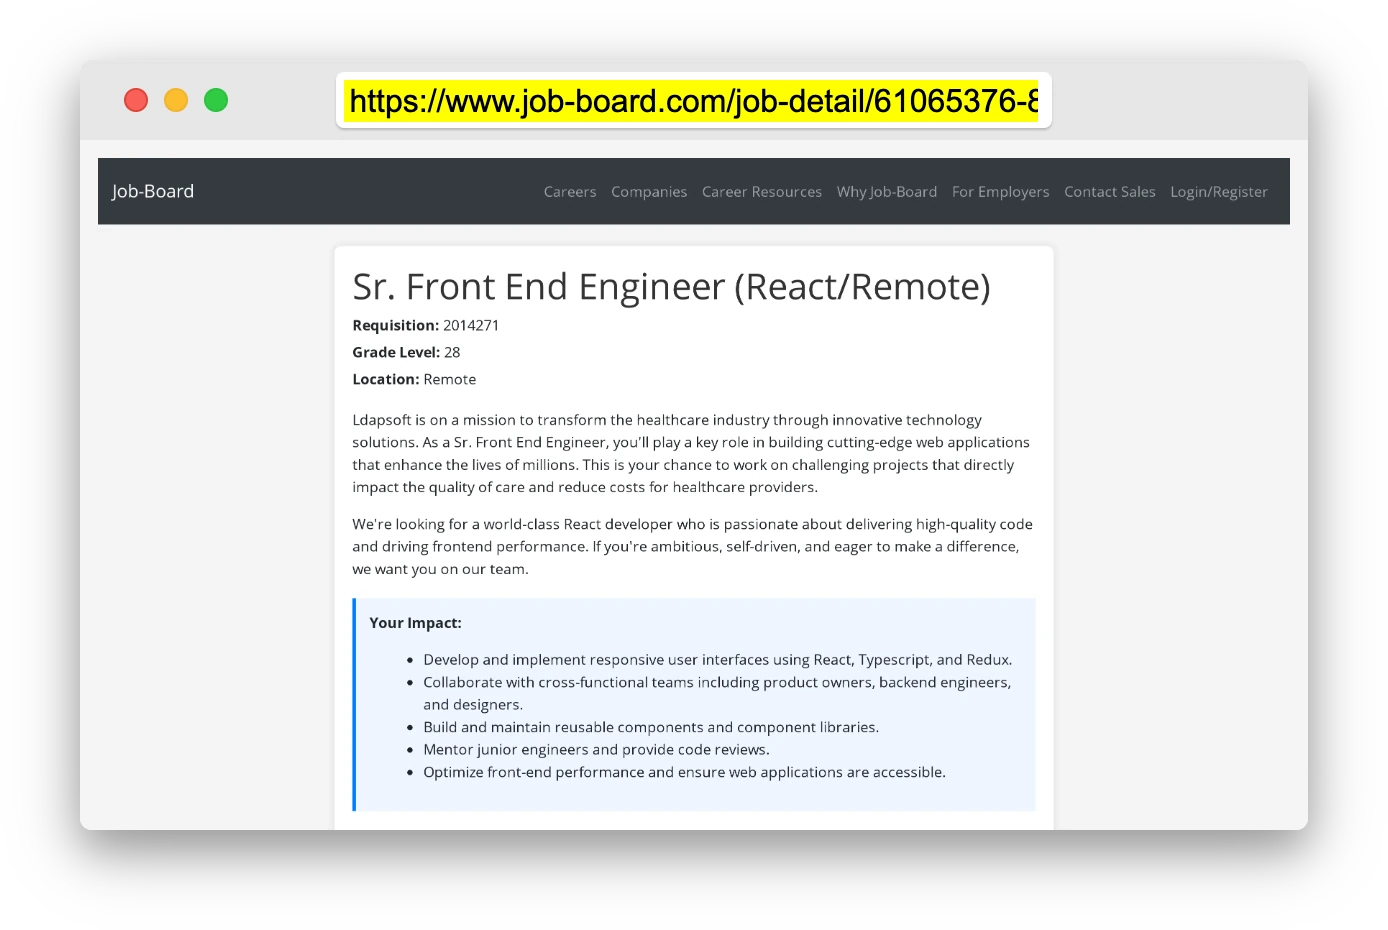
  • six years of experience in information security, IT audit, and complianceOriginal keyword in JD: 5–7 years of GRC, information security, IT audit, or related compliance experience
  • end-to-end audit ownershipOriginal keyword in JD: End-to-end audit cycle ownership
  • SOX 404
  • Evaluates ITGC design and operating effectivenessOriginal keyword in JD: IT general controls (ITGCs)
  • SOC 2
  • ISO 27001
  • HIPAA
  • NIST CSFOriginal keyword in JD: NIST Cybersecurity Framework (NIST CSF)
  • Evaluates ITGC design and operating effectiveness for access management, change management, and computer operationsOriginal keyword in JD: ITGC design and operating effectiveness testing
  • Identified gaps in privileged access and financial application change approvals, then developed remediation plans with control owners, due dates, and closure evidence for systems supporting financial reporting.Original keyword in JD: Control gap identification and remediation
  • user access reviewsOriginal keyword in JD: User Access Reviews (UARs)
  • vendor risk assessments
  • internal audits
  • AuditBoardOriginal keyword in JD: GRC platform experience (Vanta OR Drata OR AuditBoard)
  • Managed evidenceOriginal keyword in JD: Audit evidence management
  • process narratives and risk-control matrices
  • access management
  • change managementOriginal keyword in JD: Change management controls
  • computer operationsOriginal keyword in JD: Computer operations controls
  • walkthrough preparation for annual SOC 2 and ISO 27001 auditsOriginal keyword in JD: Audit walkthroughs
  • customer security questionnaires
  • Responds to customer security questionnaires and due diligence within established SLAsOriginal keyword in JD: Security due diligence
  • trust center content
  • third-party security assessments
  • reviews vendor contracts for security requirementsOriginal keyword in JD: Vendor contract security reviews
  • Improves Vanta asset management, integrations, test configurations, control mapping, review workflows, and risk objectsOriginal keyword in JD: GRC platform configuration and optimization
  • continuous control monitoring
  • presents control health metrics to GRC leadershipOriginal keyword in JD: Control health metrics and reporting
  • ClaudeOriginal keyword in JD: AI and large language model tools (Gemini OR Claude OR Copilot)
  • CISAOriginal keyword in JD: CISA OR CRISC OR CISSP OR Security+ OR ISO 27001 Lead Auditor
  • Public Accounting
  • AWSOriginal keyword in JD: Cloud platforms (GCP OR AWS OR Azure)
  • ERP, billing, and revenue recognition systems
  • Policy Management
  • security awareness training
  • Uses NIST AI Risk Management Framework concepts to assess emerging AI governance risks.Original keyword in JD: AI risk assessment frameworks
  • AI Governance
  • Communicated testing results in concise reports and walkthroughsOriginal keyword in JD: Written and verbal communication
  • leads cross-functional compliance initiatives with IT, Security, Finance, and EngineeringOriginal keyword in JD: Cross-functional compliance leadership
  • mentors a junior analystOriginal keyword in JD: Mentoring junior analysts

Missing keywords (7)

  • Internal and external auditor coordination
  • Security policies and standards
  • GRC automation
  • Explaining compliance requirements to technical and nontechnical audiences
  • Influencing control owners without direct authority
  • Independent prioritization across stakeholders
  • Attention to detail and reliable follow-through
Disclaimer: All names, images, contact information, employment histories, achievements, security clearances, military credentials, and other qualifications shown in this content are fictional and used for illustrative purposes only. Any resemblance to actual persons, living or deceased, is purely coincidental.

Resume and cover-letter examples and recommendations in this article reflect general best practices and professional experience and are provided for guidance only. Results may vary based on role, industry, region, and hiring organization.

Content Accuracy and Verification: To the fullest extent permitted by applicable law, we do not represent or warrant that resume or cover-letter guidance, examples, recommendations, or related information are accurate, complete, current, error-free, or suitable for any particular purpose. You are responsible for independently reviewing and verifying the information before relying on it.

ATS and Cover-Letter Scores: ATS scores are estimates calculated using our own formula, informed by publicly available guidance on resume formatting and keyword matching. They are not scores issued or endorsed by an ATS provider or employer. Cover-letter scores are also our own assessments. Parsing, weighting, screening criteria, and results vary between systems, employers, job descriptions, and document formats. No score guarantees successful parsing, a particular ranking, an interview, or employment. Use scores as general guidance and independently check your documents against the employer’s requirements. To the fullest extent permitted by applicable law, we accept no liability for errors in scores or parsing, or losses arising from reliance on these assessments. Nothing in this notice excludes liability or limits consumer rights that cannot lawfully be excluded or limited.

Terms and Conditions
 
> JP 1 1
PDF Footer and Margins Setup
The margins are applied to the document, and the footer shows up in the preview and the PDF

Footer Font Settings

Are you applying for a specific job
so we can tailor your resume to it?
Are you applying for a specific job
so we can tailor your cover letter to it?

Your data stays private and is never used for training.Privacy Policy

Type your details as text to generate a personalized resume Type your details as text to generate a personalized cover letter
Website link found! Ready to create resume from:

Your data stays private and is never used for training.Privacy Policy

Drag the into the box to verify you're human.
Drop here

My Resumes

Displaying {number_of_files} files (out of {total_of_all_files} total)
Name File Type Last Modified: Description:

Rename File

Filename already exists!

Delete Files

Warning: This action is irreversible. Once you click submit, the files will be permanently deleted.

Heading text
Upload From Computer Upload
Select From Existing
LinkedIn
Drag & Drop files anywhere in this tab, or

Uploaded Files

Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

My Files

Resumes or cover letters you create will appear here. No files available yet.
Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Add LinkedIn Profile PDF

You can download your LinkedIn profile as a PDF by opening linkedin.com in a web browser, clicking your profile photo, selecting the “More” or “Resources” button, and choosing “Save to PDF.” You can then attach the PDF using the Upload From Computer tab.

Paste Your LinkedIn Profile Text

If you have copied the LinkedIn profile text, paste it below. See how to copy your profile from LinkedIn

Select this to use the LinkedIn profile text for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Try these controls

<
>