US English


7 VP, Security - SaaS and AI Security Resume Templates with Example
By Ria · Last Updated On October 23, 2026
Resume example — page 1

This guide shows you how to create a VP, Security - SaaS and AI Security resume that presents executive scope, security judgment, and business impact with clarity. You will learn how to organize your evidence so leaders and recruiters can quickly understand your value for this role.

Build a focused summary, then support it with concise experience bullets and relevant skills. Strong examples can show security strategy, AI governance, incident leadership, Board communication, and assurance work, with tools and standards such as AWS, Kubernetes, SOC 2, ISO 27001, ISO 42001, and Okta where they match your background.

The document is presented in 7 layouts. Compare the image previews to see how each design organizes executive experience, skills, and credentials, then open an example in the editor to review or customize its structure.

What Makes a Great VP, Security - SaaS and AI Security Resume in 2026

A strong resume makes the scope of security leadership easy to see. Use a clear summary and focused experience bullets to show strategy, team leadership, risk decisions, incident response, and executive communication.

Support claims with specific evidence, such as leading SOC 1 and SOC 2 assurance, ISO programs, AI governance, or a serious incident response. Include role-relevant terms like AWS, Kubernetes, Okta, ISO 42001, and EU AI Act only when they reflect your experience.

Note: Resume examples are for educational purposes only. Use only information that accurately reflects your experience and qualifications. References to real organizations do not imply affiliation or endorsement.

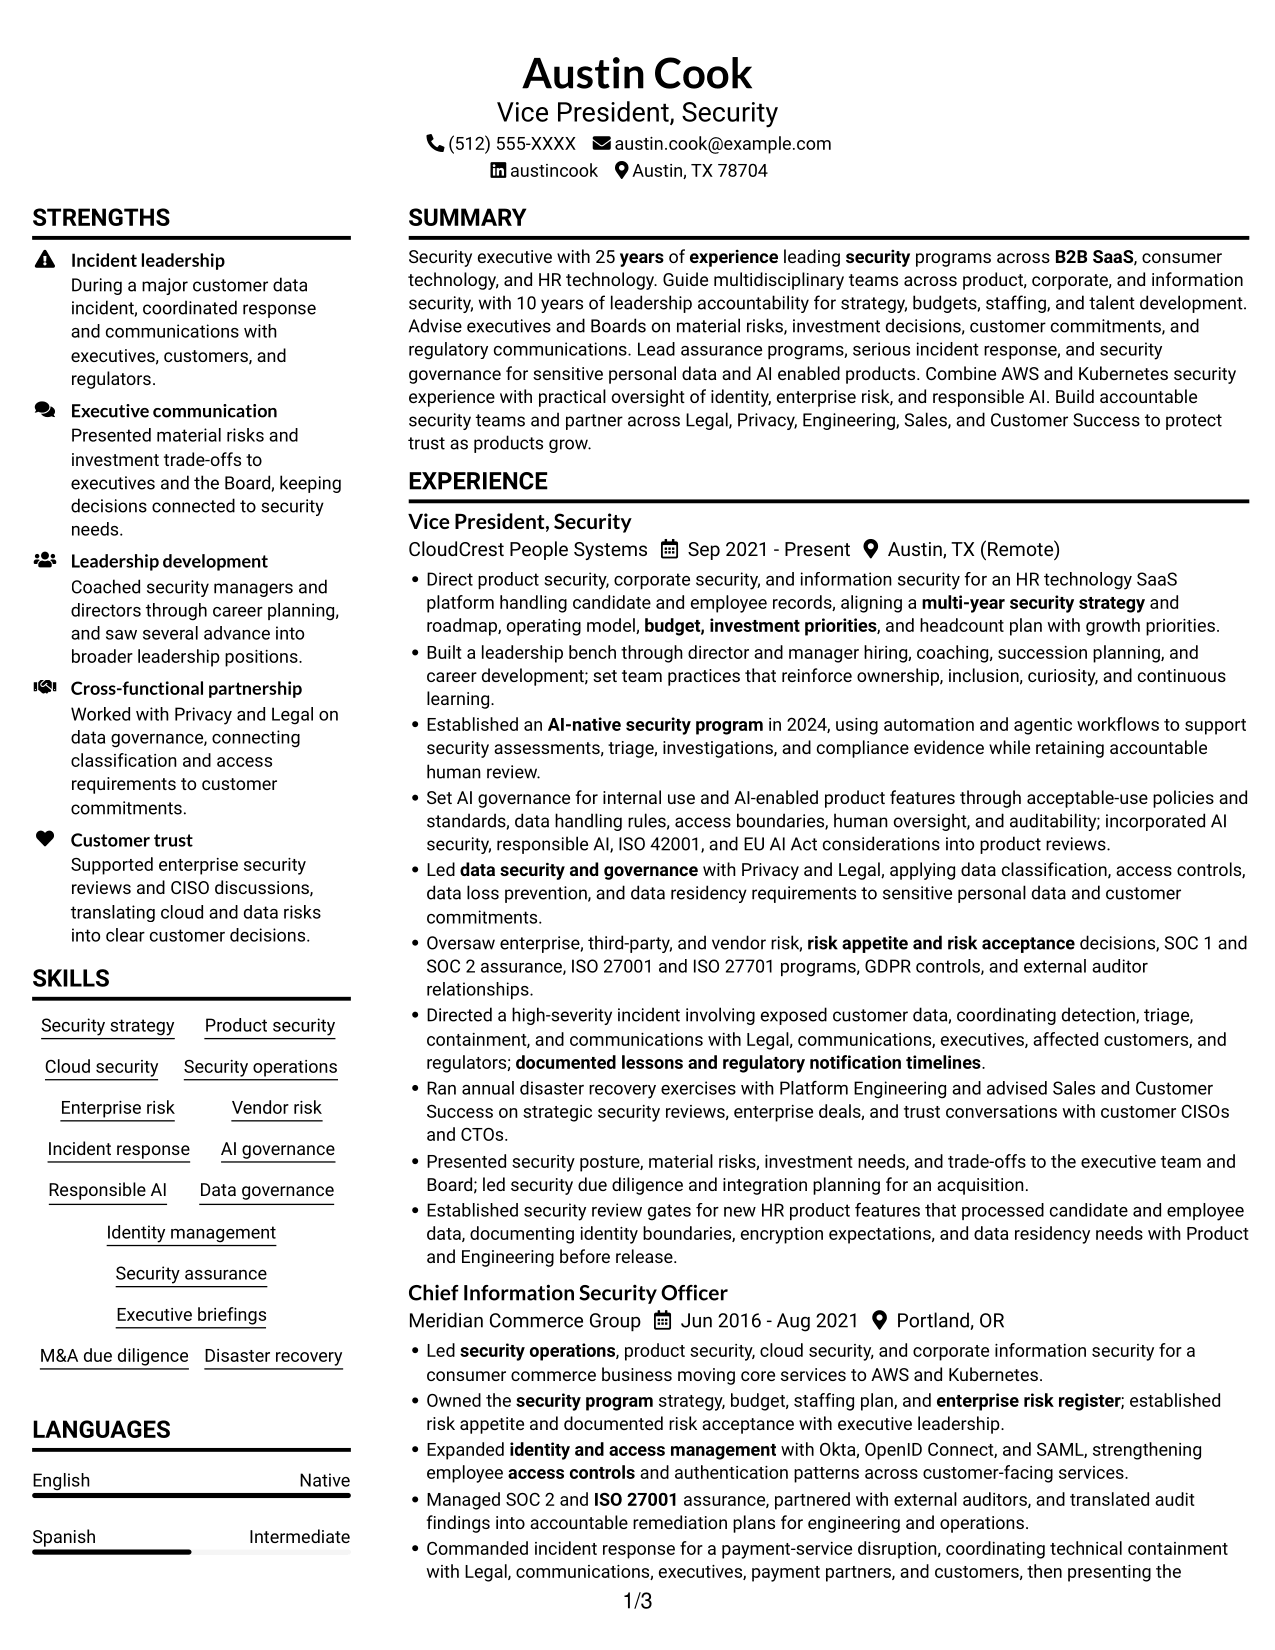
#1 Plain Two Column Format Resume Example

Plain Two Column Format places resume information in two body columns, helping reviewers compare career history with supporting details.
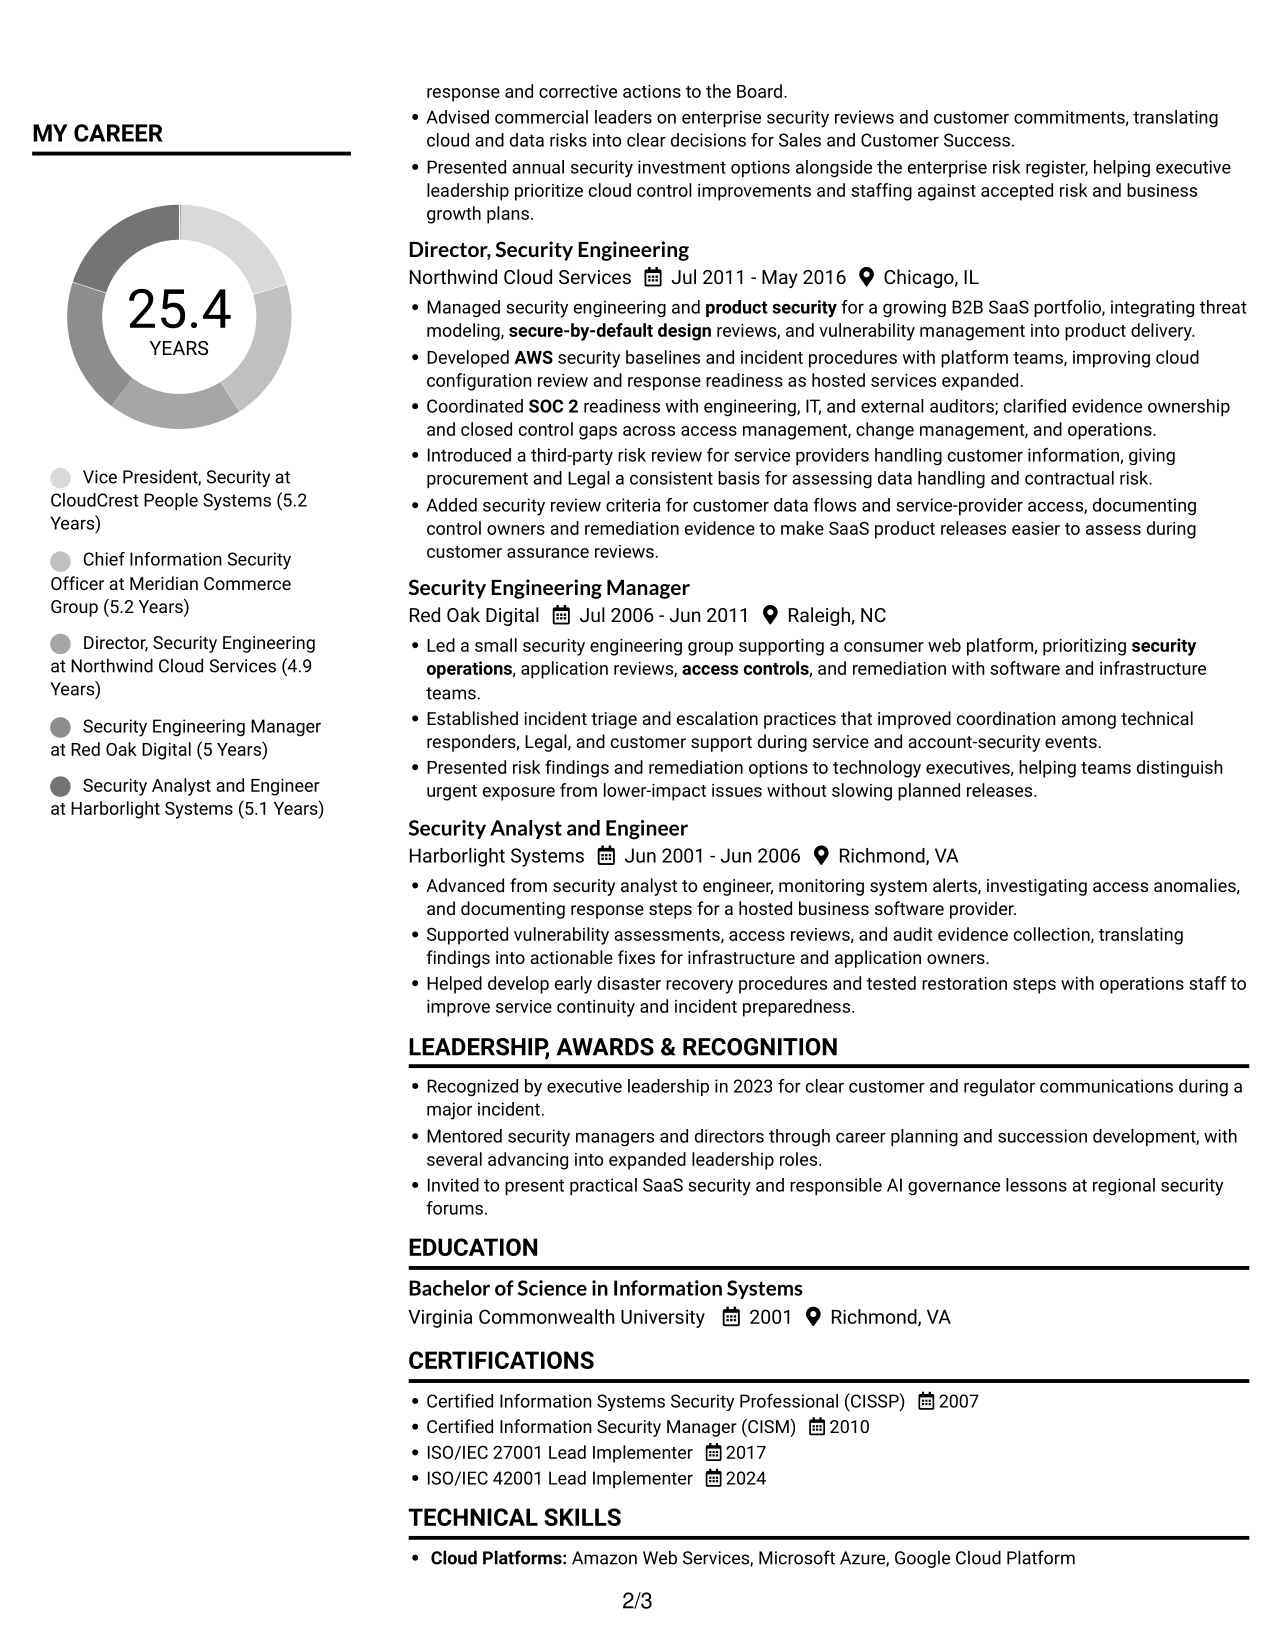
 
Resume example — page 1   Resume example — page 2

Resume Snapshot

  • 25 years of security program experience
  • 10 years of security leadership
  • AI governance for internal and product use
  • Executive and Board risk briefings

Why This Format Works

  • The two-column body separates career history from supporting skills and education.
  • Parallel content areas keep leadership scope and technical breadth visible without disrupting chronology.
  • Clear section groups help reviewers locate executive achievements, credentials, and measurable results.

Best For

  • Executive resumes with broad scope
  • Career timelines spanning multiple roles
  • Skills and credentials beside experience
  • Detailed accomplishment records
  • Quick section-to-section review

Resume Keywords

  • 25 years of experience leading security programs
  • 10 years of leadership accountability for strategy, budgets, staffing, and talent development
  • Owned the security program strategy, budget, staffing plan, and enterprise risk register
  • aligning a multi-year security strategy and roadmap
  • operating model
  • budget, investment priorities
  • headcount plan
  • director and manager hiring, coaching, succession planning
  • enterprise risk register
  • Oversaw enterprise, third-party, and vendor risk
  • risk appetite and risk acceptance
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 27701
See all keywords
 

#2 Simple One Column Format Resume Example

Simple One Column Format uses a single body column, giving the resume a clear top-to-bottom reading path.
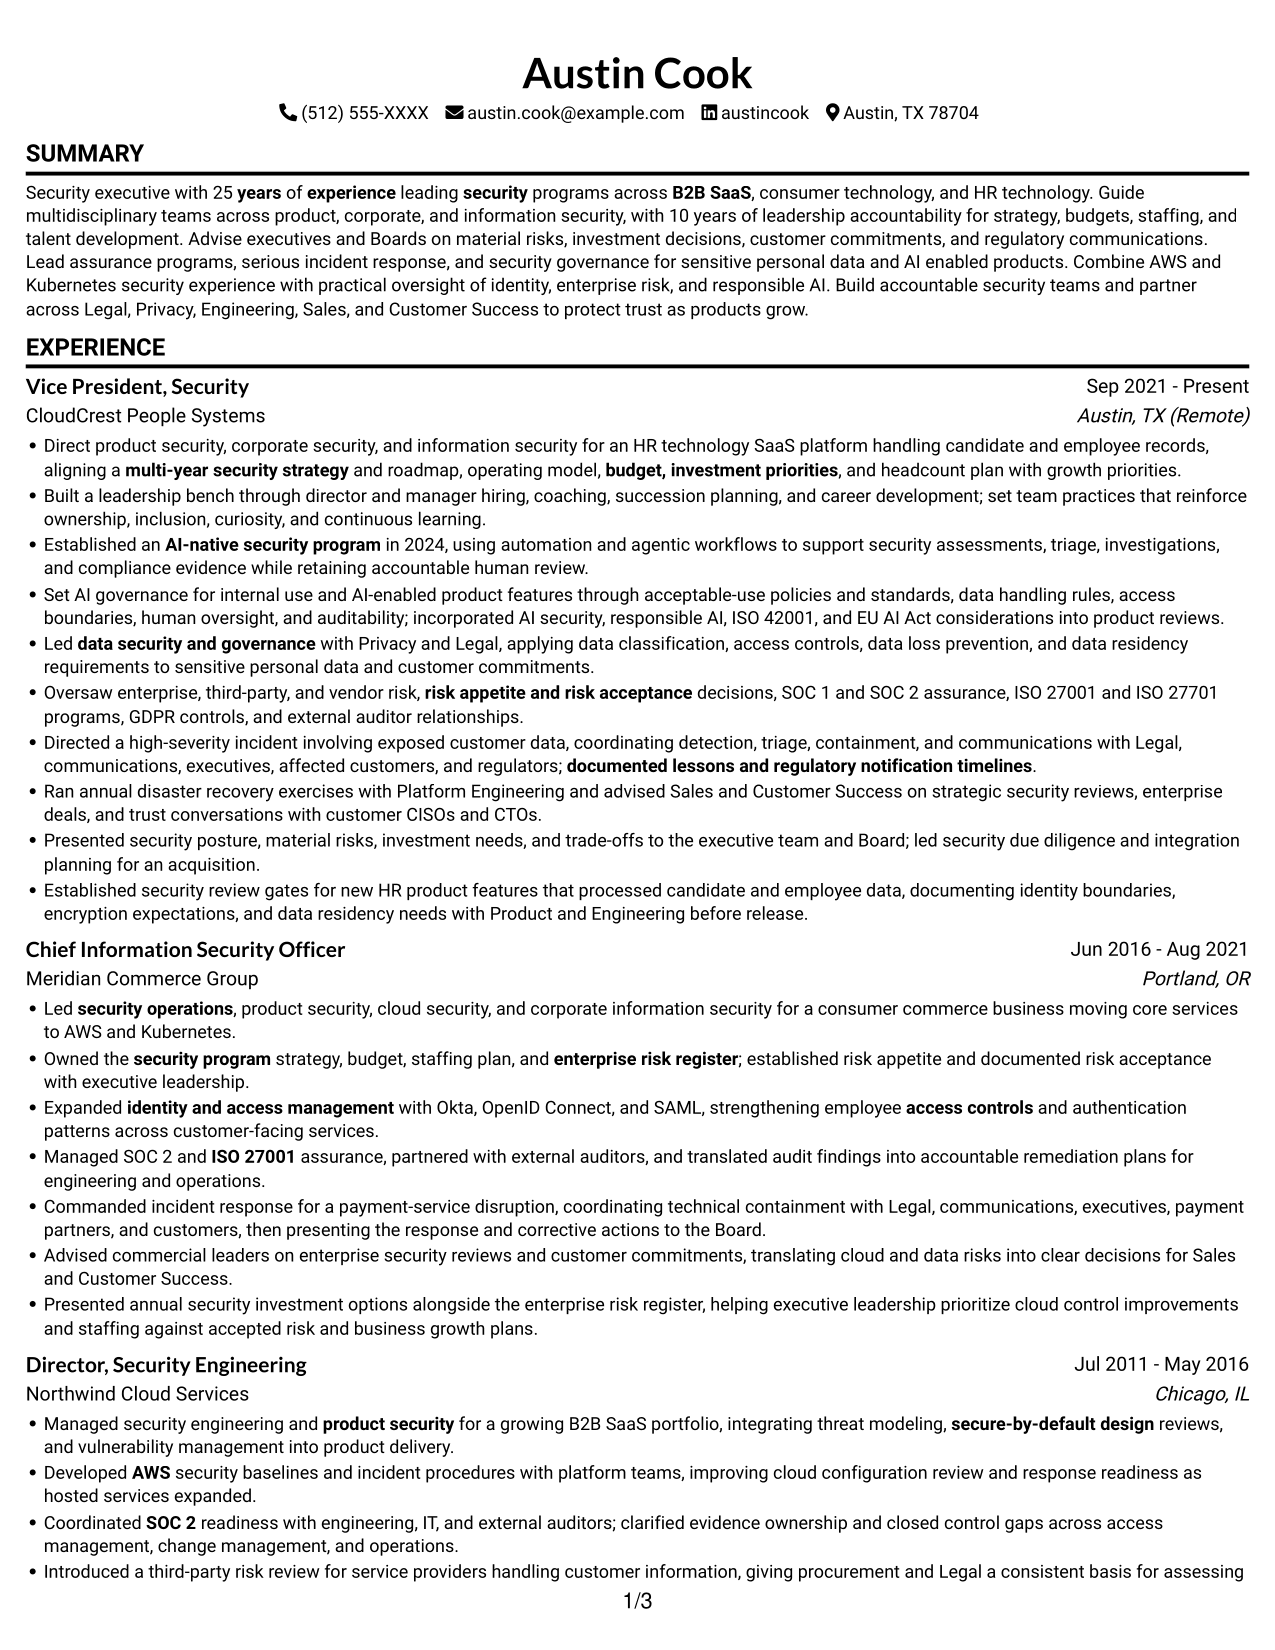
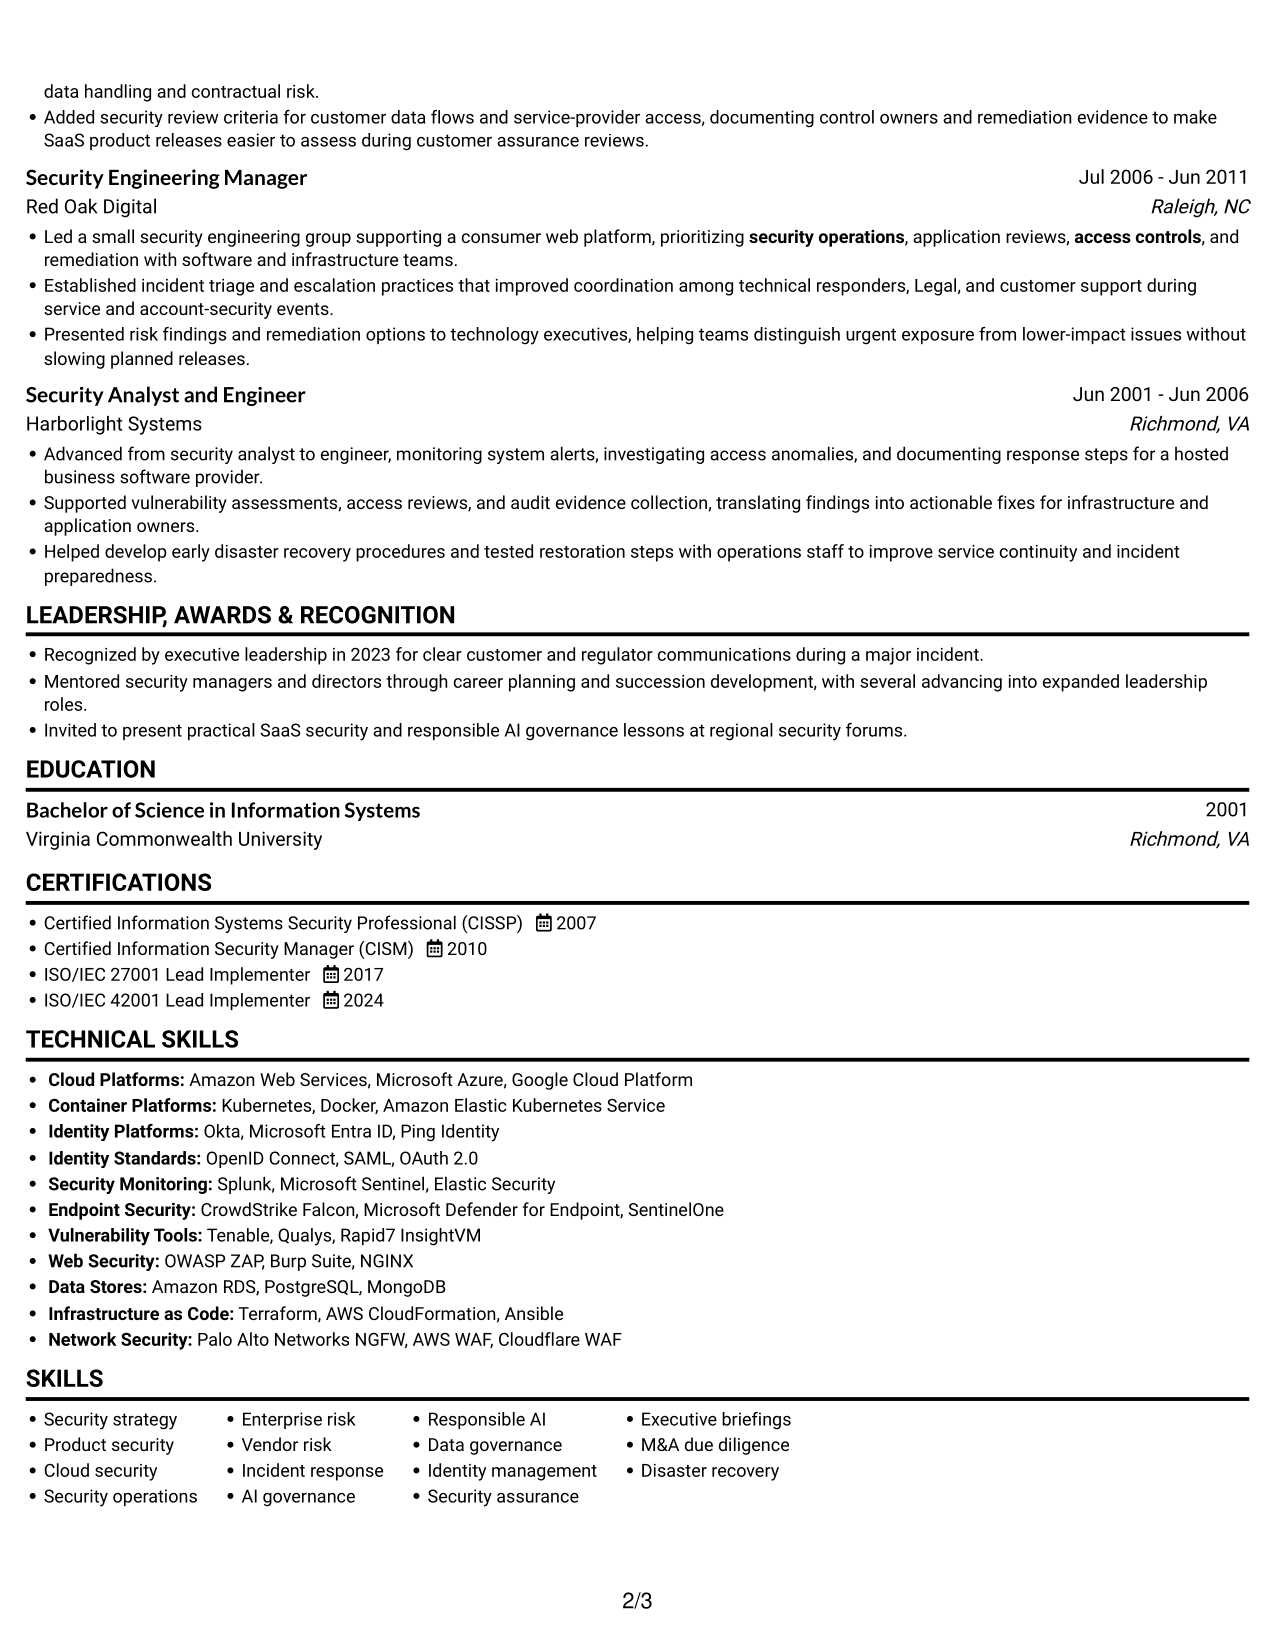
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • One continuous column keeps the extensive career chronology in a familiar reading order.
  • Full-width sections give detailed leadership evidence and achievement bullets room to read clearly.
  • Top-to-bottom movement helps reviewers follow skills, education, and credentials in sequence.

Best For

  • Long executive career histories
  • Linear recruiter review
  • Detailed experience narratives
  • ATS-oriented resume structure
  • Section-by-section credential review
 

#3 Clean Two Column Sidebar Format Resume Example

Clean Two Column Sidebar Format arranges resume content in two body columns, making separate sections easier to locate.
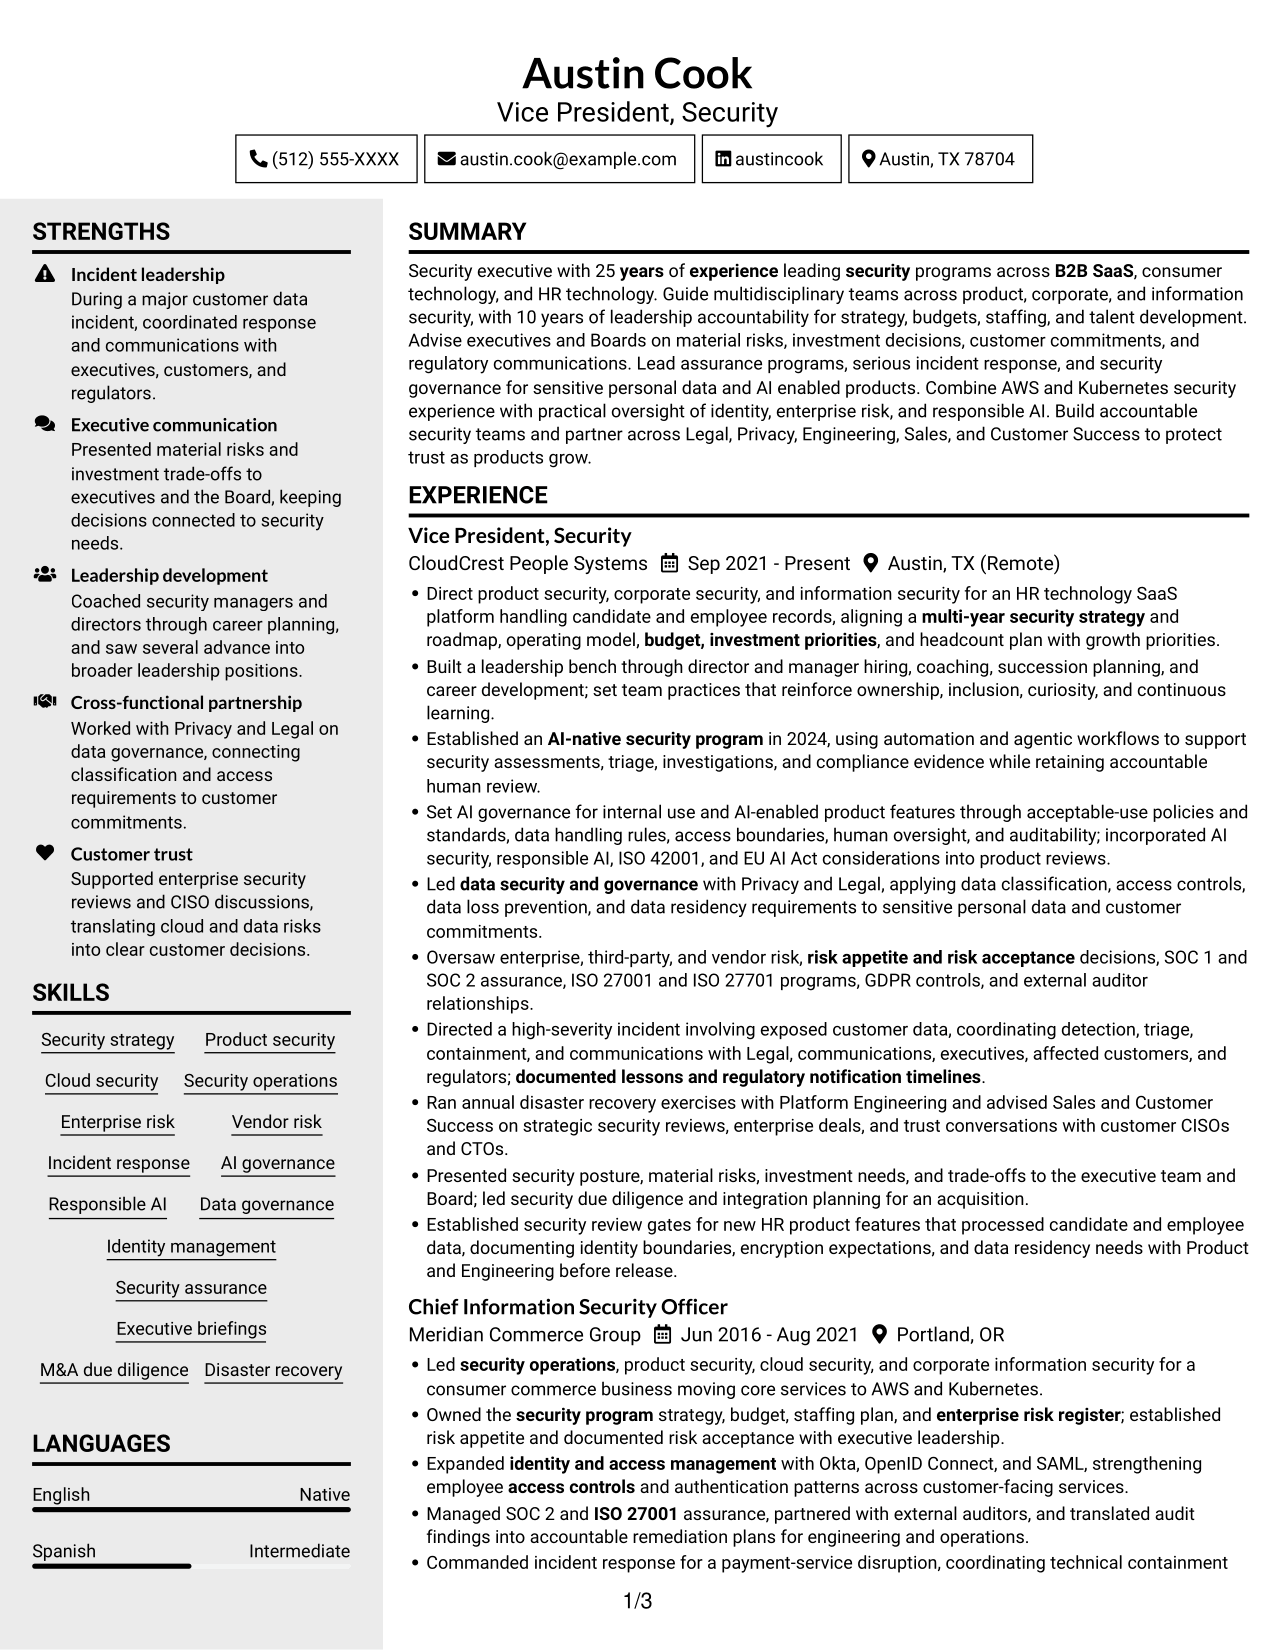
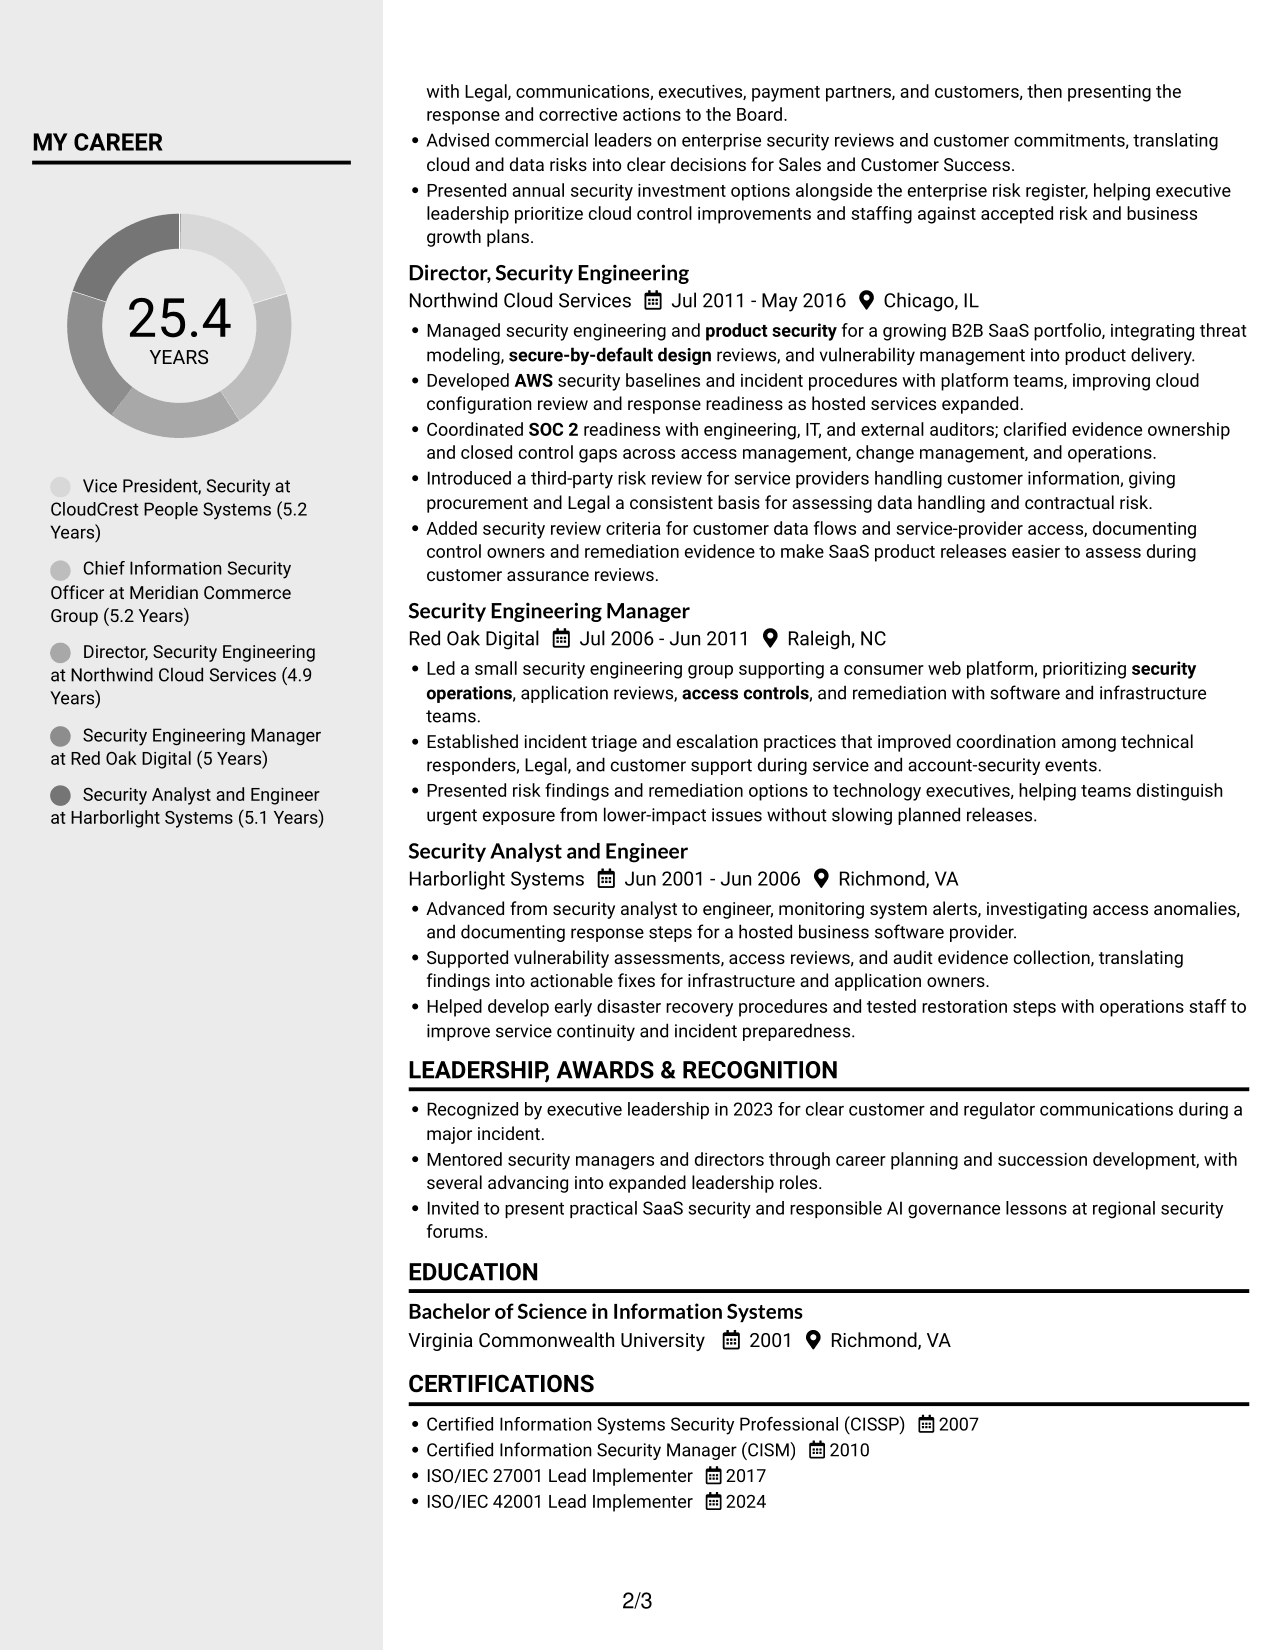
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Distinct content areas make career history and supporting details easier to scan.
  • Skills and credentials can remain visible beside the chronological work record.
  • Section separation helps reviewers move between leadership scope and education.

Best For

  • Resumes with many supporting sections
  • Side-by-side content review
  • Executive experience across varied domains
  • Dense skills and credential details
  • Quick education lookup
 

#4 Two Column Format Resume Example

Two Column Format places resume sections in paired body columns, helping reviewers compare career progression with related details.
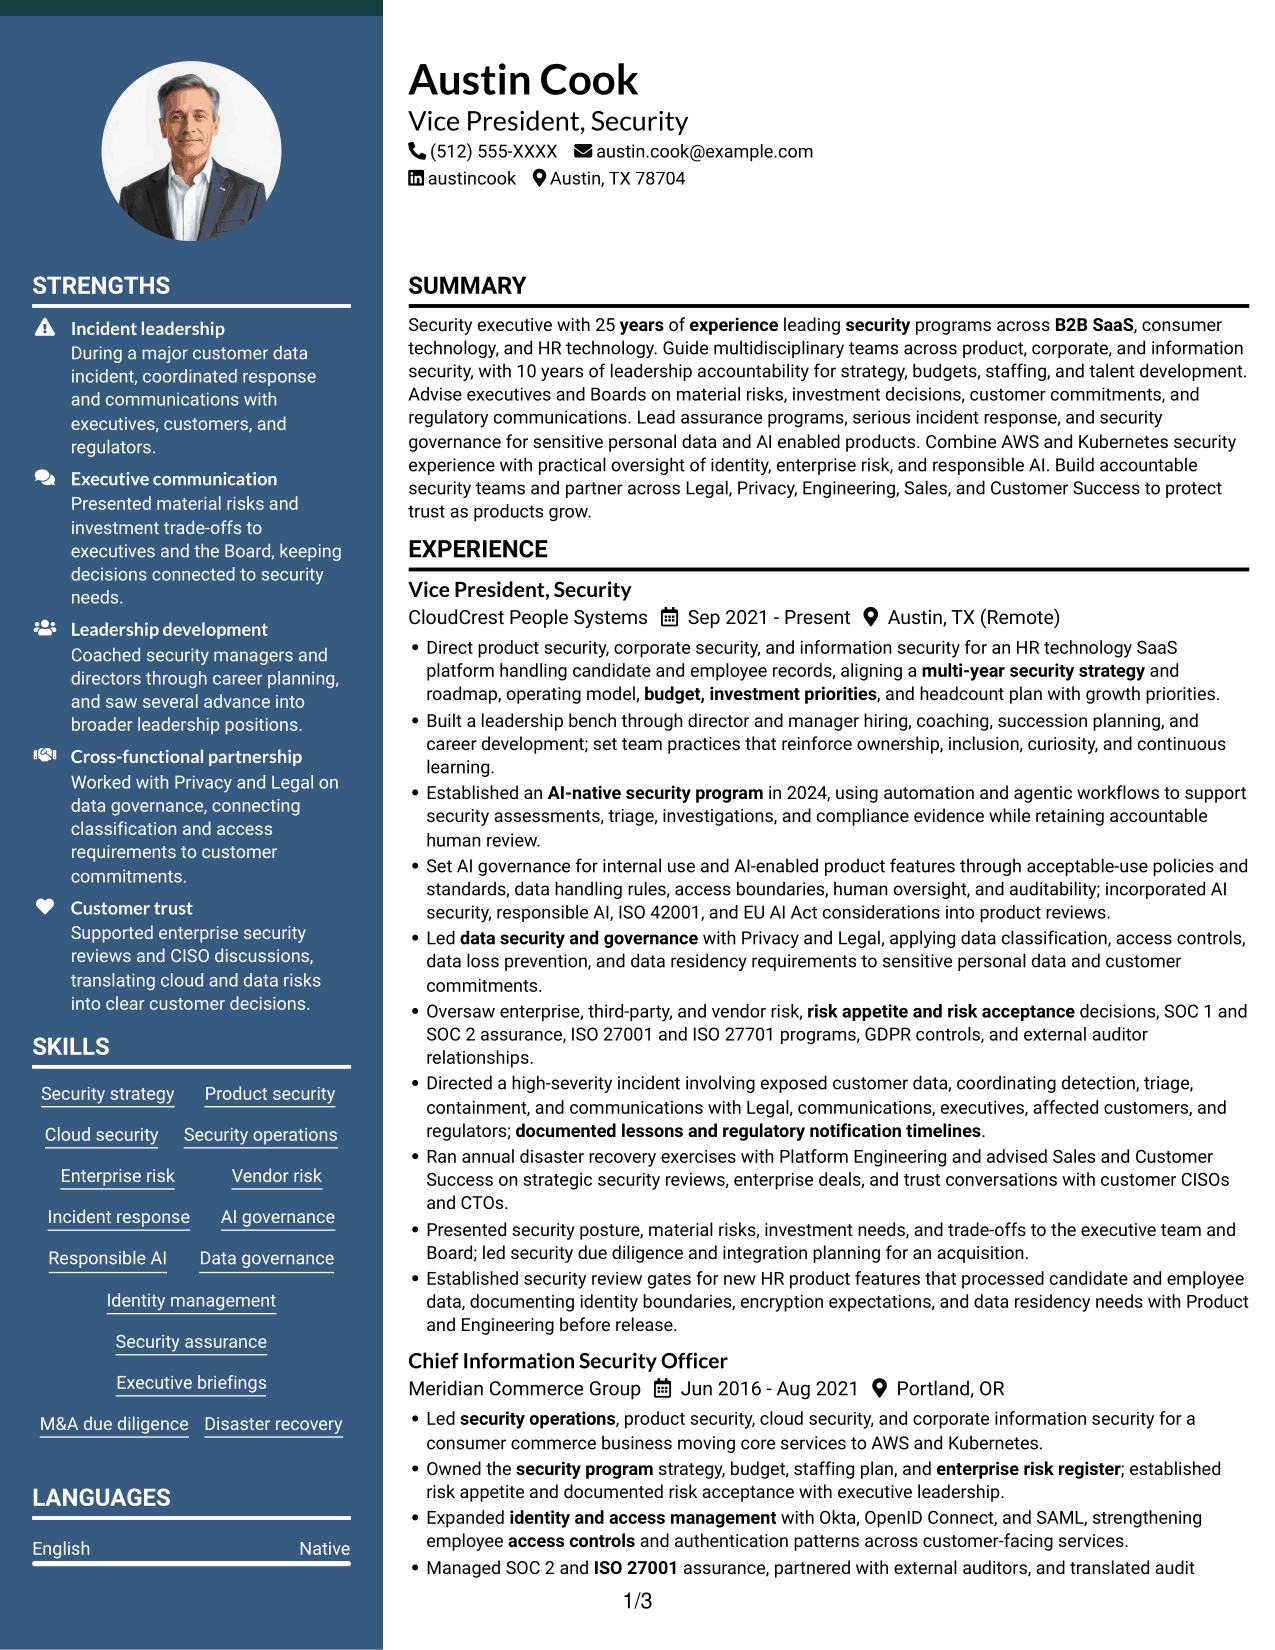
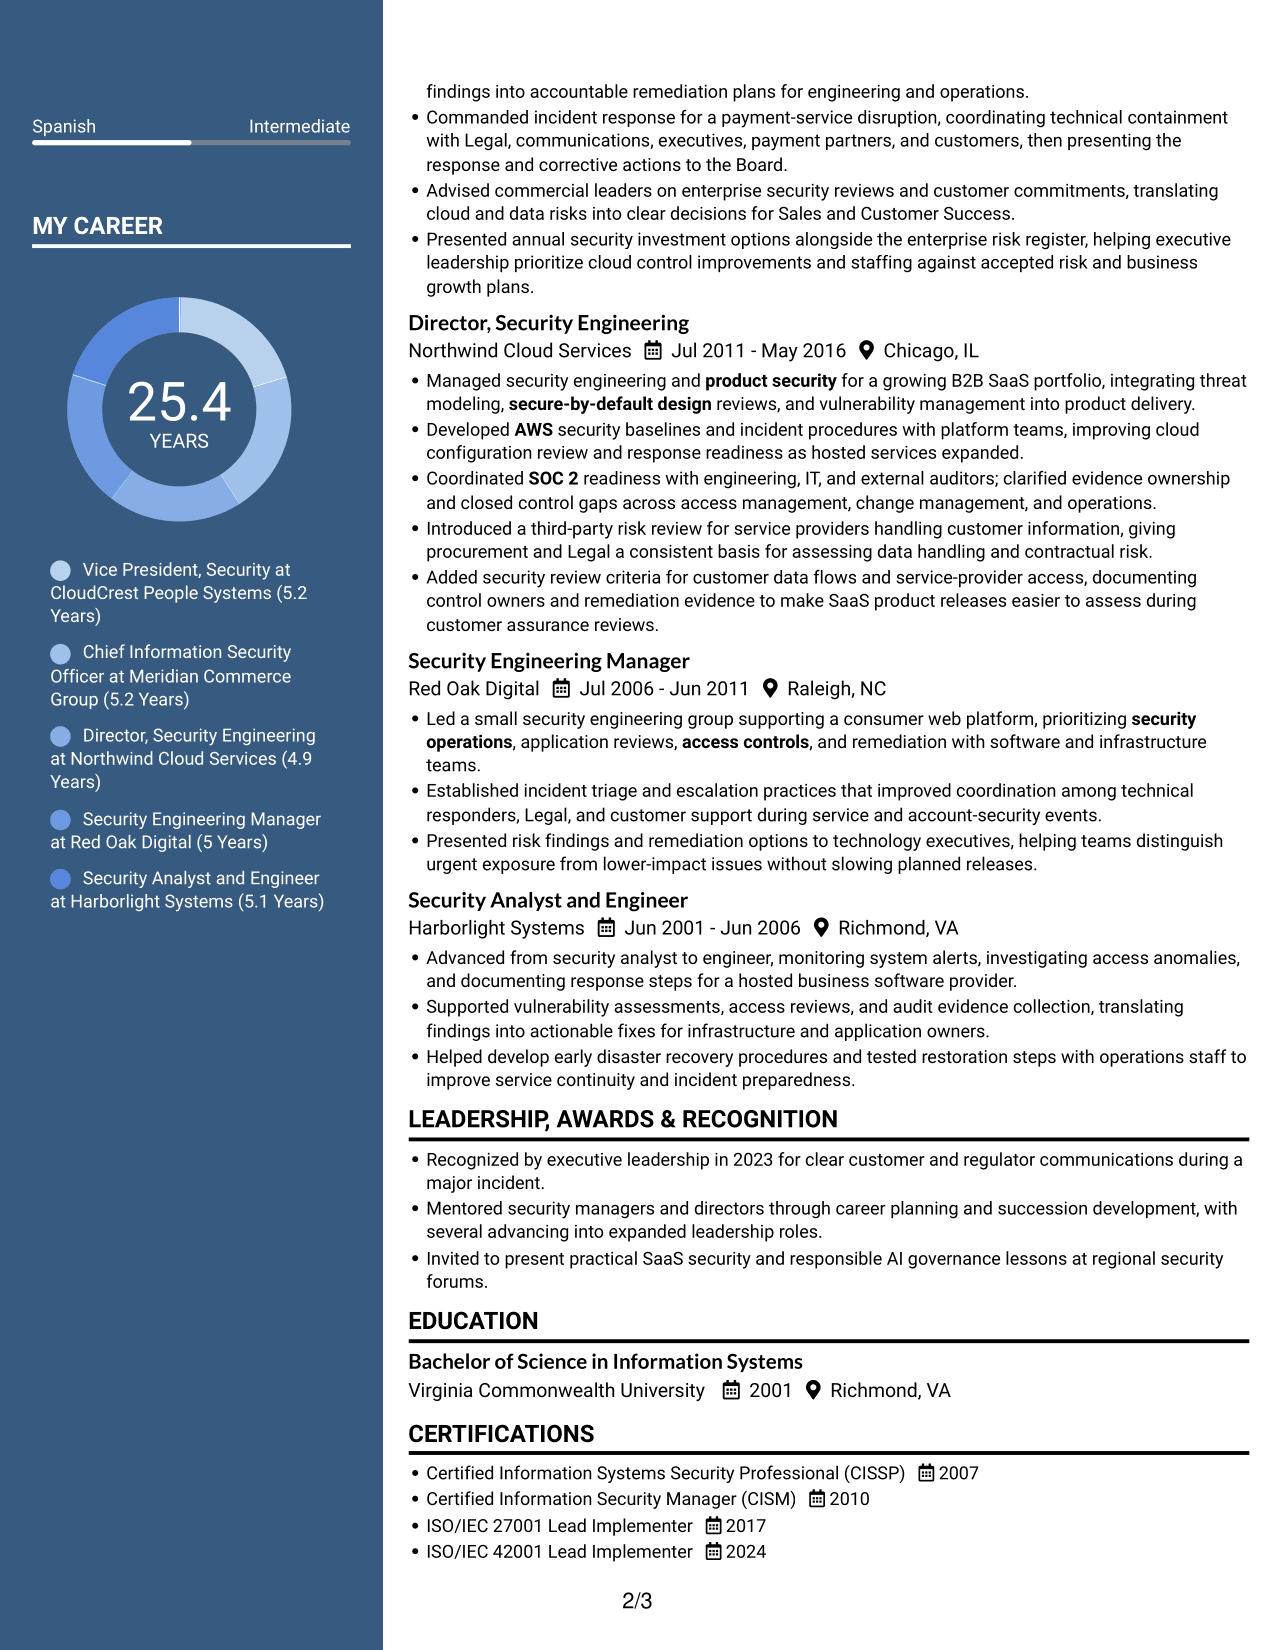
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two body columns let reviewers compare career progression with supporting resume sections.
  • Grouping related details across columns keeps skills and credentials easy to locate.
  • Chronological experience remains distinct from education and leadership recognition.

Best For

  • Multi-area executive resumes
  • Parallel section comparison
  • Career progression and breadth
  • Complete education and certification records
  • Recruiter scans across resume sections


#5 Photo Header Two Column Format Resume Example

Photo Header Two Column Format places a photo in the header above a two-column body, pairing a visual identifier with organized resume sections.
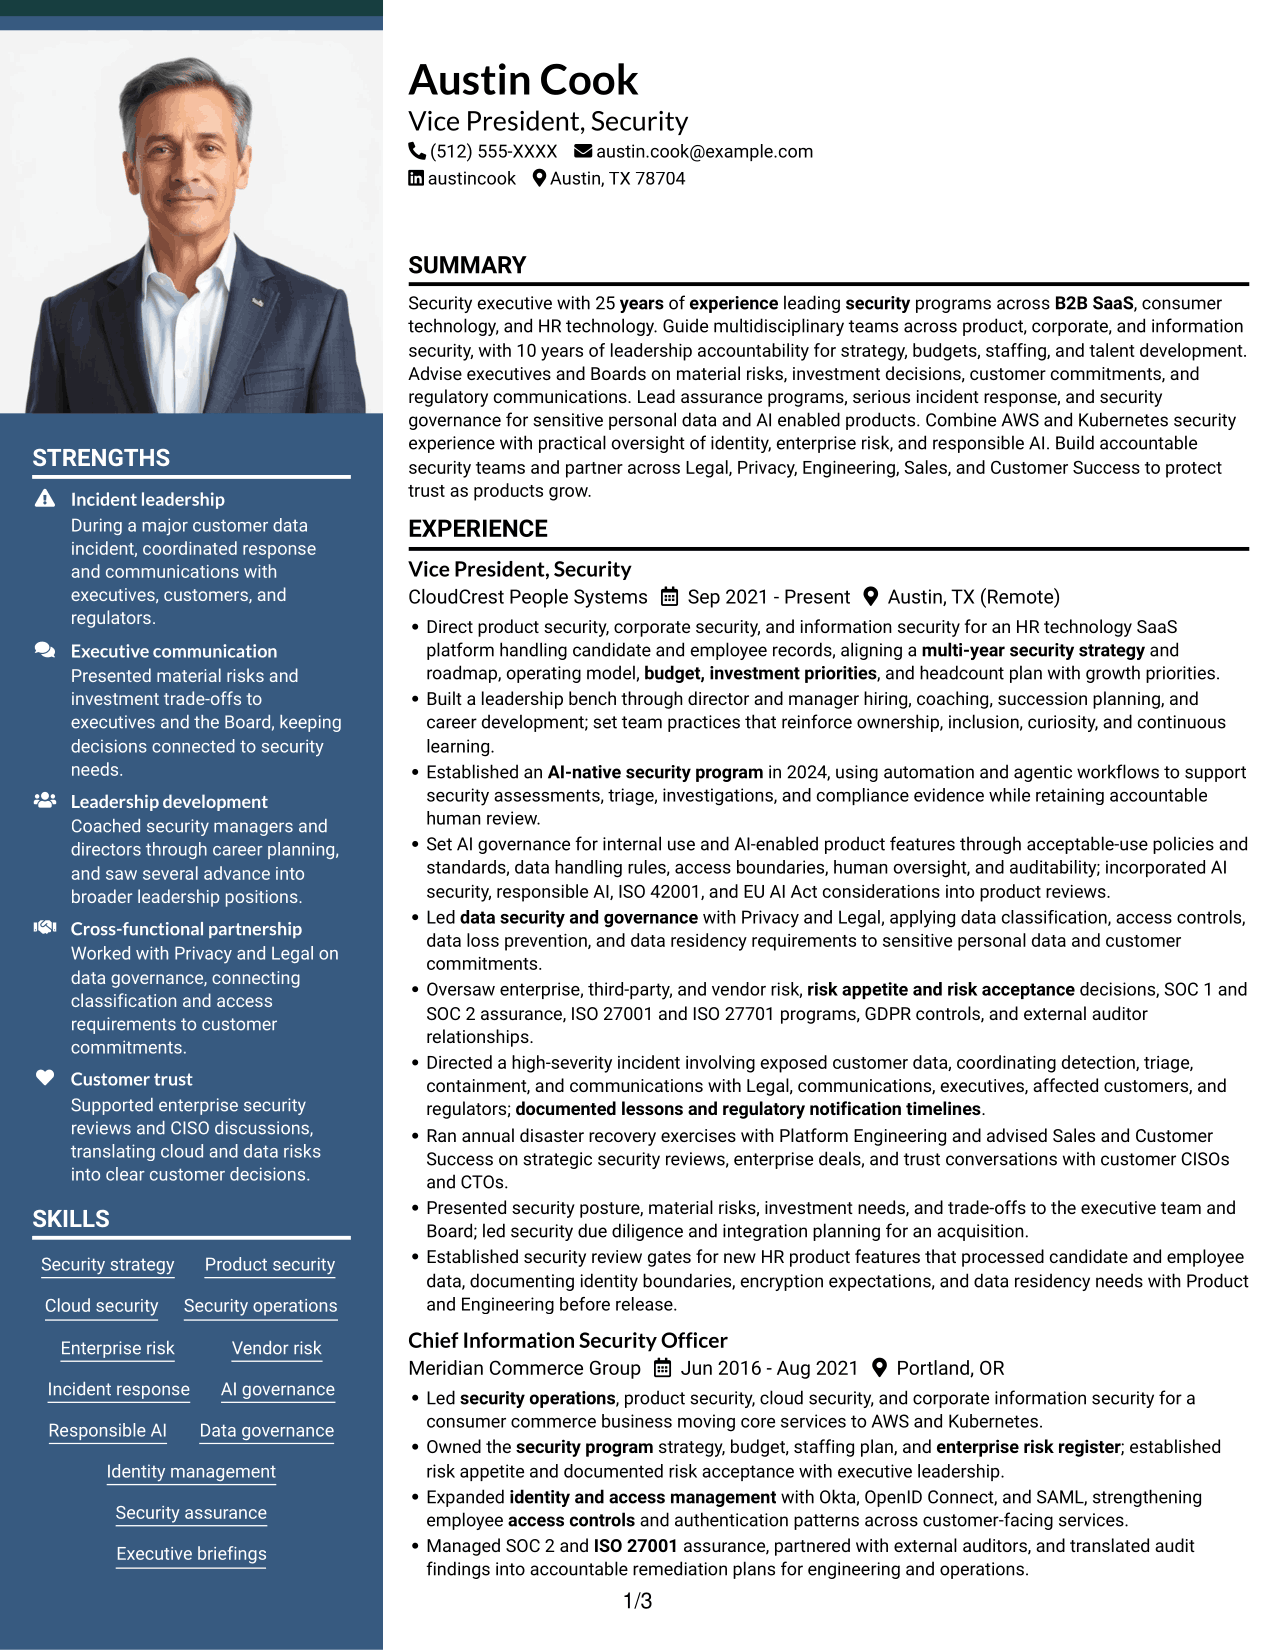
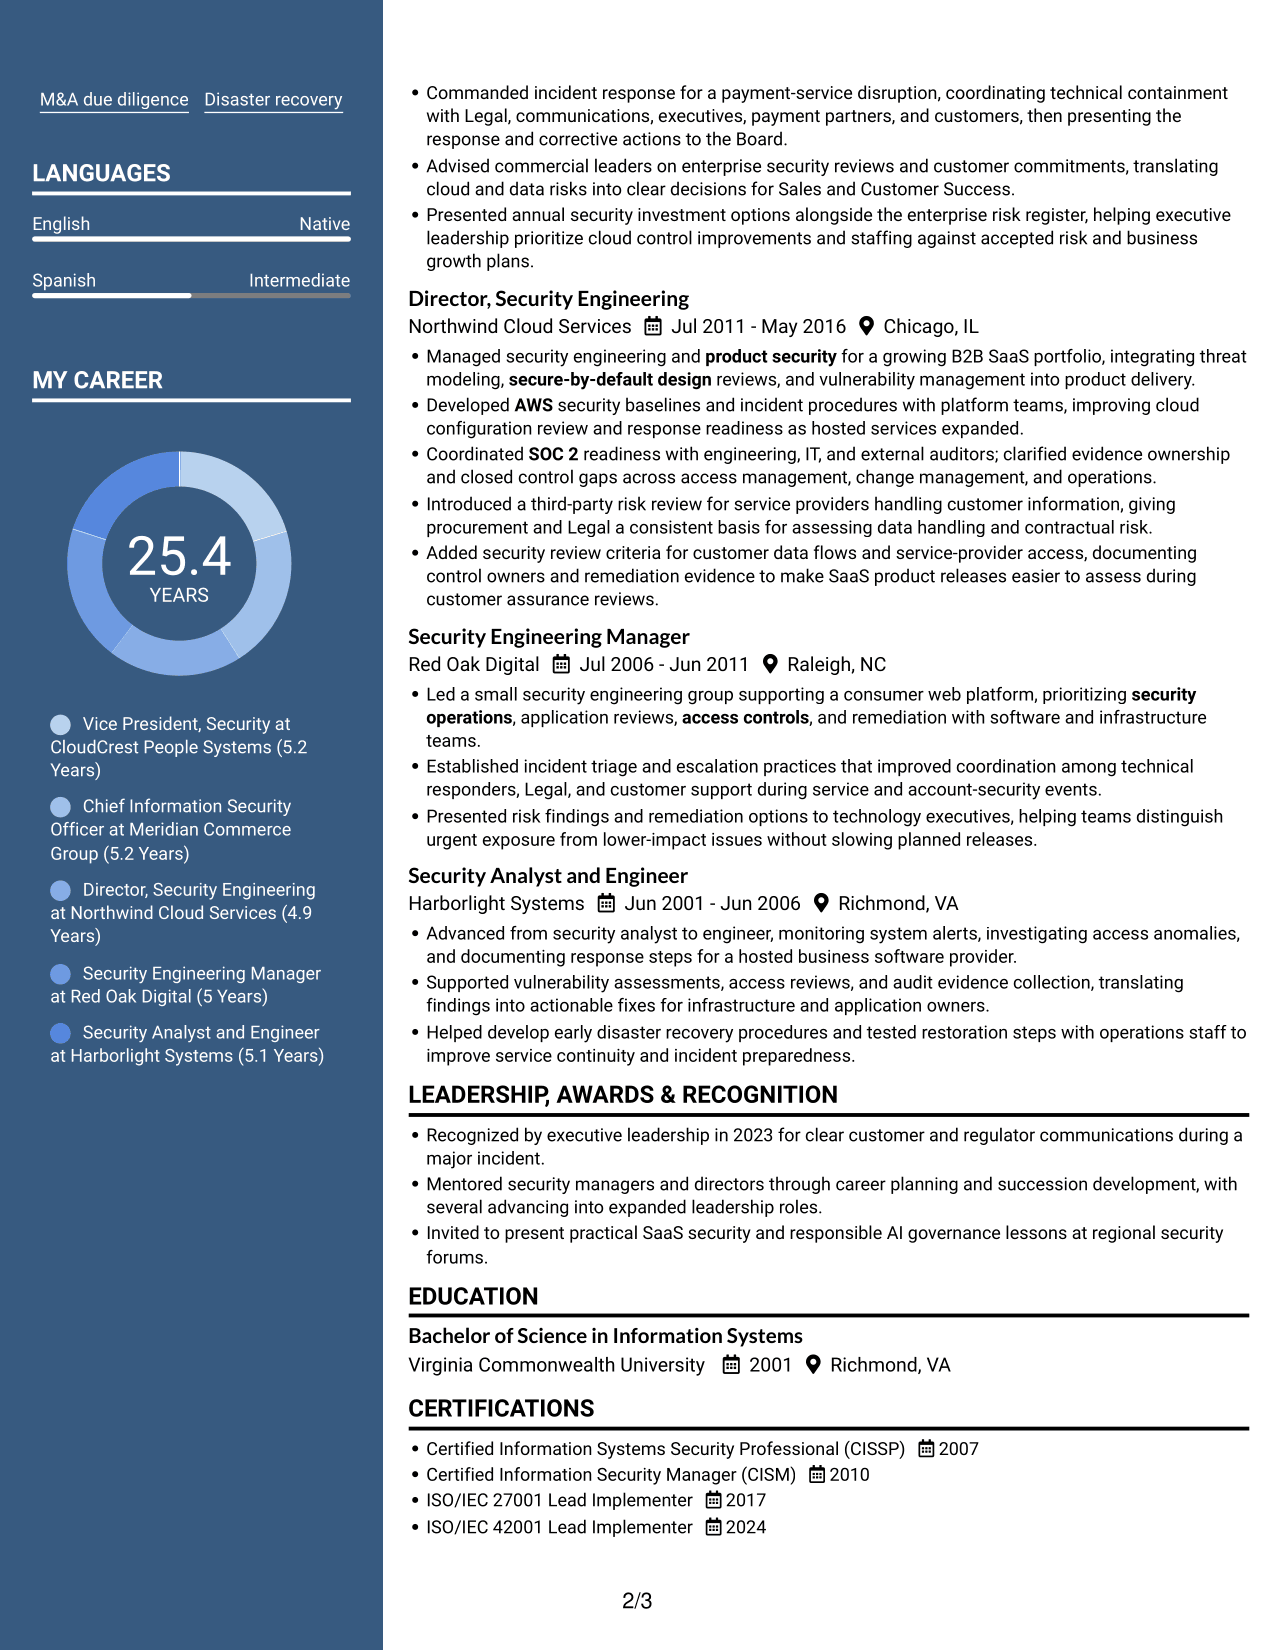
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two-column body gives career history and supporting sections separate places to scan.
  • Chronological experience stays legible while education and credentials remain easy to find.
  • The header photo adds a visual identifier while the body carries qualification details.

Best For

  • Photo-forward resume presentation
  • Executive resumes with broad experience
  • Career history with supporting sections
  • Separate skills and education details
  • Visual identification in the header
 

#6 Colored Two Column Format Resume Example

Colored Two Column Format uses two body columns to keep career information and supporting resume sections in parallel areas.
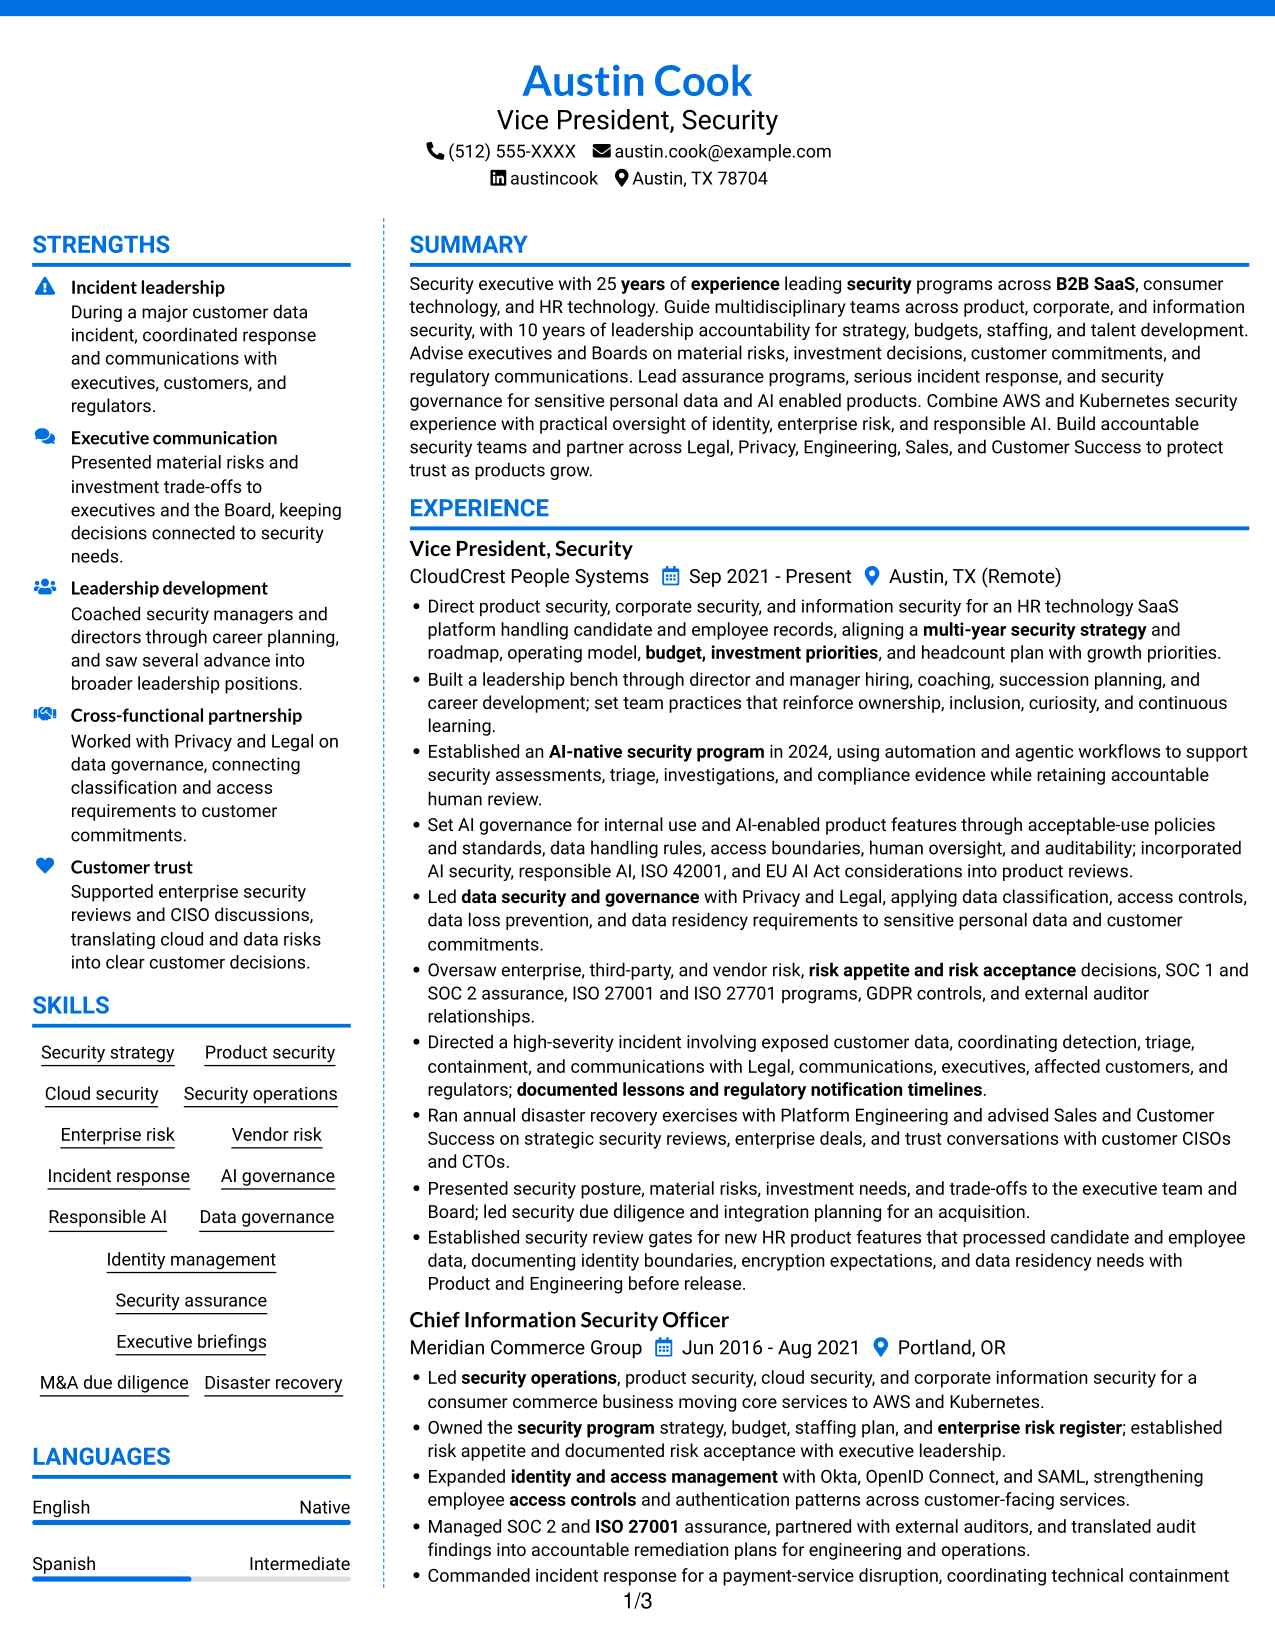
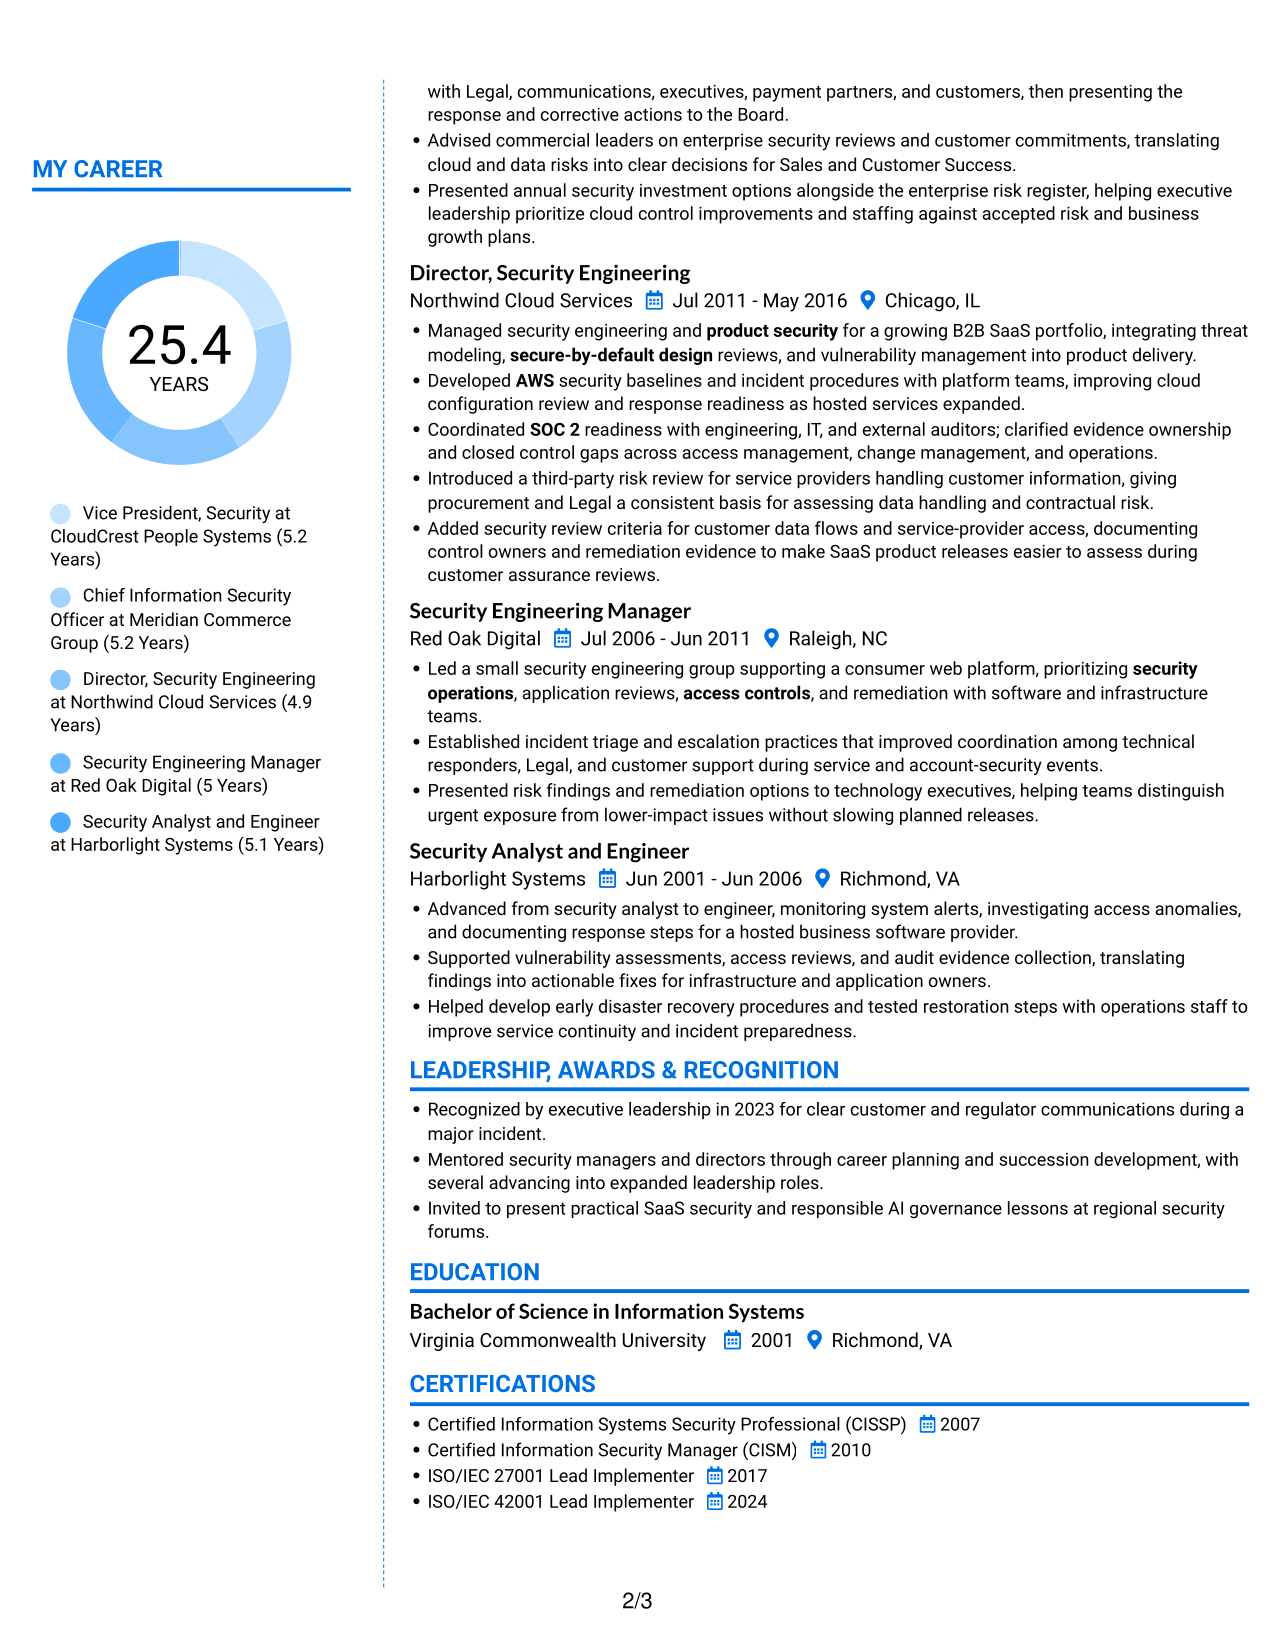
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Parallel columns give career history and supporting qualifications distinct reading areas.
  • Section breaks help reviewers find experience, skills, and education without losing their place.
  • The two-part structure accommodates both leadership scope and detailed credentials.

Best For

  • Resumes balancing breadth and detail
  • Career history with varied responsibilities
  • Skills alongside experience
  • Education and credential details
  • Review across distinct resume sections
 

#7 Stylish Two Column Designer Format Resume Example

Stylish Two Column Designer Format uses a two-column resume body, giving reviewers separate areas for career history and other sections.
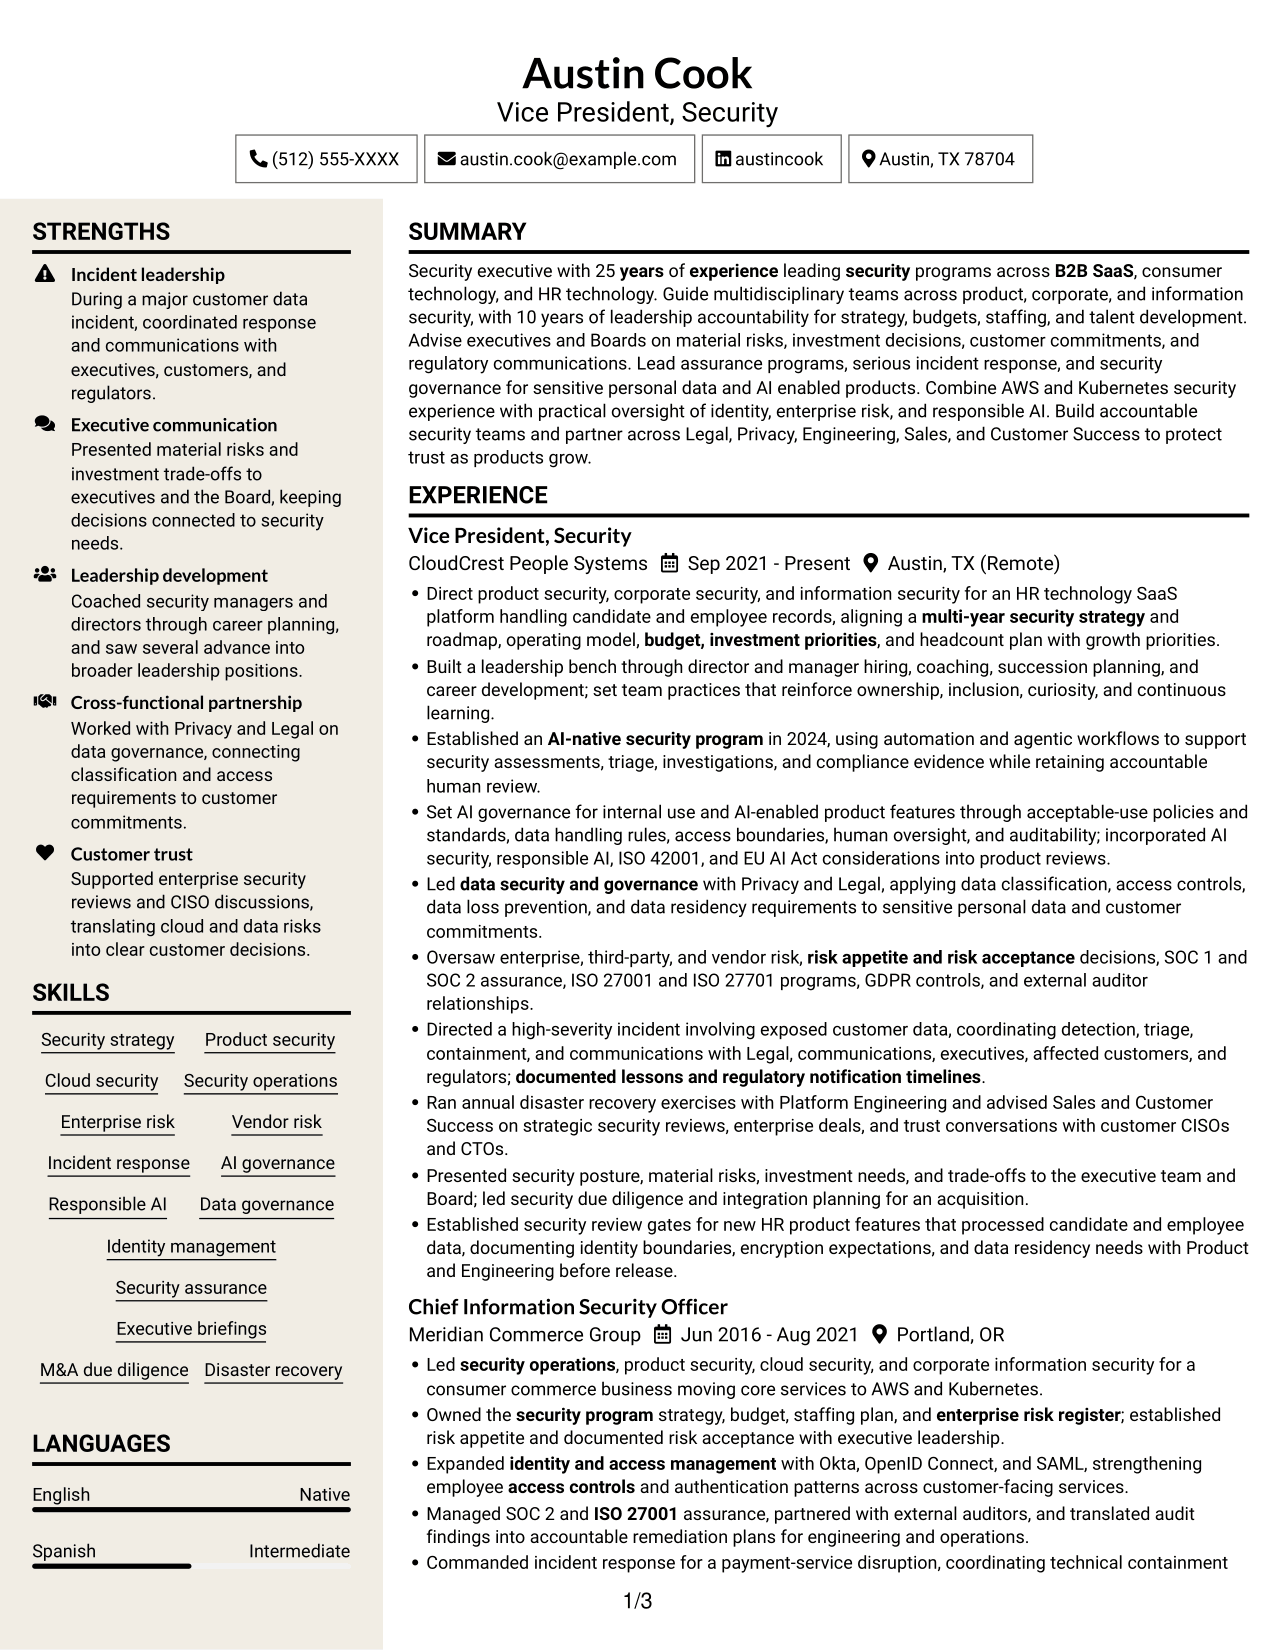
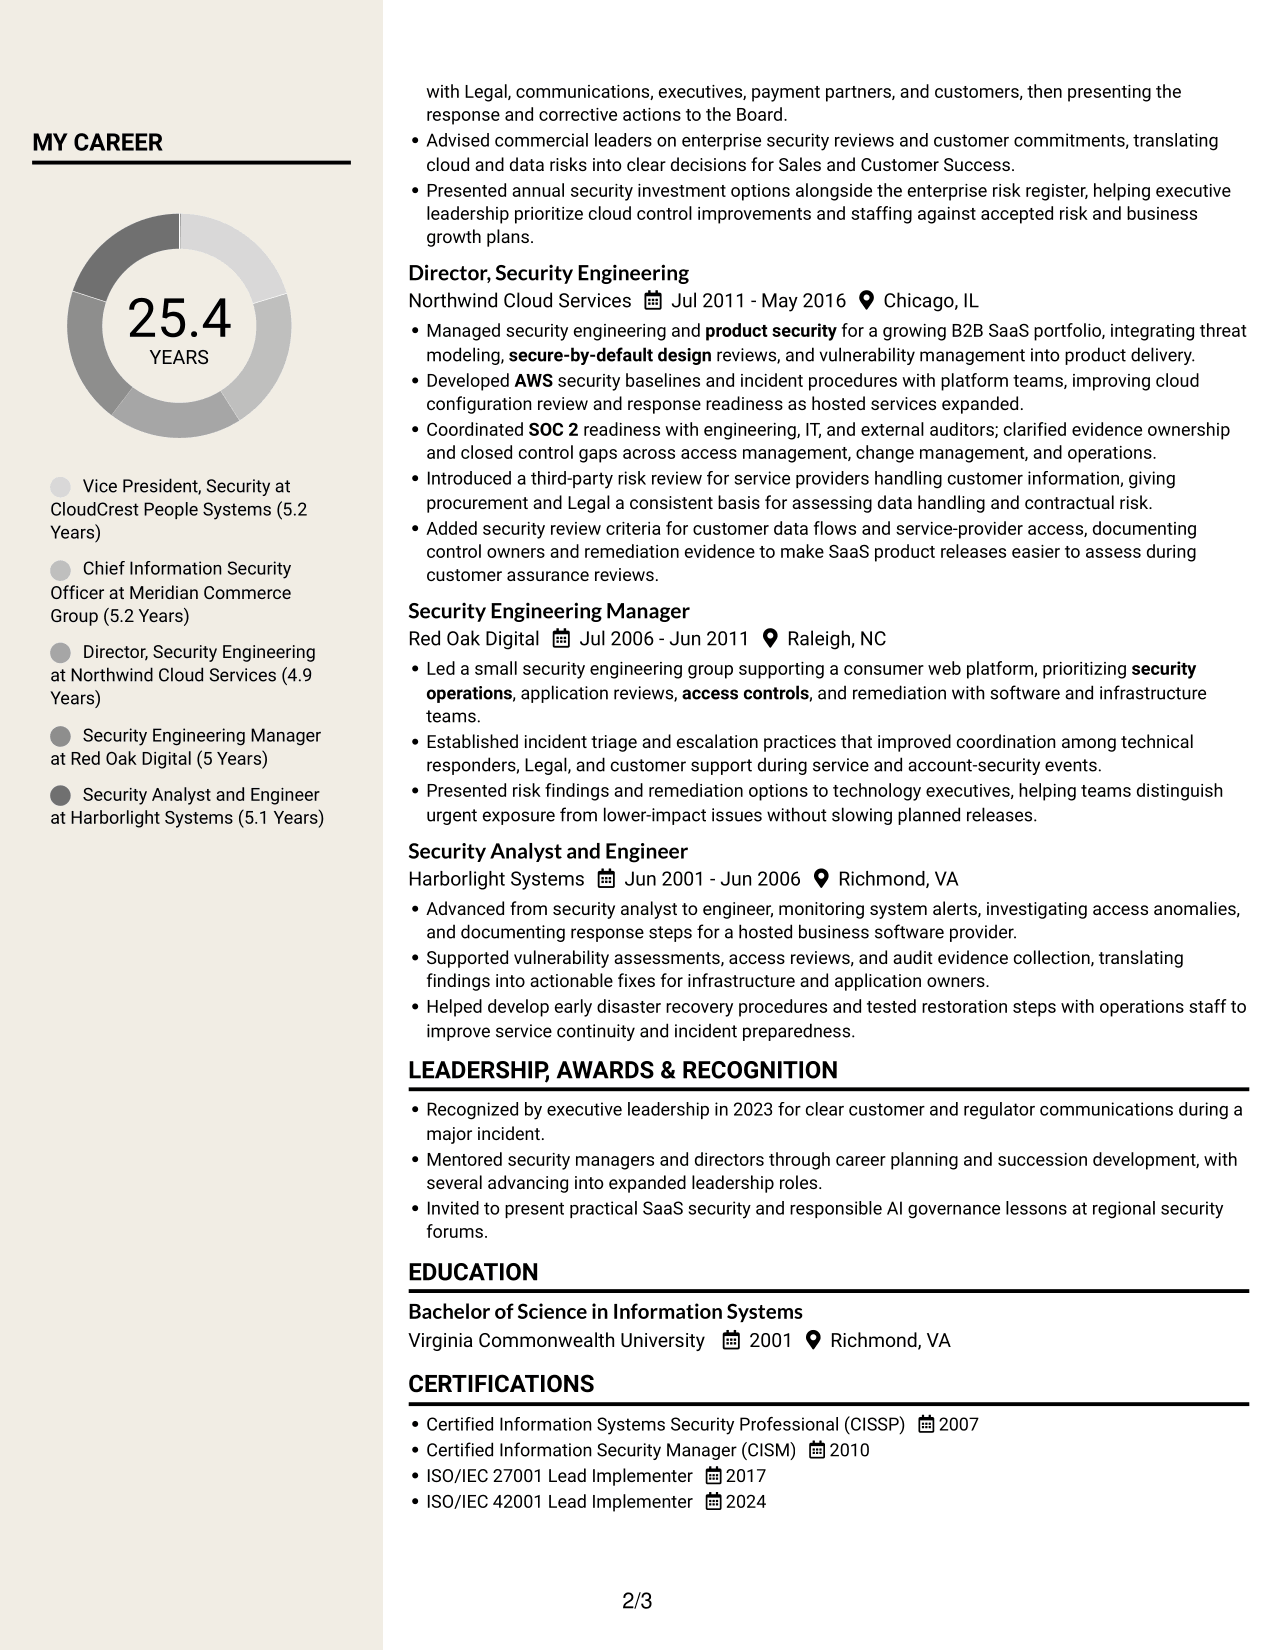
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • The paired columns distinguish career progression from supporting resume information.
  • Separate content areas let recruiters locate education and credentials without retracing the work history.
  • Skills and achievements can be reviewed alongside the broader leadership record.

Best For

  • Executive resumes with varied content
  • Paired career and supporting sections
  • Leadership history with achievements
  • Fast review of education and credentials
  • Skills considered with career progression


Why Build Your VP, Security - SaaS and AI Security Resume with ResumeInMinutes

ResumeInMinutes helps you arrange executive security experience, technical strengths, and credentials in a resume that is easy to review. Use the editor to shape the content around your scope and the evidence most relevant to this role.

  • Distinct resume layouts
  • Clear section structure
  • Role-focused keyword guidance
  • Organized experience and skills
  • Image previews for comparison
  • Resume editing in the editor

Present security strategy, AI governance, risk oversight, assurance, and incident leadership with direct language and concrete evidence. Keep the layout simple enough for quick review and automated parsing.


See Also


Frequently Asked Questions

Are these VP, Security - SaaS and AI Security resume templates ATS-friendly?

They use organized resume sections and readable headings. For stronger ATS alignment, use relevant terms such as product security, cloud security, enterprise risk, AI governance, SOC 2, and ISO 27001 when they accurately describe your experience.

Do the previews show one resume in different layouts?

Yes. The examples show the resume content in different visual layouts. Compare the image previews, then open an example in the editor to review or customize its structure.

What should a VP, Security - SaaS and AI Security resume include?

Include a concise executive summary, leadership experience, security strategy and risk ownership, relevant skills and tools, education, and certifications. Add clear evidence of incident leadership, assurance work, AI governance, and communication with executives or Boards when supported by your experience.

Which resume layout works well for a VP, Security role?

A clean layout with clear headings and a logical experience section makes executive scope easy to scan. Choose a design that gives space to strategy, team leadership, technical oversight, risk, and measurable outcomes without crowding the page.

How can I show both executive leadership and technical security knowledge?

Use the summary and recent experience to show strategy, budgets, team leadership, and executive decisions. Add relevant technical skills such as AWS, Kubernetes, Okta, OpenID Connect, or SAML, and connect them to specific work in your experience section.

Should I include a photo on my resume?

For U.S. applications, a resume without a photo is usually the safer choice. Keep the focus on your leadership, skills, and results.
ATS Score 100%

How we calculate this score

  • Keywords: 60% of the total. AI extracts keywords from your job description. If you do not provide one, a standard job description for the title matching your resume is used. This is not a match to a specific vacancy.
  • Text-based resume: 20%. The text resume assessed here receives 100 for this part.
  • Resume quality: 20%. We start at 100 and subtract points for issues found by our resume checks, down to a minimum of zero.
  • Keyword coverage = round(100 × confirmed matches ÷ total keywords). Exact matches and supported equivalents verified by AI receive full credit; unsupported keywords receive none. Live text checks use the saved equivalents and do not request a new AI review. Without keywords, no overall ATS score is available.
  • Final score = 60% of keyword coverage + 20% of the text score + 20% of the quality score, rounded to a whole number. Without keywords, no overall ATS score is available.

What this score means

Our scores are estimates, not employer ratings. They may contain errors and do not guarantee accurate parsing, a ranking, an interview, or a job. Check your document against the employer’s requirements. You are responsible for relying on this score.

Terms and Conditions

Score weights: Keywords 60% · Text based resume 20% · Resume quality 20%

Keyword coverage: 46 of 46 (100%) · Resume quality: 100%

Resume quality 100% · Weight 20% · Issues (0)

Details
  • ✓Name present: Austin Cook
  • ✓Email format: austin.cook@example.com
  • ✓Phone format: (512) 555-XXXX
  • ✓Experience 1: Job title: Vice President, Security
  • ✓Experience 1: Company name: CloudCrest People Systems
  • ✓Experience 1: Work location: Austin, TX (Remote)
  • ✓Experience 1: Employment dates: Sep 2021 - Present
  • ✓Experience 1: Description or achievements: Present
  • ✓Experience 2: Job title: Chief Information Security Officer
  • ✓Experience 2: Company name: Meridian Commerce Group
  • ✓Experience 2: Work location: Portland, OR
  • ✓Experience 2: Employment dates: Jun 2016 - Aug 2021
  • ✓Experience 2: Description or achievements: Present
  • ✓Experience 3: Job title: Director, Security Engineering
  • ✓Experience 3: Company name: Northwind Cloud Services
  • ✓Experience 3: Work location: Chicago, IL
  • ✓Experience 3: Employment dates: Jul 2011 - May 2016
  • ✓Experience 3: Description or achievements: Present
  • ✓Experience 4: Job title: Security Engineering Manager
  • ✓Experience 4: Company name: Red Oak Digital
  • ✓Experience 4: Work location: Raleigh, NC
  • ✓Experience 4: Employment dates: Jul 2006 - Jun 2011
  • ✓Experience 4: Description or achievements: Present
  • ✓Experience 5: Job title: Security Analyst and Engineer
  • ✓Experience 5: Company name: Harborlight Systems
  • ✓Experience 5: Work location: Richmond, VA
  • ✓Experience 5: Employment dates: Jun 2001 - Jun 2006
  • ✓Experience 5: Description or achievements: Present
  • ✓No placeholder fields
  • ✓No repeated achievement bullets
  • ✓No empty bullets

No issues found by the current checks.

Text Based Resume 100% · Weight 20%

Parsed text
Austin Cook
Vice President, Security
(512) 555-XXXX
austincook
austin.cook@example.com
Austin, TX 78704
STRENGTHS
Incident leadership
During a major customer data incident, coordinated response and communications with executives, customers, and regulators.
Executive communication
Presented material risks and investment trade-offs to executives and the Board, keeping decisions connected to security needs.
Leadership development
Coached security managers and directors through career planning, and saw several advance into broader leadership positions.
Cross-functional partnership
Worked with Privacy and Legal on data governance, connecting classification and access requirements to customer commitments.
Customer trust
Supported enterprise security reviews and CISO discussions, translating cloud and data risks into clear customer decisions.
SUMMARY
Security executive with 25 years of experience leading security programs across B2B SaaS, consumer technology, and HR technology. Guide multidisciplinary teams across product, corporate, and information security, with 10 years of leadership accountability for strategy, budgets, staffing, and talent development. Advise executives and Boards on material risks, investment decisions, customer commitments, and regulatory communications. Lead assurance programs, serious incident response, and security governance for sensitive personal data and AI enabled products. Combine AWS and Kubernetes security experience with practical oversight of identity, enterprise risk, and responsible AI. Build accountable security teams and partner across Legal, Privacy, Engineering, Sales, and Customer Success to protect trust as products grow.
EXPERIENCE
Vice President, Security
CloudCrest People Systems
Sep 2021 - Present
Austin, TX (Remote)
Direct product security, corporate security, and information security for an HR technology SaaS platform handling candidate and employee records, aligning a multi-year security strategy and roadmap, operating model, budget, investment priorities, and headcount plan with growth priorities.
Built a leadership bench through director and manager hiring, coaching, succession planning, and career development; set team practices that reinforce ownership, inclusion, curiosity, and continuous learning.
Established an AI-native security program in 2024, using automation and agentic workflows to support security assessments, triage, investigations, and compliance evidence while retaining accountable human review.
Set AI governance for internal use and AI-enabled product features through acceptable-use policies and standards, data handling rules, access boundaries, human oversight, and auditability; incorporated AI security, responsible AI, ISO 42001, and EU AI Act considerations into product reviews.
Led data security and governance with Privacy and Legal, applying data classification, access controls, data loss prevention, and data residency requirements to sensitive personal data and customer commitments.
Oversaw enterprise, third-party, and vendor risk, risk appetite and risk acceptance decisions, SOC 1 and SOC 2 assurance, ISO 27001 and ISO 27701 programs, GDPR controls, and external auditor relationships.
Directed a high-severity incident involving exposed customer data, coordinating detection, triage, containment, and communications with Legal, communications, executives, affected customers, and regulators; documented lessons and regulatory notification timelines.
Ran annual disaster recovery exercises with Platform Engineering and advised Sales and Customer Success on strategic security reviews, enterprise deals, and trust conversations with customer CISOs and CTOs.
Presented security posture, material risks, investment needs, and trade-offs to the executive team and Board; led security due diligence and integration planning for an acquisition.
Established security review gates for new HR product features that processed candidate and employee data, documenting identity boundaries, encryption expectations, and data residency needs with Product and Engineering before release.
Chief Information Security Officer
Meridian Commerce Group
Jun 2016 - Aug 2021
Portland, OR
Led security operations, product security, cloud security, and corporate information security for a consumer commerce business moving core services to AWS and Kubernetes.
Owned the security program strategy, budget, staffing plan, and enterprise risk register; established risk appetite and documented risk acceptance with executive leadership.
Expanded identity and access management with Okta, OpenID Connect, and SAML, strengthening employee access controls and authentication patterns across customer-facing services.
Managed SOC 2 and ISO 27001 assurance, partnered with external auditors, and translated audit findings into accountable remediation plans for engineering and operations.
Commanded incident response for a payment-service disruption, coordinating technical containment with Legal, communications, executives, payment partners, and customers, then presenting the response and corrective actions to the Board.
Advised commercial leaders on enterprise security reviews and customer commitments, translating cloud and data risks into clear decisions for Sales and Customer Success.
Presented annual security investment options alongside the enterprise risk register, helping executive leadership prioritize cloud control improvements and staffing against accepted risk and business growth plans.
Director, Security Engineering
Northwind Cloud Services
Jul 2011 - May 2016
Chicago, IL
Managed security engineering and product security for a growing B2B SaaS portfolio, integrating threat modeling, secure-by-default design reviews, and vulnerability management into product delivery.
Developed AWS security baselines and incident procedures with platform teams, improving cloud configuration review and response readiness as hosted services expanded.
Coordinated SOC 2 readiness with engineering, IT, and external auditors; clarified evidence ownership and closed control gaps across access management, change management, and operations.
Introduced a third-party risk review for service providers handling customer information, giving procurement and Legal a consistent basis for assessing data handling and contractual risk.
Added security review criteria for customer data flows and service-provider access, documenting control owners and remediation evidence to make SaaS product releases easier to assess during customer assurance reviews.
Security Engineering Manager
Red Oak Digital
Jul 2006 - Jun 2011
Raleigh, NC
Led a small security engineering group supporting a consumer web platform, prioritizing security operations, application reviews, access controls, and remediation with software and infrastructure teams.
Established incident triage and escalation practices that improved coordination among technical responders, Legal, and customer support during service and account-security events.
Presented risk findings and remediation options to technology executives, helping teams distinguish urgent exposure from lower-impact issues without slowing planned releases.
Security Analyst and Engineer
Harborlight Systems
Jun 2001 - Jun 2006
Richmond, VA
Advanced from security analyst to engineer, monitoring system alerts, investigating access anomalies, and documenting response steps for a hosted business software provider.
Supported vulnerability assessments, access reviews, and audit evidence collection, translating findings into actionable fixes for infrastructure and application owners.
Helped develop early disaster recovery procedures and tested restoration steps with operations staff to improve service continuity and incident preparedness.
SKILLS
M&A due diligence
Security strategy
Cloud security
Incident response
Responsible AI
Enterprise risk
Identity management
Security assurance
Executive briefings
Security operations
Data governance
Disaster recovery
Product security
AI governance
Vendor risk
LANGUAGES
English
Native
Spanish
Intermediate
MY CAREER
25.4Years
Vice President, Security at CloudCrest People Systems (5.2 Years)
Chief Information Security Officer at Meridian Commerce Group (5.2 Years)
Director, Security Engineering at Northwind Cloud Services (4.9 Years)
Security Engineering Manager at Red Oak Digital (5 Years)
Security Analyst and Engineer at Harborlight Systems (5.1 Years)
LEADERSHIP, AWARDS & RECOGNITION
Recognized by executive leadership in 2023 for clear customer and regulator communications during a major incident.
Mentored security managers and directors through career planning and succession development, with several advancing into expanded leadership roles.
Invited to present practical SaaS security and responsible AI governance lessons at regional security forums.
EDUCATION
Bachelor of Science in Information Systems
Virginia Commonwealth University
2001
Richmond, VA
CERTIFICATIONS
Certified Information Systems Security Professional (CISSP)
2007
Certified Information Security Manager (CISM)
2010
ISO/IEC 27001 Lead Implementer
2017
ISO/IEC 42001 Lead Implementer
2024
TECHNICAL SKILLS
Cloud Platforms: Amazon Web Services, Microsoft Azure, Google Cloud Platform
Container Platforms: Kubernetes, Docker, Amazon Elastic Kubernetes Service
Identity Platforms: Okta, Microsoft Entra ID, Ping Identity
Identity Standards: OpenID Connect, SAML, OAuth 2.0
Security Monitoring: Splunk, Microsoft Sentinel, Elastic Security
Endpoint Security: CrowdStrike Falcon, Microsoft Defender for Endpoint, SentinelOne
Vulnerability Tools: Tenable, Qualys, Rapid7 InsightVM
Web Security: OWASP ZAP, Burp Suite, NGINX
Data Stores: Amazon RDS, PostgreSQL, MongoDB
Infrastructure as Code: Terraform, AWS CloudFormation, Ansible
Network Security: Palo Alto Networks NGFW, AWS WAF, Cloudflare WAF
PROFESSIONAL AFFILIATIONS
Member of (ISC)², engaging with the professional community on information security practice and development.
Member of ISACA, participating in a professional community focused on security, risk, and assurance.

Matched keywords (46)

  • 25 years of experience leading security programsOriginal keyword in JD: 12+ years of security experience
  • 10 years of leadership accountability for strategy, budgets, staffing, and talent developmentOriginal keyword in JD: 5+ years leading a multidisciplinary security organization
  • Owned the security program strategy, budget, staffing plan, and enterprise risk registerOriginal keyword in JD: End-to-end security program ownership
  • aligning a multi-year security strategy and roadmapOriginal keyword in JD: Security strategy and multi-year roadmap
  • operating modelOriginal keyword in JD: Security organization operating model
  • budget, investment prioritiesOriginal keyword in JD: Security budget and investment planning
  • headcount planOriginal keyword in JD: Security staffing and headcount planning
  • director and manager hiring, coaching, succession planningOriginal keyword in JD: Leadership hiring, coaching, and succession planning
  • enterprise risk registerOriginal keyword in JD: Enterprise risk management
  • Oversaw enterprise, third-party, and vendor riskOriginal keyword in JD: Third-party and vendor risk management
  • risk appetite and risk acceptance
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 27701
  • ISO 42001Original keyword in JD: ISO 42001 OR ISO 27701 OR GDPR OR EU AI Act experience
  • AI-native security program
  • AI security
  • AI governance
  • Responsible AI
  • using automation and agentic workflows to support security assessments, triage, investigations, and compliance evidenceOriginal keyword in JD: Agentic workflows and security automation
  • security governance for sensitive personal data and AI enabled productsOriginal keyword in JD: AI-enabled product security
  • data security and governance
  • data classification
  • access controls
  • data loss prevention
  • data residency
  • secure-by-default design
  • Security operations
  • Cloud security
  • AWS
  • Kubernetes
  • Product security
  • identity and access management
  • OktaOriginal keyword in JD: Okta OR OpenID Connect OR SAML
  • Incident response
  • disaster recovery exercises
  • documented lessons and regulatory notification timelinesOriginal keyword in JD: Regulatory communications and notification timelines
  • external auditor relationships
  • Presented security posture, material risks, investment needs, and trade-offs to the executive team and BoardOriginal keyword in JD: Executive and Board security briefings
  • advised Sales and Customer Success on strategic security reviews, enterprise deals, and trust conversations with customer CISOs and CTOsOriginal keyword in JD: Customer security reviews and enterprise deal support
  • led security due diligence and integration planning for an acquisitionOriginal keyword in JD: Security due diligence and M&A integration
  • B2B SaaSOriginal keyword in JD: B2B SaaS OR consumer technology experience
  • CISOOriginal keyword in JD: Head of Security OR CISO OR Vice President of Security experience
  • ISO 42001
  • applying data classification, access controls, data loss prevention, and data residency requirements to sensitive personal data and customer commitmentsOriginal keyword in JD: HR technology and sensitive personal data

Missing keywords (0)

No missing keywords.

Disclaimer: All names, images, contact information, employment histories, achievements, security clearances, military credentials, and other qualifications shown in this content are fictional and used for illustrative purposes only. Any resemblance to actual persons, living or deceased, is purely coincidental.

Resume and cover-letter examples and recommendations in this article reflect general best practices and professional experience and are provided for guidance only. Results may vary based on role, industry, region, and hiring organization.

Content Accuracy and Verification: To the fullest extent permitted by applicable law, we do not represent or warrant that resume or cover-letter guidance, examples, recommendations, or related information are accurate, complete, current, error-free, or suitable for any particular purpose. You are responsible for independently reviewing and verifying the information before relying on it.

ATS and Cover-Letter Scores: ATS scores are estimates calculated using our own formula, informed by publicly available guidance on resume formatting and keyword matching. They are not scores issued or endorsed by an ATS provider or employer. Cover-letter scores are also our own assessments. Parsing, weighting, screening criteria, and results vary between systems, employers, job descriptions, and document formats. No score guarantees successful parsing, a particular ranking, an interview, or employment. Use scores as general guidance and independently check your documents against the employer’s requirements. To the fullest extent permitted by applicable law, we accept no liability for errors in scores or parsing, or losses arising from reliance on these assessments. Nothing in this notice excludes liability or limits consumer rights that cannot lawfully be excluded or limited.

Terms and Conditions
 
> JP 1 1
PDF Footer and Margins Setup
The margins are applied to the document, and the footer shows up in the preview and the PDF

Footer Font Settings

Are you applying for a specific job
so we can tailor your resume to it?
Are you applying for a specific job
so we can tailor your cover letter to it?

Your data stays private and is never used for training.Privacy Policy

Type your details as text to generate a personalized resume Type your details as text to generate a personalized cover letter
Website link found! Ready to create resume from:

Your data stays private and is never used for training.Privacy Policy

Drag the into the box to verify you're human.
Drop here

My Resumes

Displaying {number_of_files} files (out of {total_of_all_files} total)
Name File Type Last Modified: Description:

Rename File

Filename already exists!

Delete Files

Warning: This action is irreversible. Once you click submit, the files will be permanently deleted.

Heading text
Upload From Computer Upload
Select From Existing
LinkedIn
Drag & Drop files anywhere in this tab, or

Uploaded Files

Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

My Files

Resumes or cover letters you create will appear here. No files available yet.
Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Add LinkedIn Profile PDF

You can download your LinkedIn profile as a PDF by opening linkedin.com in a web browser, clicking your profile photo, selecting the “More” or “Resources” button, and choosing “Save to PDF.” You can then attach the PDF using the Upload From Computer tab.

Paste Your LinkedIn Profile Text

If you have copied the LinkedIn profile text, paste it below. See how to copy your profile from LinkedIn

Select this to use the LinkedIn profile text for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Try these controls

<
>