US English


7 GRC Compliance Senior Analyst - IT/OT Security Compliance Resume Templates with Example
By Ria · Last Updated On October 19, 2026
Resume example — page 1

This guide shows you how to build a GRC Compliance Senior Analyst - IT/OT Security Compliance resume that presents your value clearly. You will learn how to organize relevant evidence and choose a format that supports quick review.

Strong resumes for this role connect risk assessment, GxP compliance, internal controls, and audit readiness to clear results. Use the examples to see how experience, skills, certifications such as CISA and CRISC, and measurable outcomes can work together.

The resume example is presented in 7 layouts. Compare the PNG image previews, then open an example in the editor to view or customize it.

What Makes a Strong GRC Compliance Senior Analyst - IT/OT Security Compliance Resume in 2026

A strong resume makes risk ownership, control work, and audit readiness easy to find. Use concise bullets to show the action taken and the result.

Include supported terms such as GxP, IT/OT security compliance, risk treatment, information governance, and KPI reporting. Add measures when available, such as a documented reduction in audit preparation time.

Note: Resume examples are for educational purposes only. Use only information that accurately reflects your experience and qualifications. References to real organizations do not imply affiliation or endorsement.

#1 Plain Two Column Format Resume Example

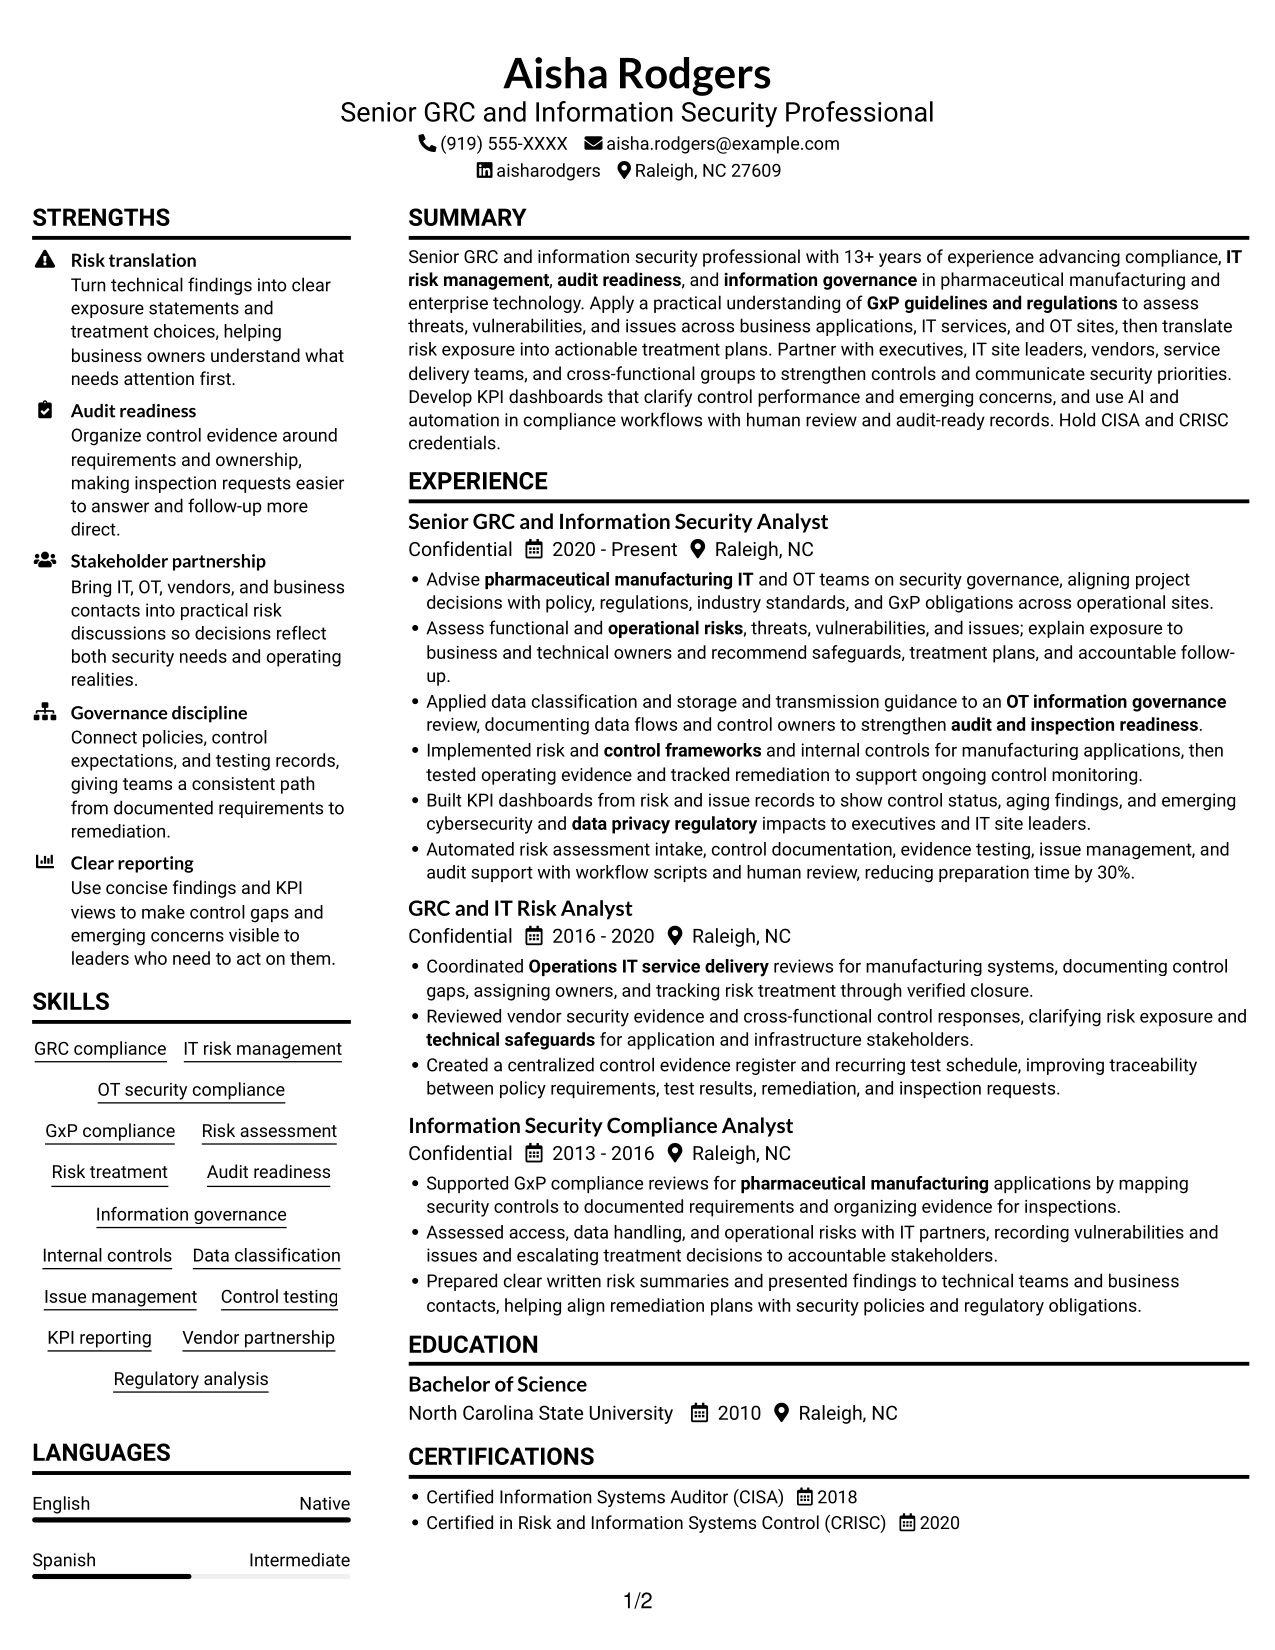
The Plain Two Column Format sets resume content in two columns, helping reviewers scan career history alongside supporting details.
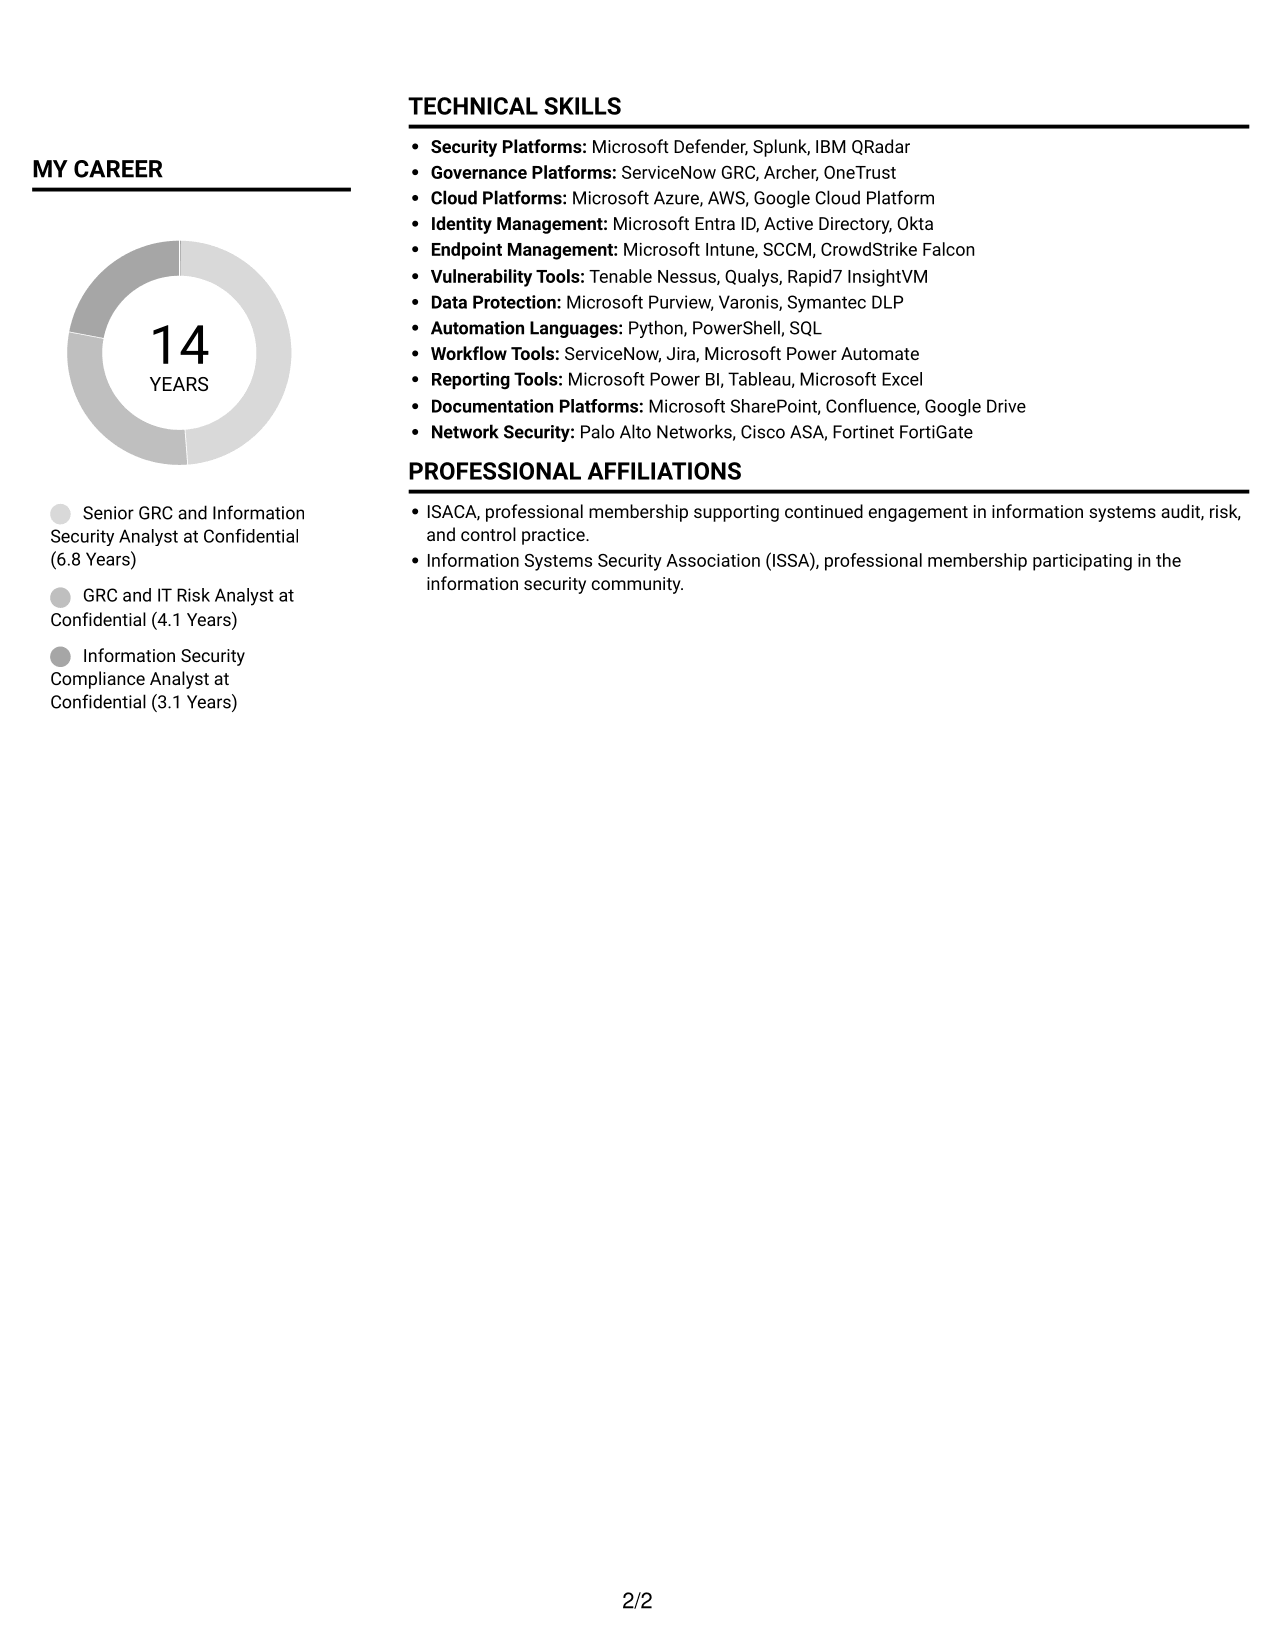
 
Resume example — page 1   Resume example — page 2

Resume Snapshot

  • 13+ years of experience
  • Pharmaceutical manufacturing and enterprise technology
  • CISA and CRISC
  • Bachelor of Science in Information Technology

Why This Format Works

  • Career history stays easy to follow while supporting sections remain distinct.
  • Skills and tools can be reviewed apart from education and credentials.
  • Consistent reading order helps recruiters move through achievements and control work.

Best For

  • Resumes with extensive career history
  • Experience paired with supporting sections
  • Skills and credentials needing quick reference
  • Detailed education and certification records
  • Two-column information organization

Resume Keywords

  • 13+ years of experience advancing compliance, IT risk management, audit readiness, and information governance in pharmaceutical manufacturing and enterprise technology.
  • Bachelor of Science
  • CISA
  • GxP guidelines and regulations
  • Assess functional and operational risks, threats, vulnerabilities, and issues
  • Information Security Compliance
  • OT security compliance
  • security governance
  • Assess functional and operational risks
  • recommend safeguards, treatment plans, and accountable follow-up
  • translate risk exposure into actionable treatment plans
  • technical safeguards
  • Internal controls
  • risk and control frameworks
  • Information governance
See all keywords
 

#2 Simple One Column Format Resume Example

The Simple One Column Format follows a single reading path, making it a practical choice for resumes reviewed from top to bottom.
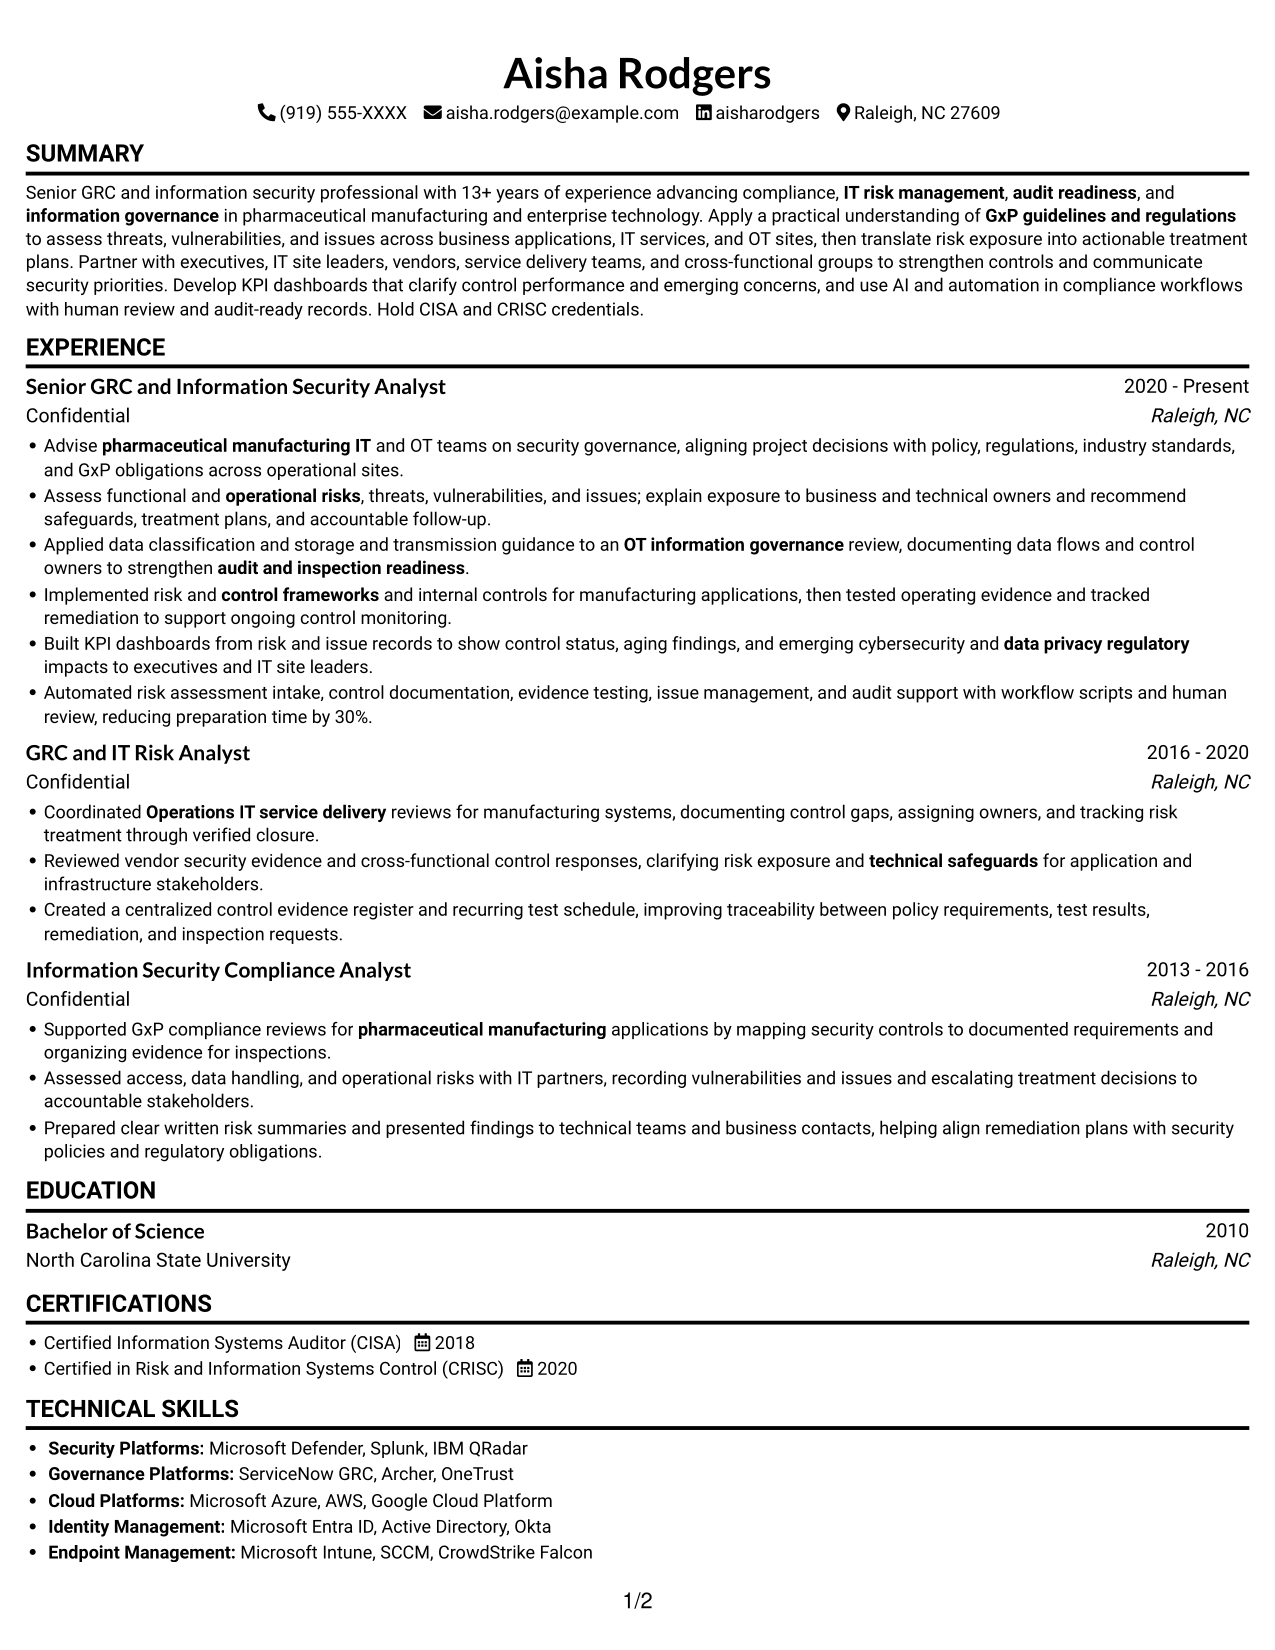
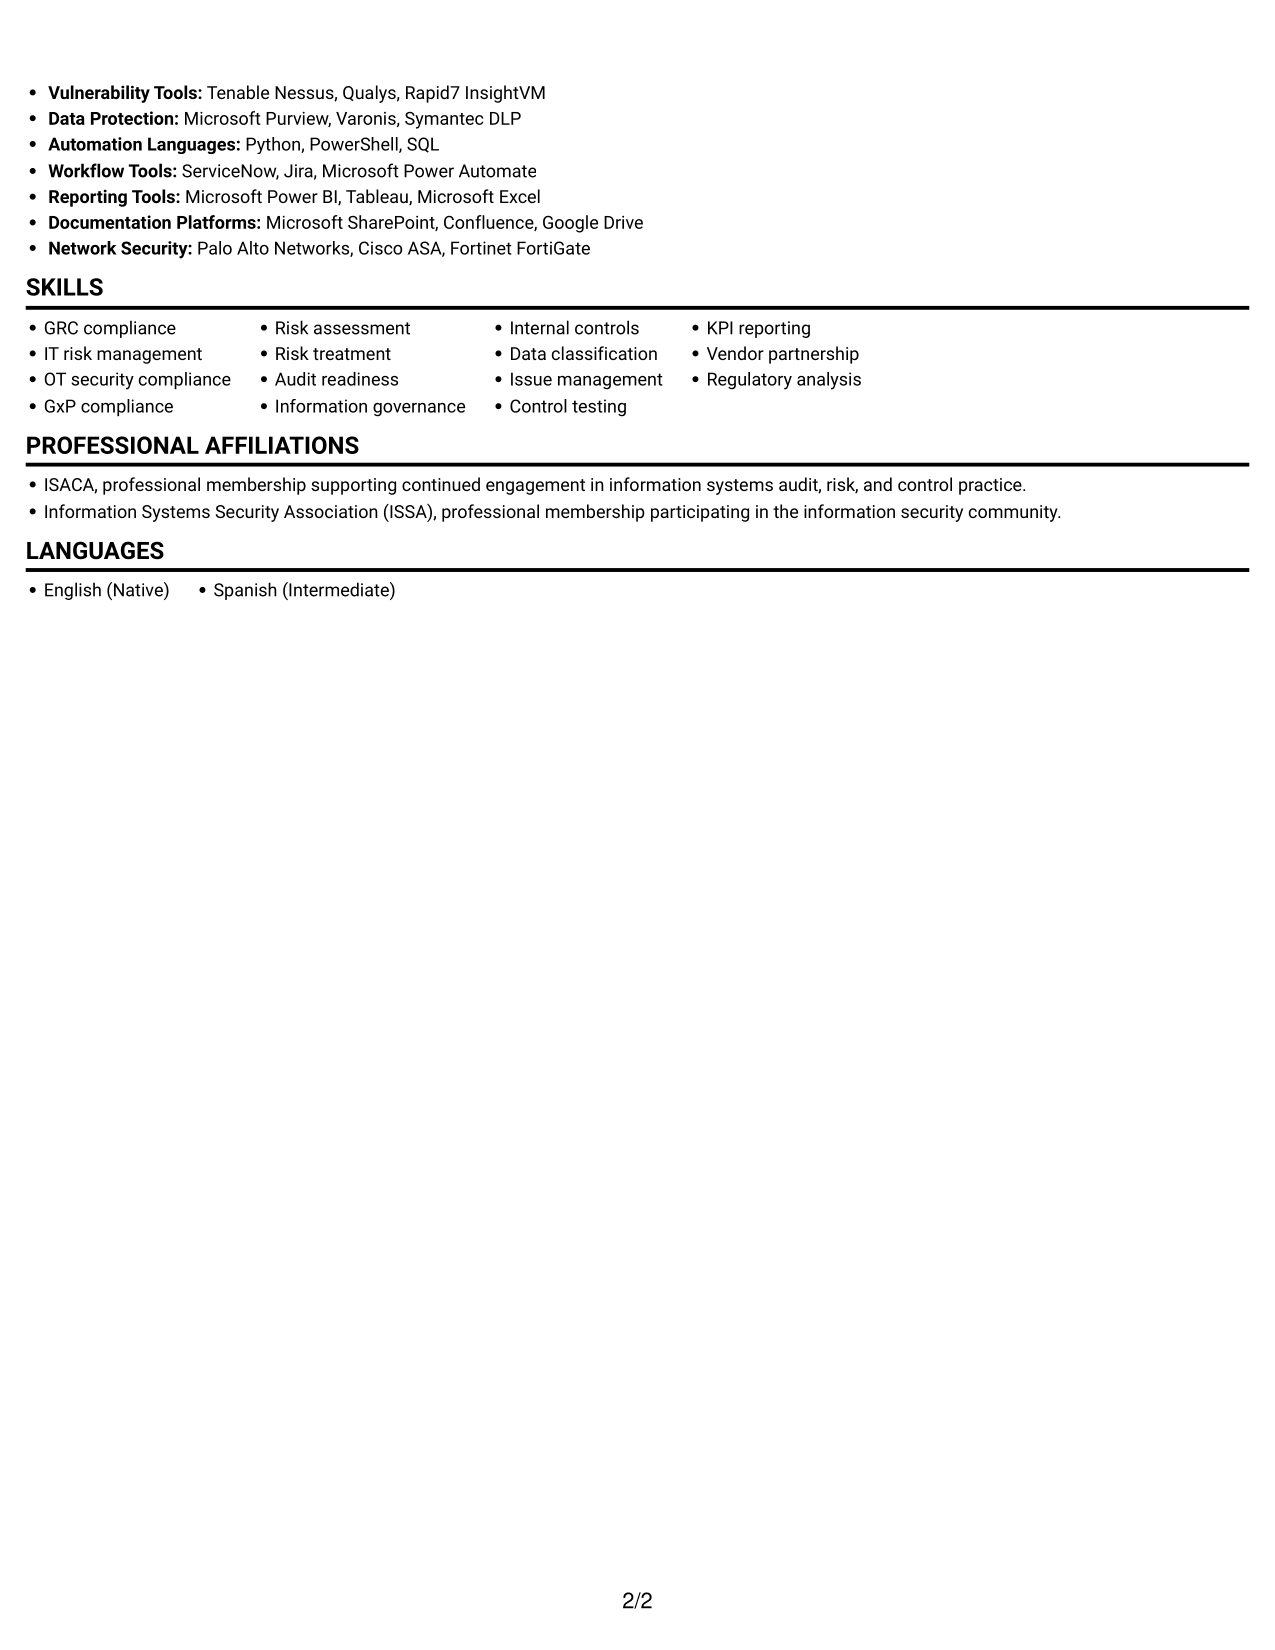
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • One continuous column gives experience entries a clear top-to-bottom sequence.
  • Section headings help reviewers locate skills, education, and certifications.
  • Achievement bullets remain in a predictable order for recruiter review.

Best For

  • Linear section-by-section review
  • Chronological experience narratives
  • Resumes with several distinct sections
  • Detailed achievement bullets
  • Simple reading order
 

#3 Clean Two Column Sidebar Format Resume Example

The Clean Two Column Sidebar Format groups resume content into two reading areas, helping reviewers move between experience and related details.
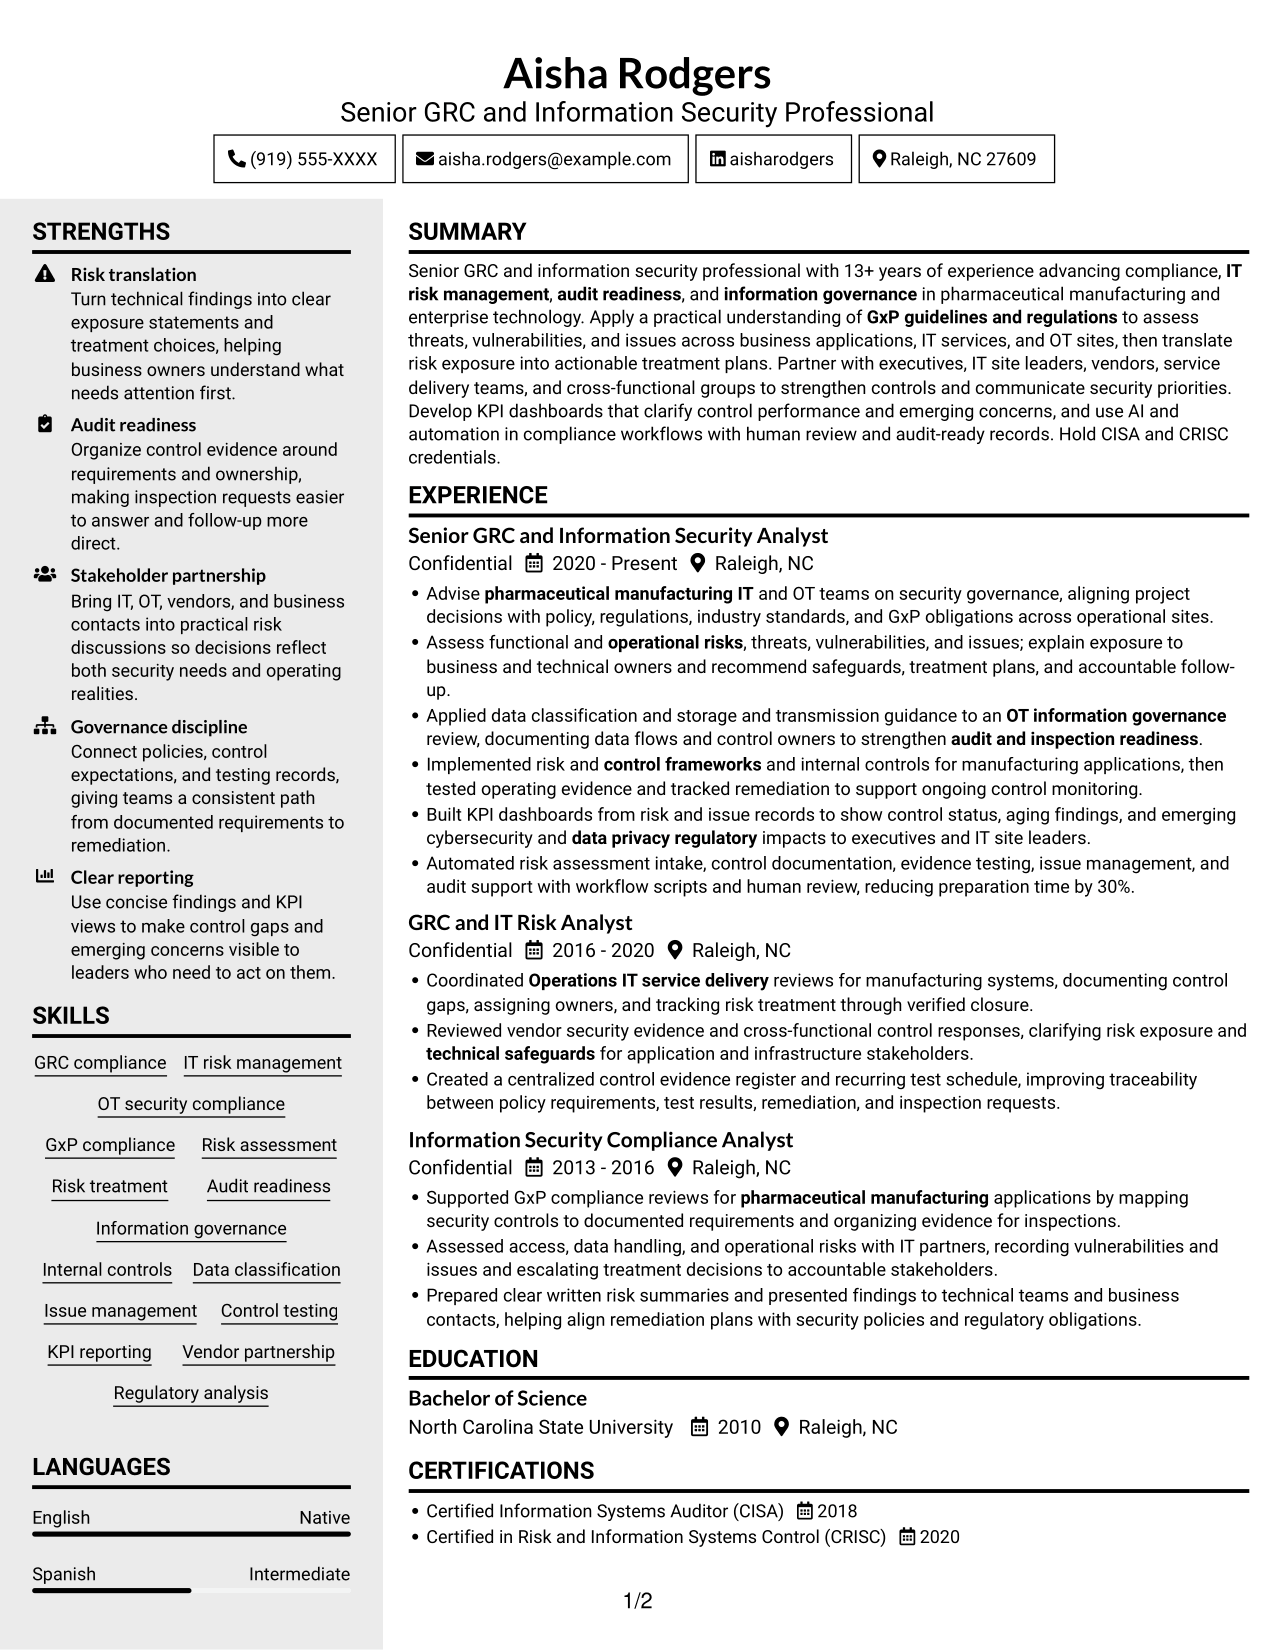
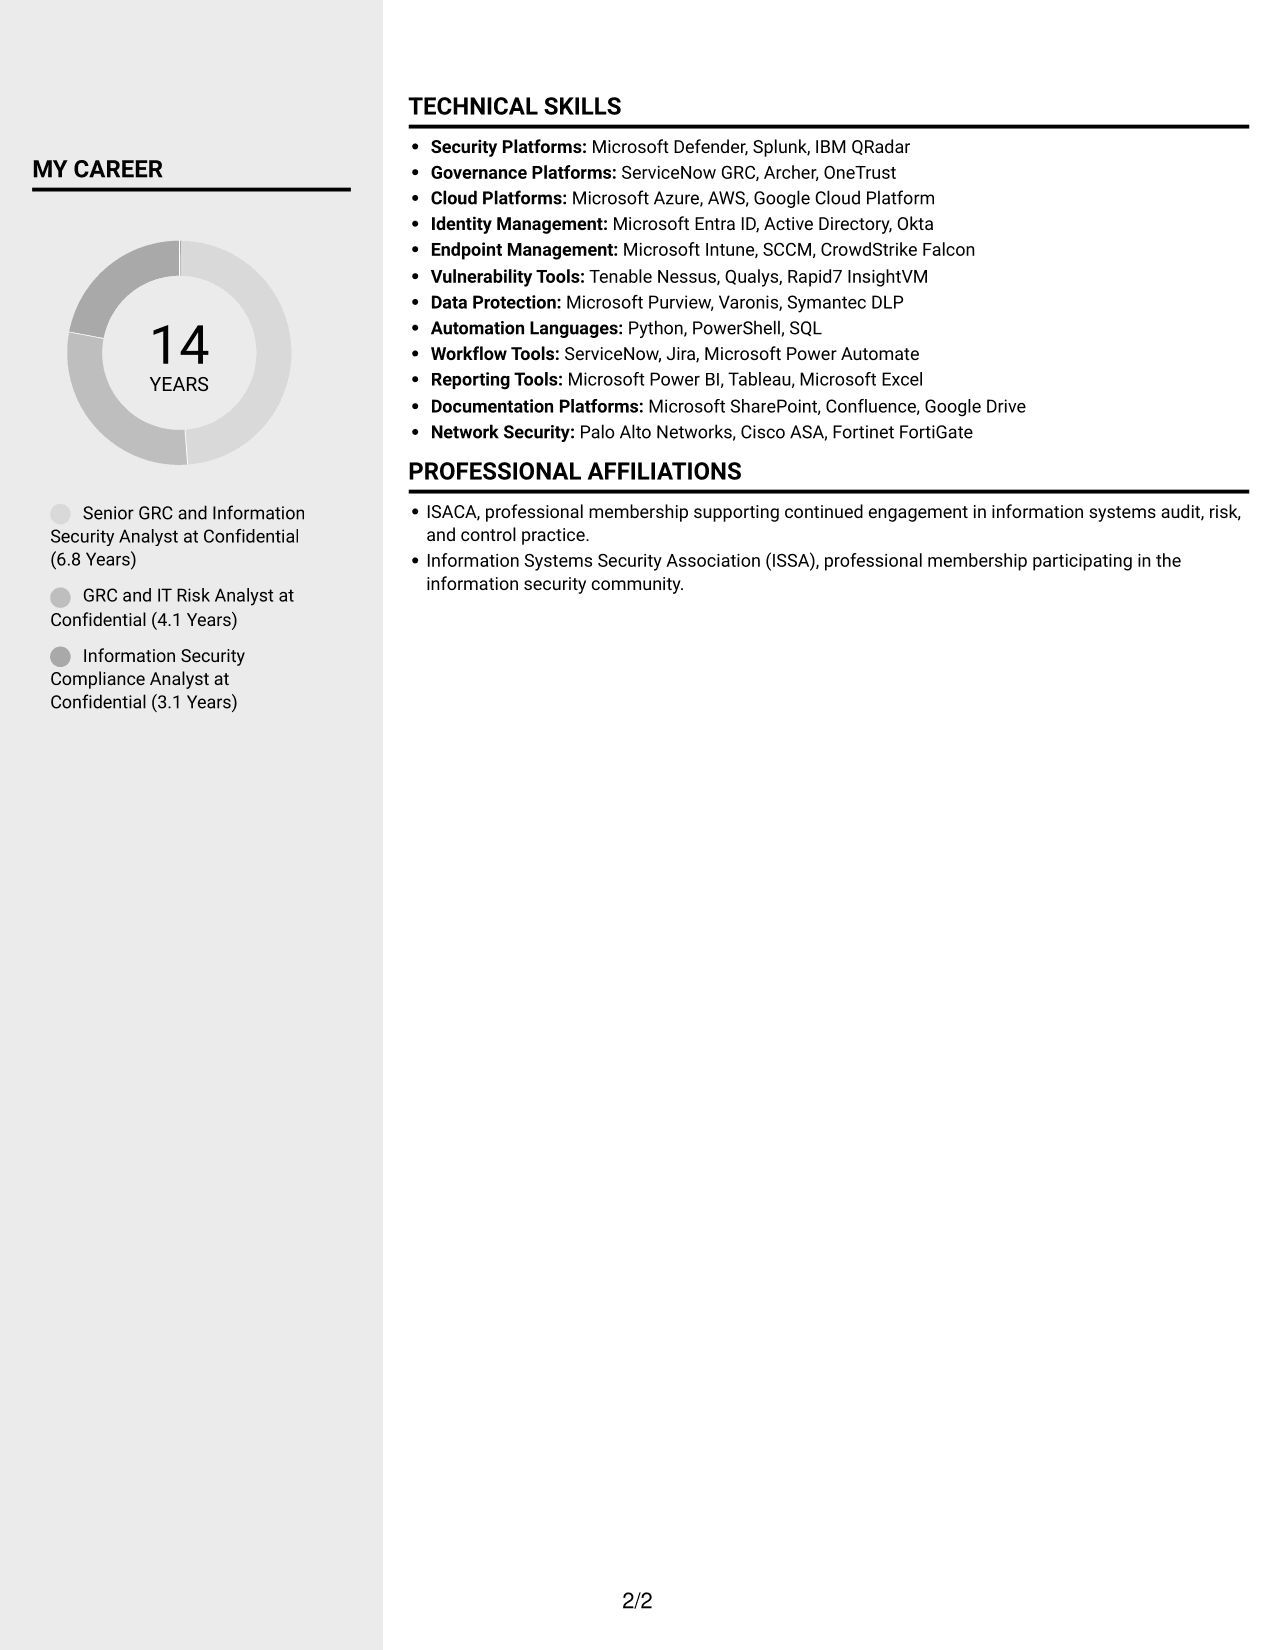
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two columns give experience and supporting sections separate visual areas.
  • Skills, tools, and credentials are easy to locate during experience review.
  • Education and certifications stay visible as reviewers follow career progression.

Best For

  • Experience with supporting details
  • Quick access to skills and credentials
  • Career histories with several roles
  • Education alongside work history
  • Two-area information organization
 

#4 Two Column Format Resume Example

The Two Column Format places resume information in two parallel areas, giving reviewers a direct way to move between experience and supporting details.
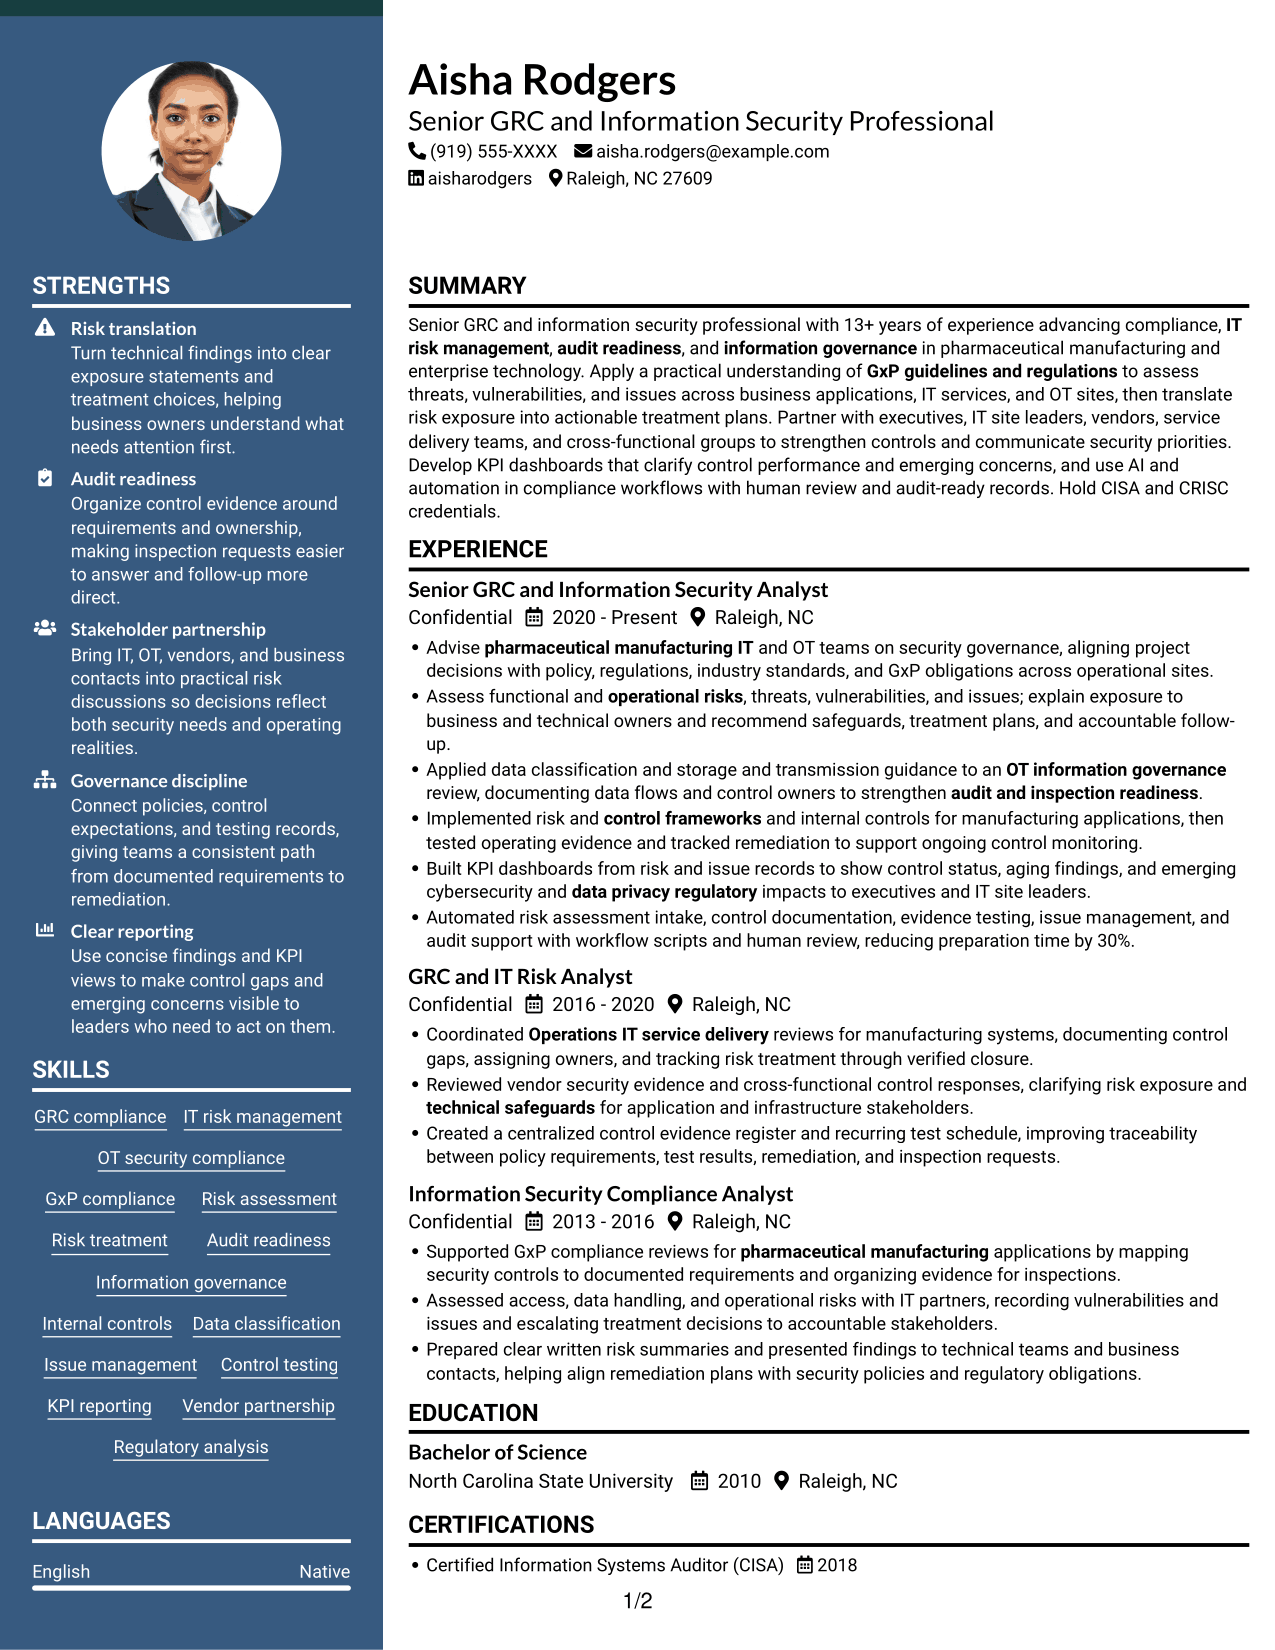
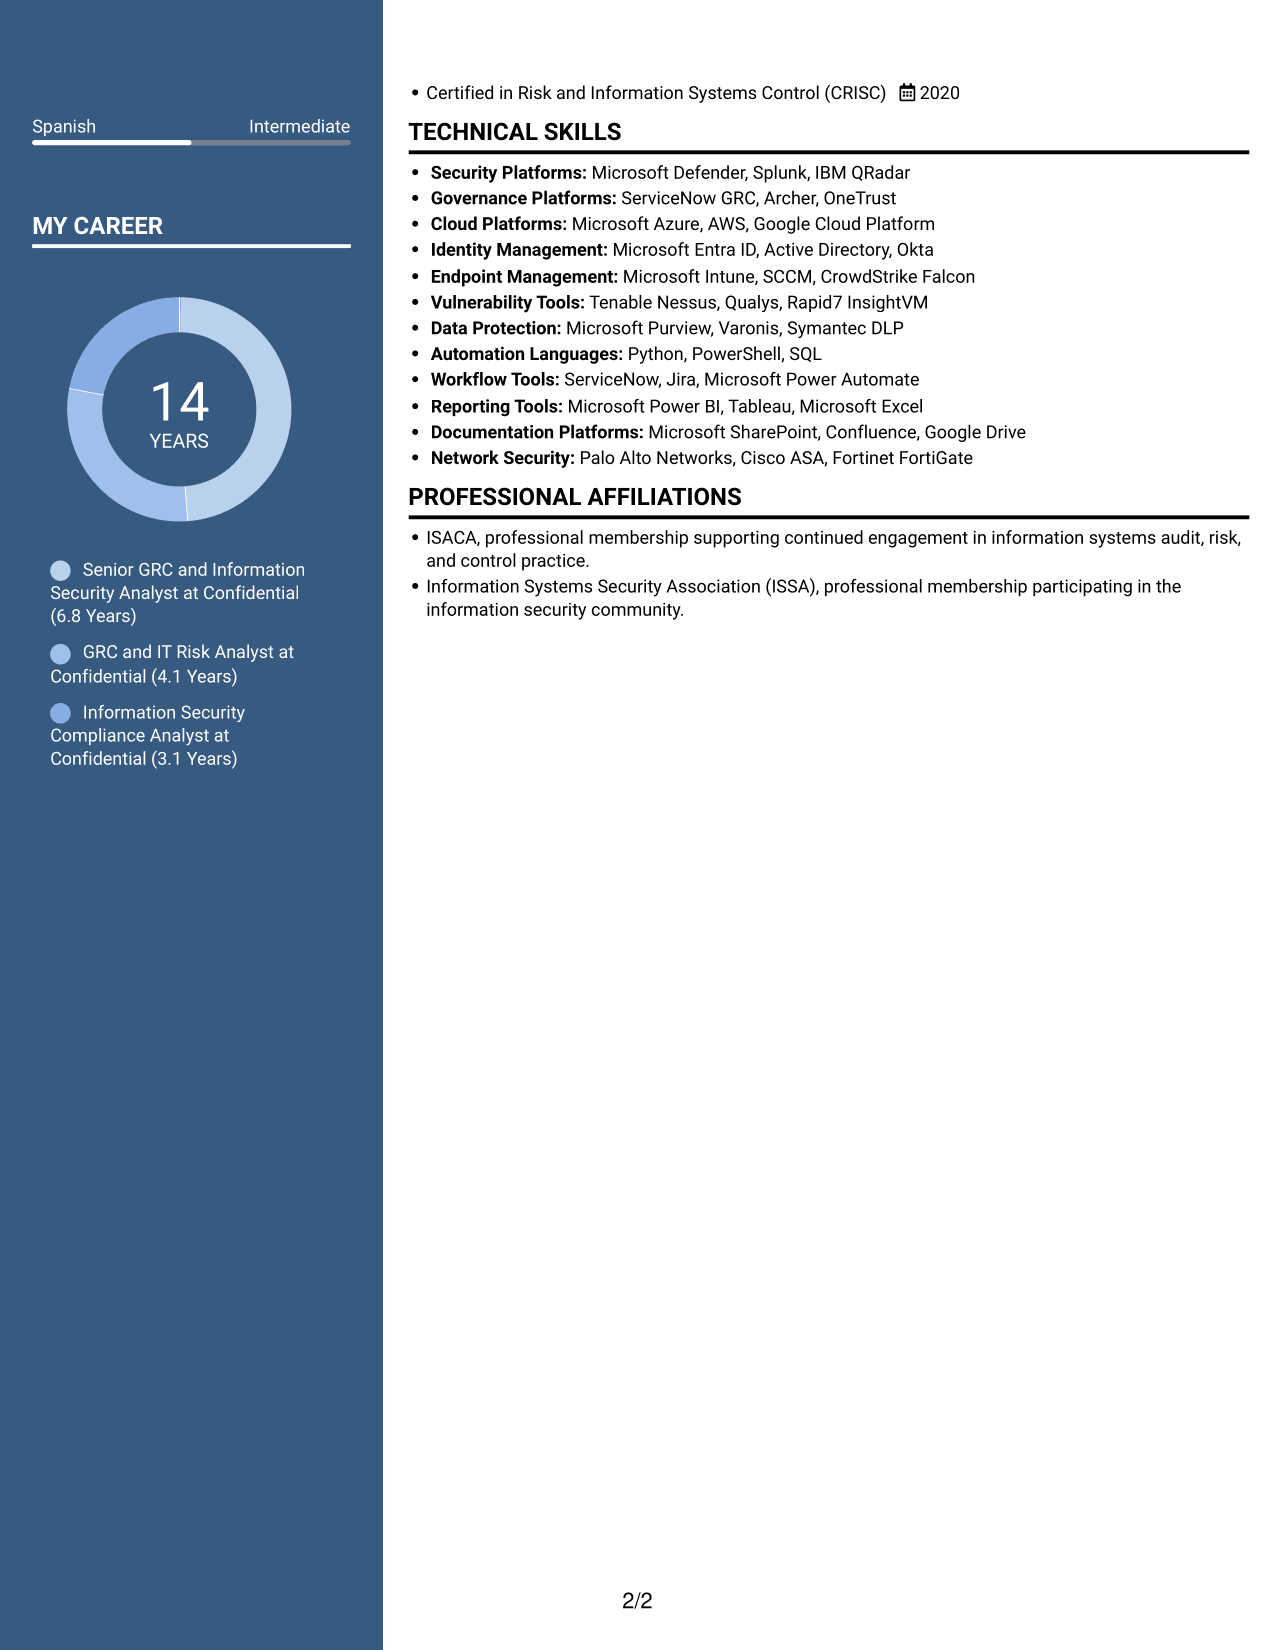
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Paired columns let reviewers compare experience with skills and credentials.
  • Clear section breaks distinguish achievements from education and certifications.
  • Experience entries retain a readable sequence within the broader resume.

Best For

  • Work history with related qualifications
  • Fast review across resume sections
  • Achievement-focused experience entries
  • Skills beside education details
  • Compact two-column organization


#5 Photo Header Two Column Format Resume Example

The Photo Header Two Column Format pairs a photo header with two content columns, for readers who prefer a personal image and grouped resume details.
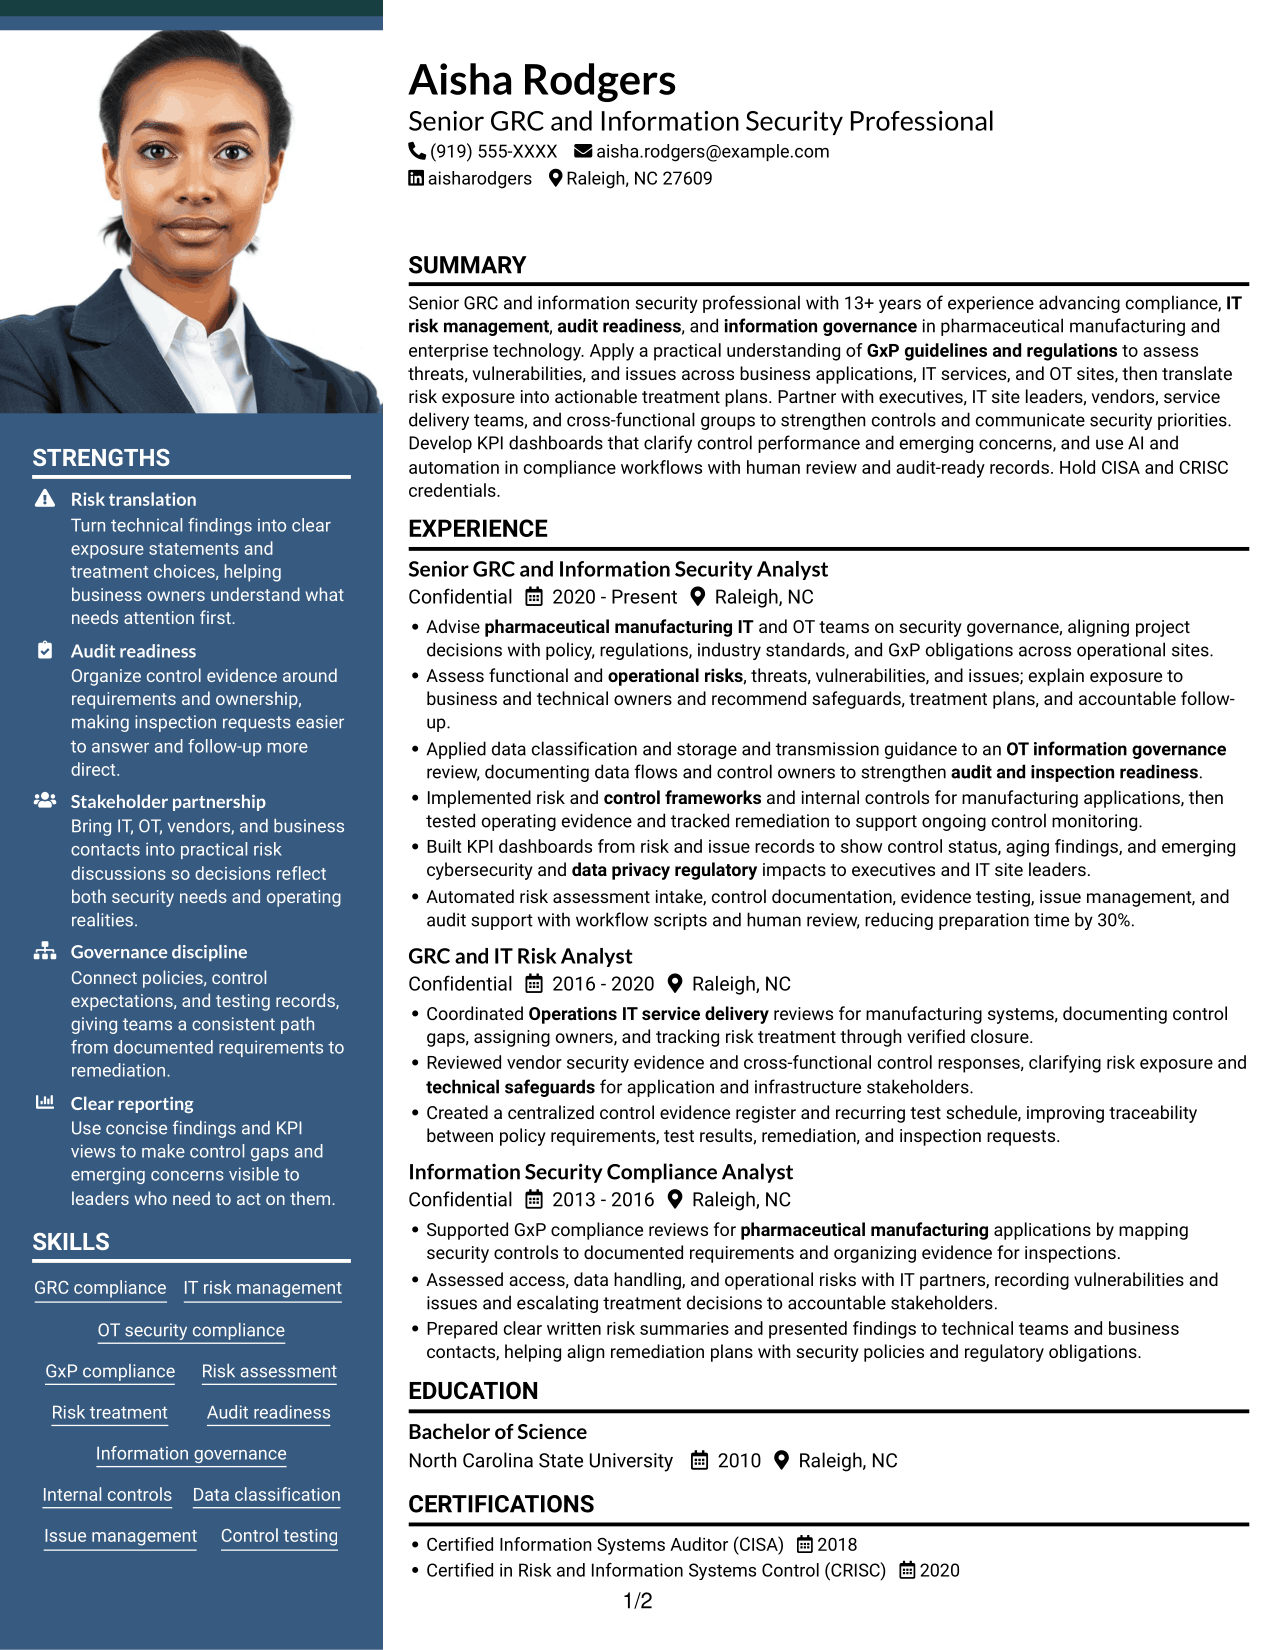
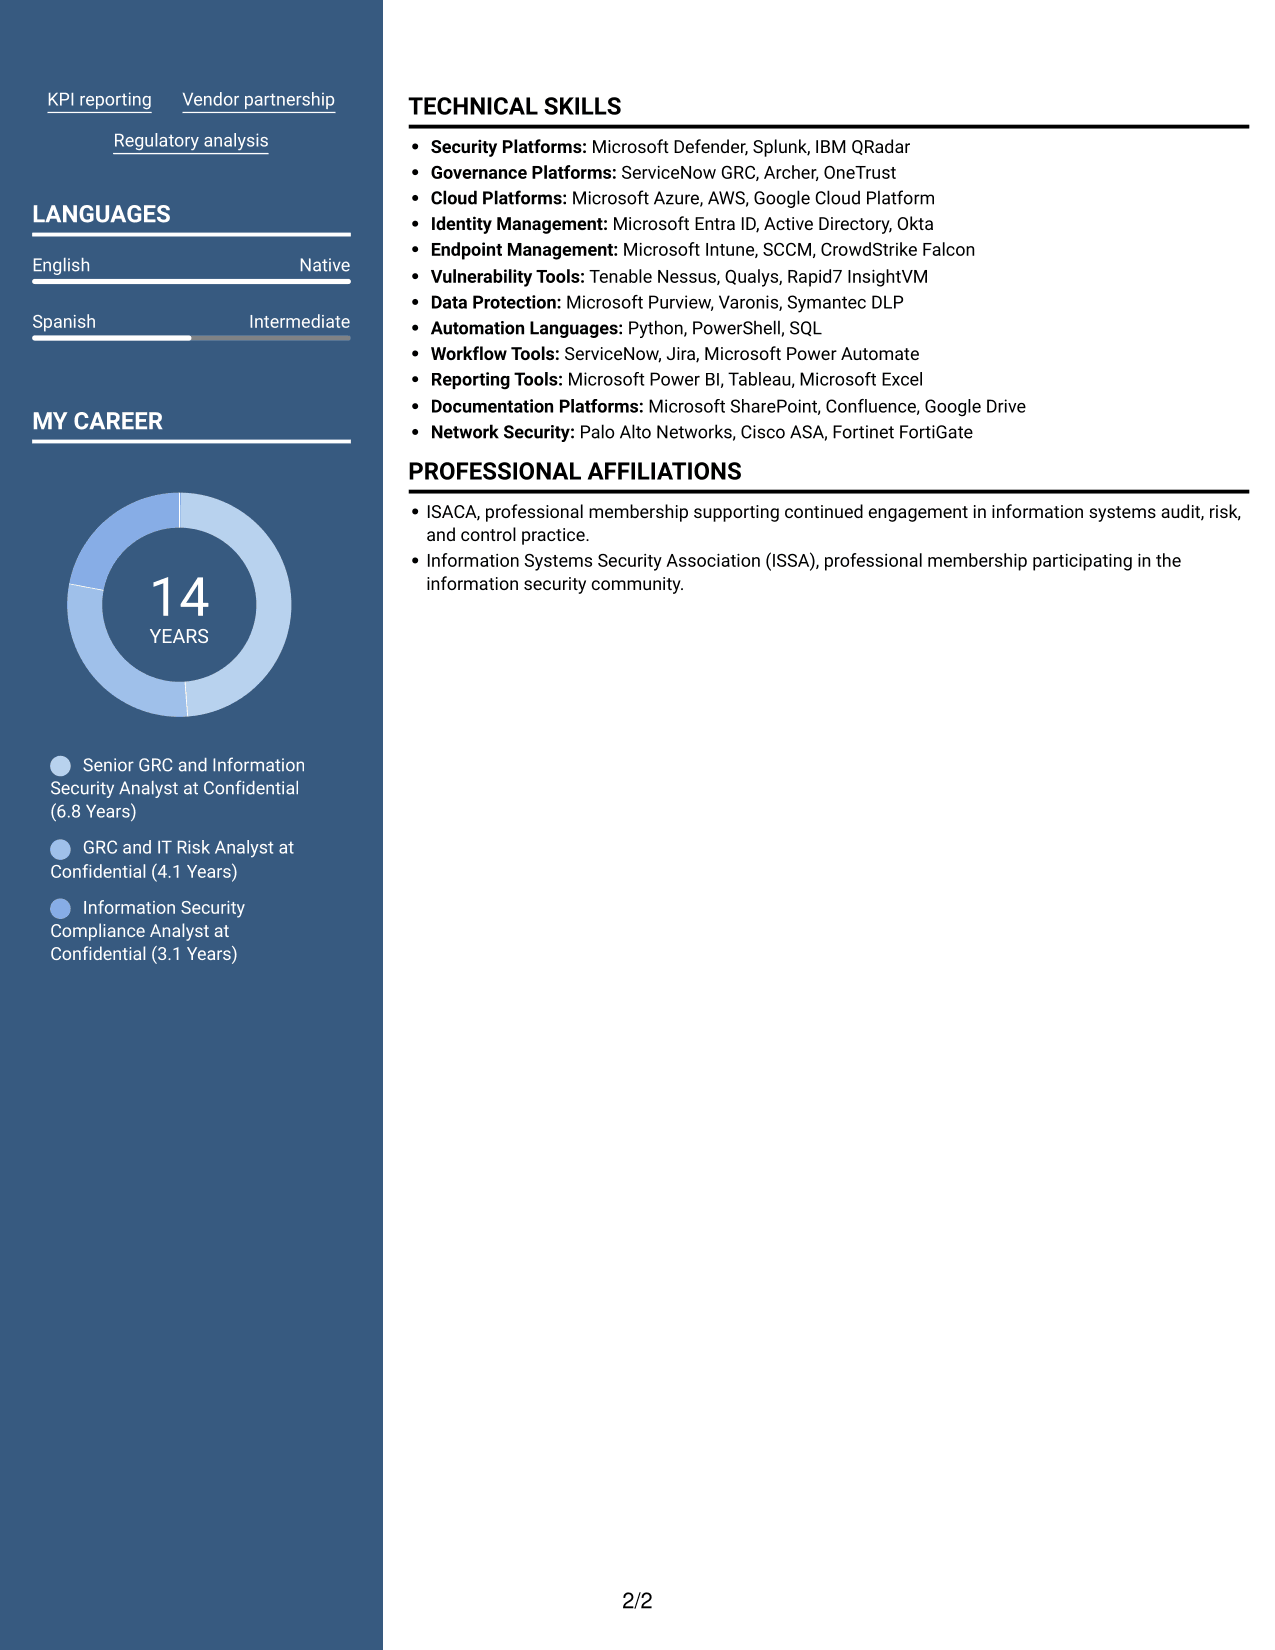
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two columns separate career history from supporting information for review.
  • Skills and tools remain distinct from experience and achievement details.
  • Education and certifications are easy to find among the resume sections.

Best For

  • Photo-based resume presentation
  • Experience with related supporting details
  • Skills and tools needing clear grouping
  • Credentials alongside career history
  • Two-column resume reading
 

#6 Colored Two Column Format Resume Example

The Colored Two Column Format organizes resume content in two columns, a useful option for readers who want related details grouped across the page.
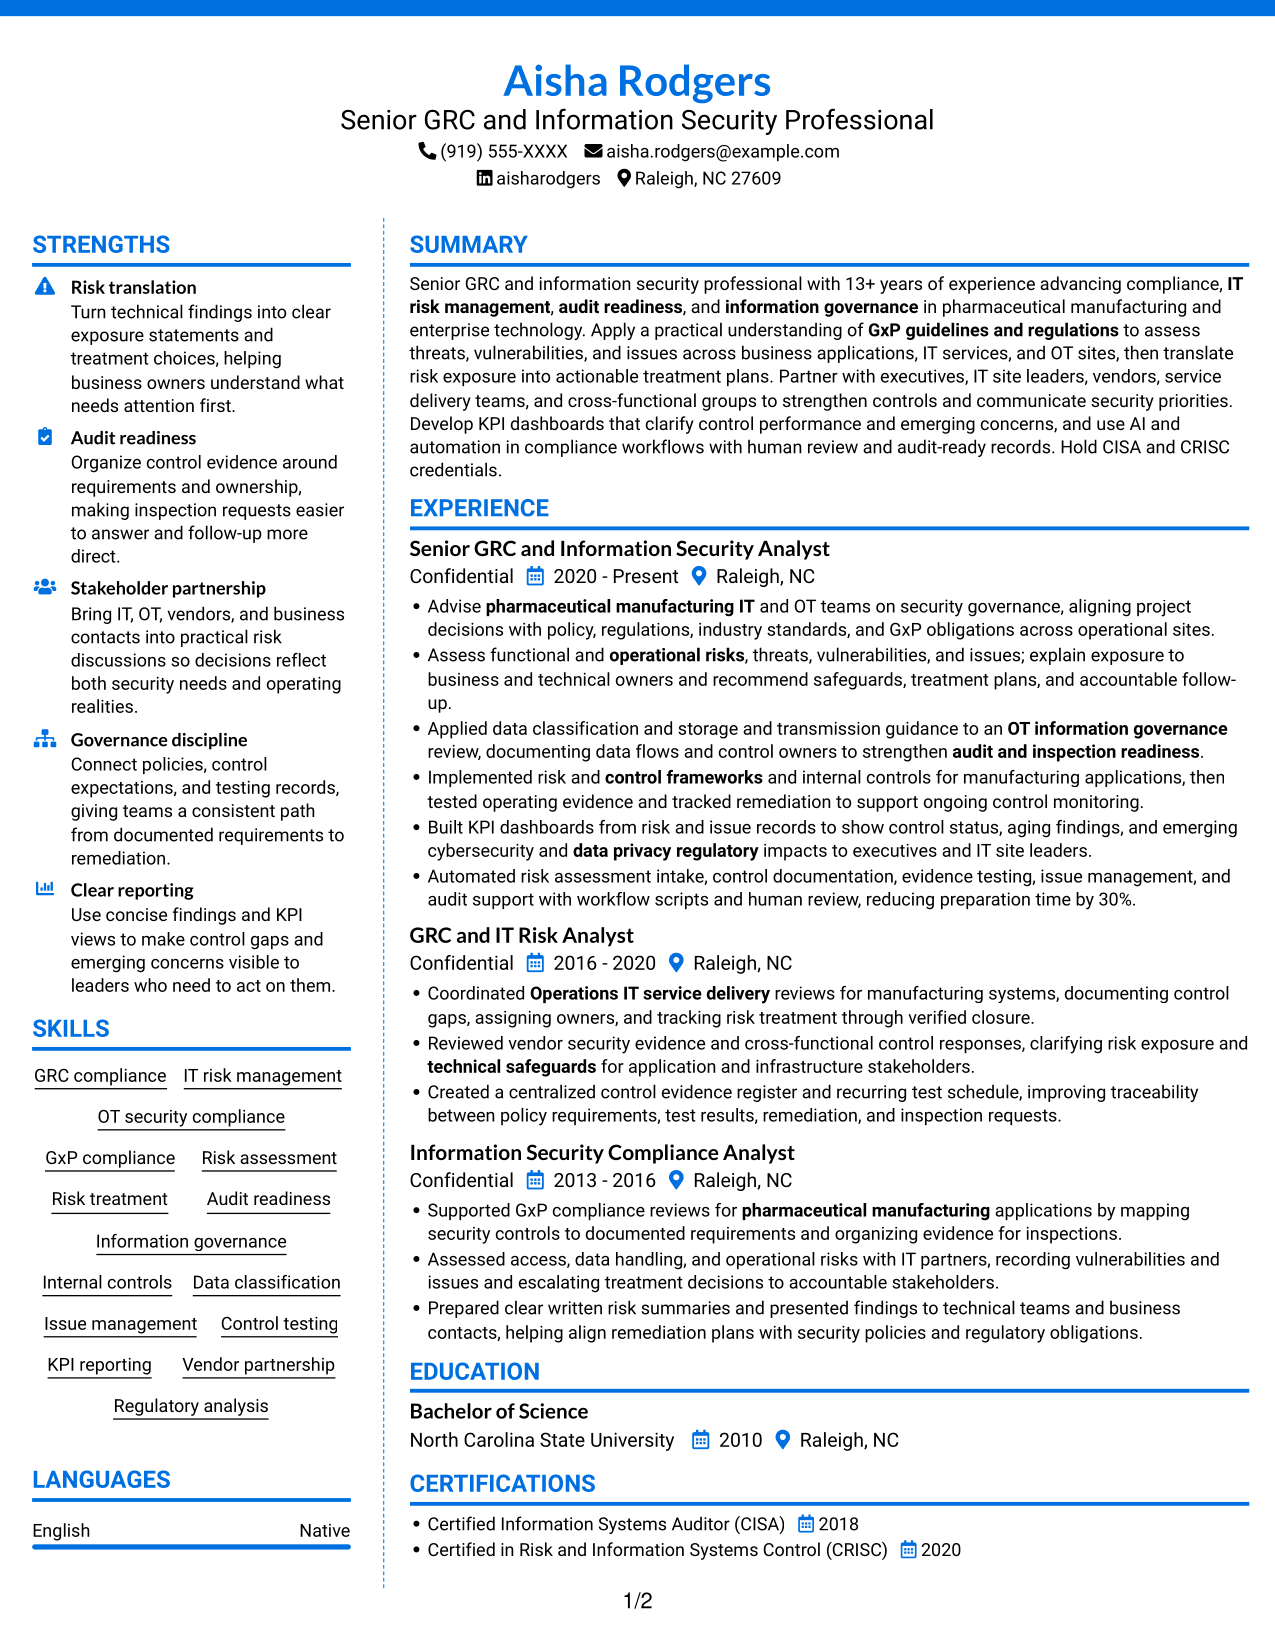
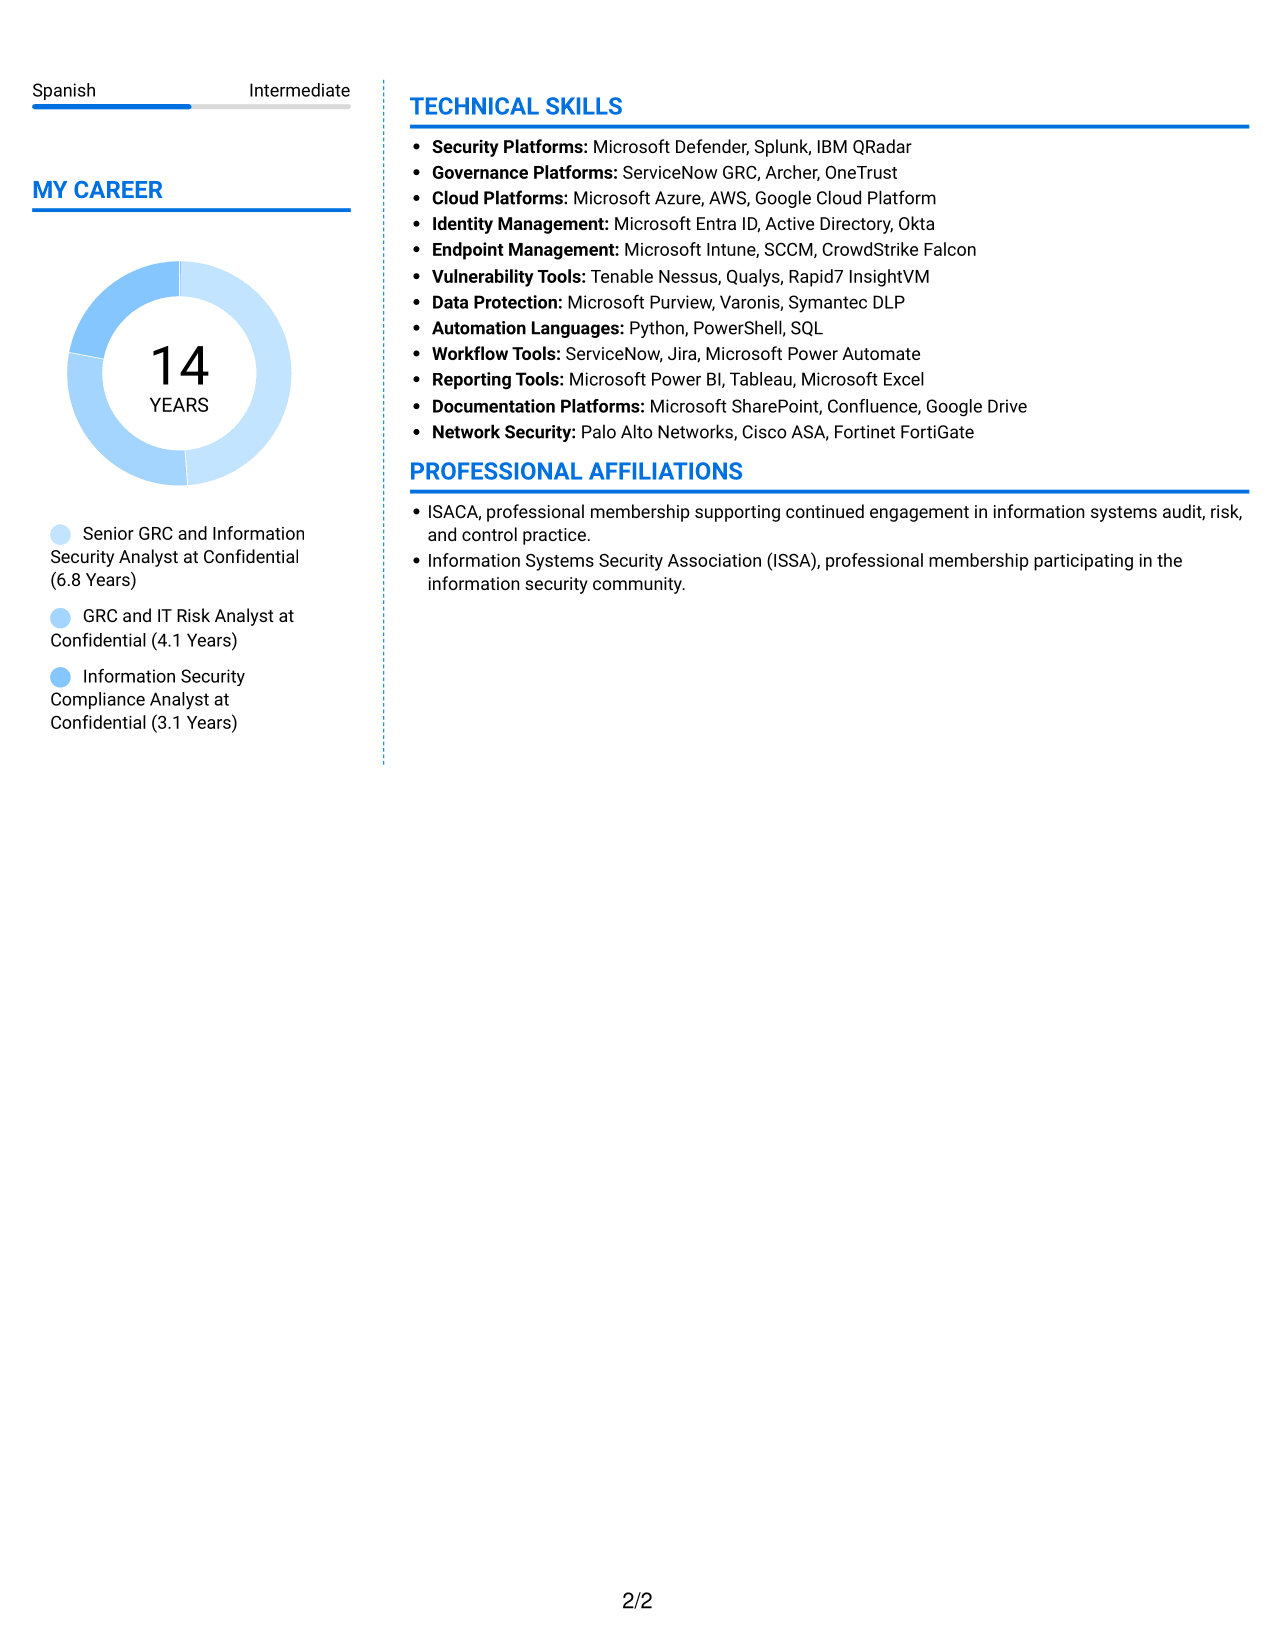
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Two content areas help reviewers move between experience and supporting sections.
  • Distinct section groupings keep skills separate from career history.
  • Education, certifications, and achievements remain easy to locate.

Best For

  • Related resume details grouped together
  • Career history with multiple supporting sections
  • Quick access to education and credentials
  • Skills separate from experience entries
  • Two-column content organization
 

#7 Stylish Two Column Designer Format Resume Example

The Stylish Two Column Designer Format presents resume content in two columns, suiting readers who prefer a structured layout for experience and supporting information.
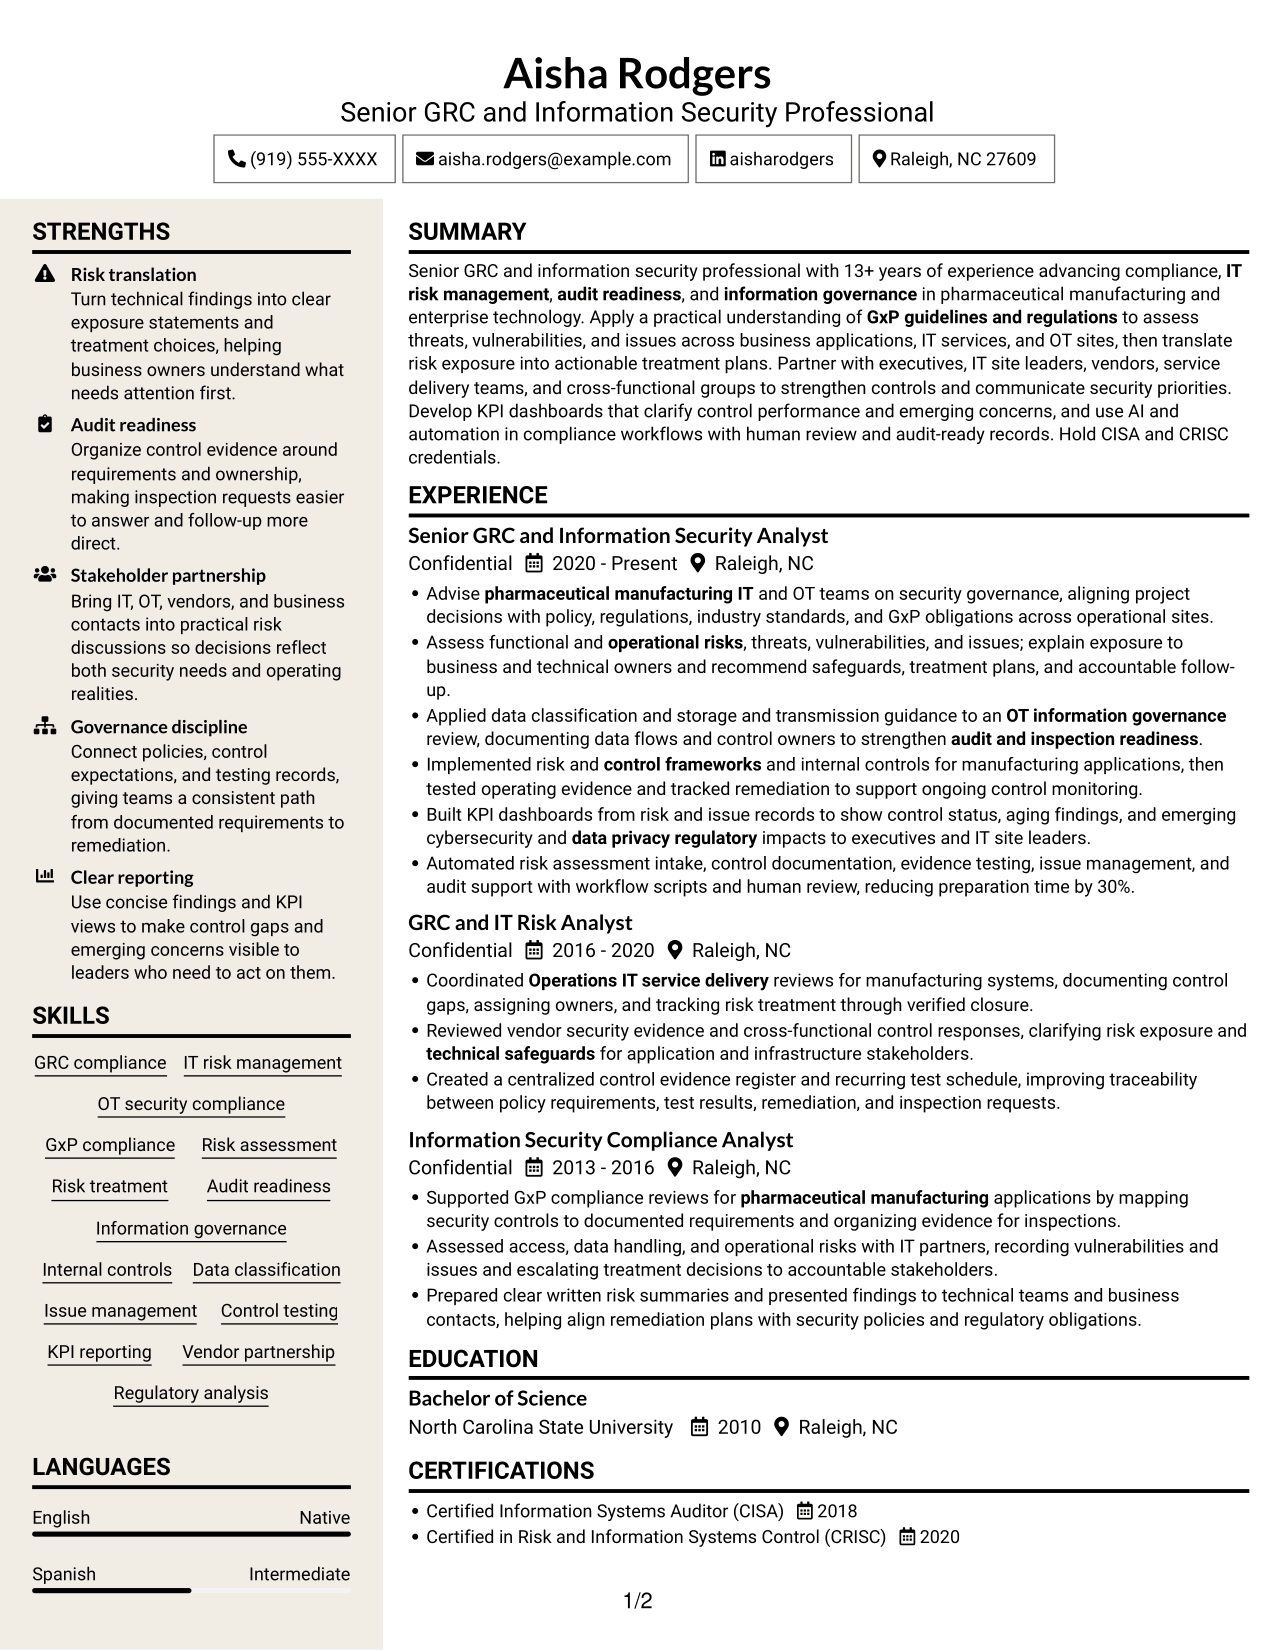
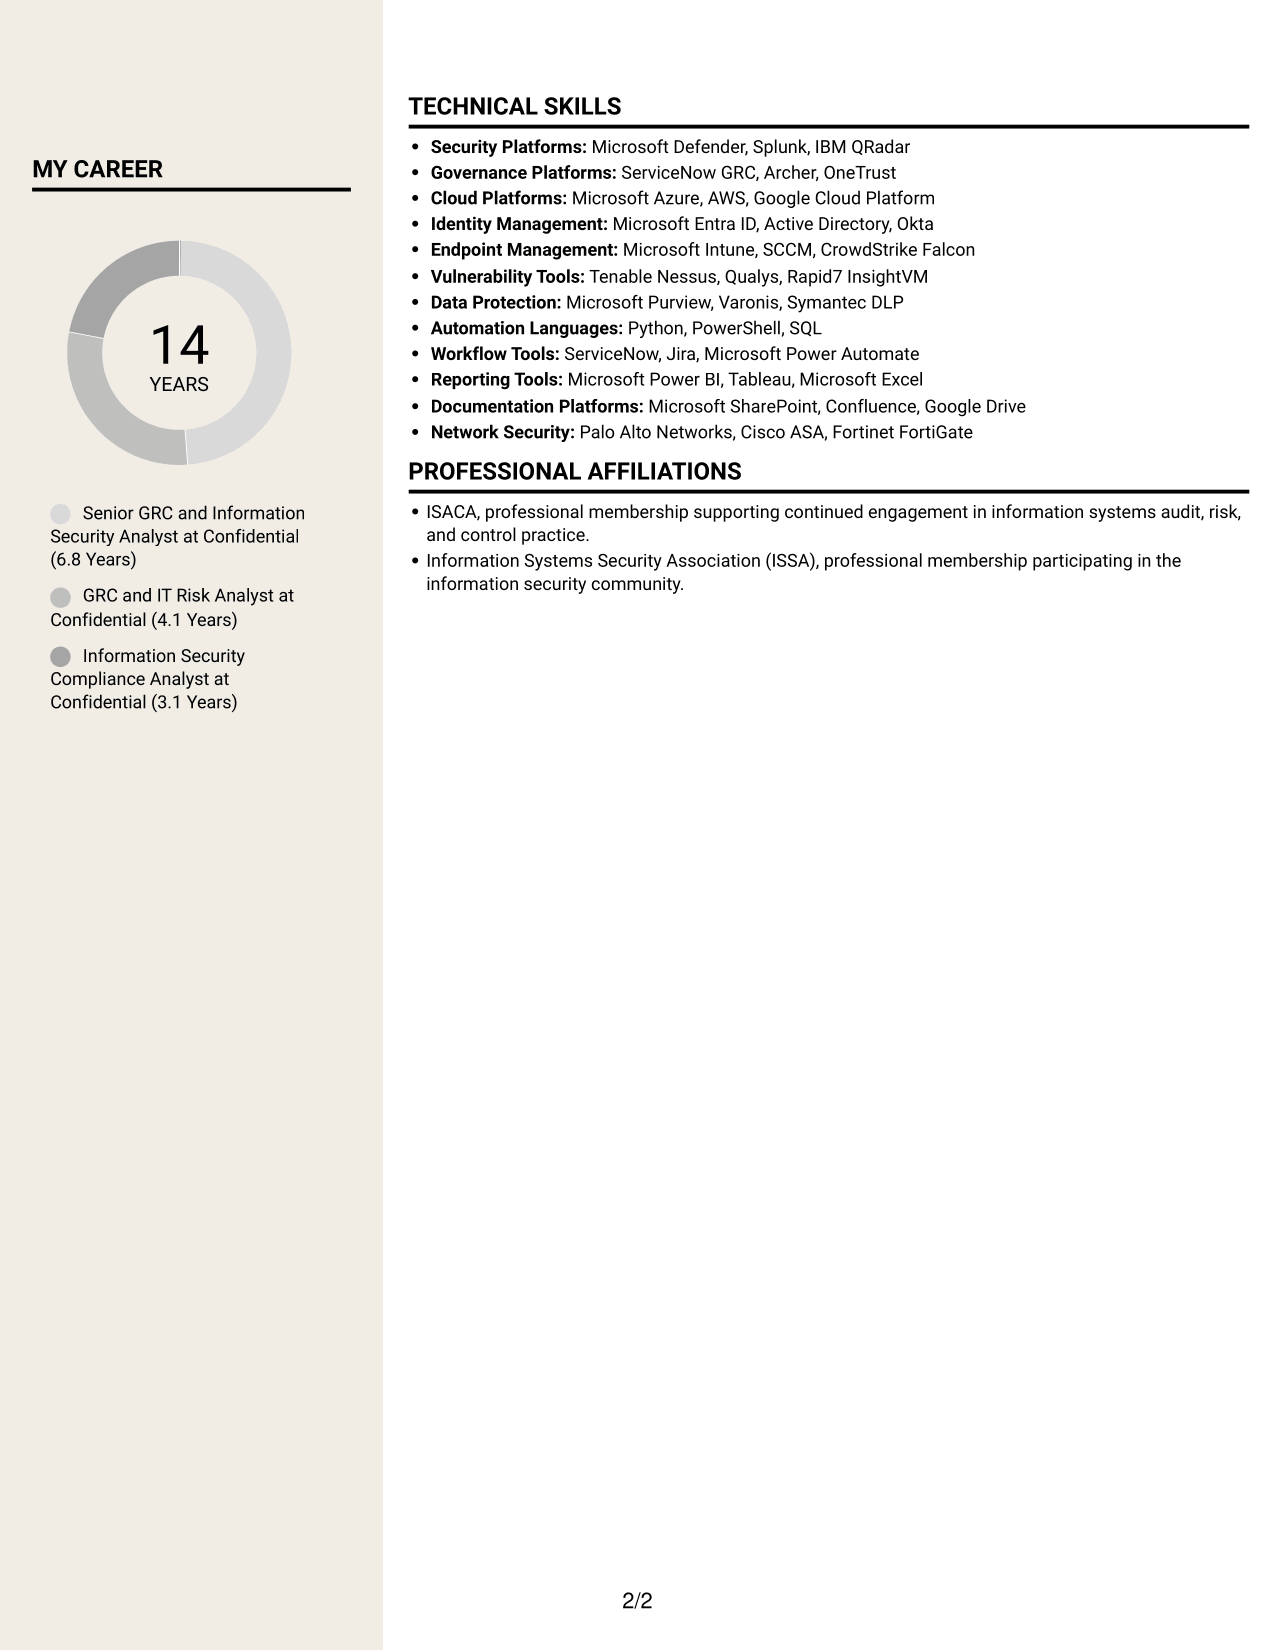
 
Resume example — page 1   Resume example — page 2

Why This Format Works

  • Career history and supporting content occupy separate areas for easier navigation.
  • Skills and credentials can be found without losing the experience sequence.
  • Section grouping helps reviewers distinguish education from achievement details.

Best For

  • Structured review of career history
  • Experience with separate support details
  • Skills and credentials for quick reference
  • Education and achievement records
  • Two-column resume organization


Why Use ResumeInMinutes to Build Your GRC Compliance Resume

ResumeInMinutes provides resume examples and layouts to help you organize experience, skills, tools, certifications, and results for clear review.

  • Resume layout options
  • Clear resume section structure
  • Space for role-specific keywords
  • Organized skills and tools
  • PNG image previews
  • Options to view or customize an example in the editor

Choose a layout that makes your experience easy to scan, then tailor the resume to show relevant evidence in GxP compliance, IT and OT risk, controls, and audit support.


See Also


Frequently Asked Questions

Are these GRC Compliance Senior Analyst - IT/OT Security Compliance resume templates ATS-friendly?

The examples use clear sections and readable headings. Match relevant terms, such as GxP compliance, IT/OT security, risk treatment, and internal controls, to your own experience.

Are these different resume examples?

This guide presents one resume example in several layouts. Review the image previews to compare the designs.

What should a GRC Compliance Senior Analyst - IT/OT Security Compliance resume include?

Include a focused summary, relevant experience, skills, education, and certifications. Show evidence of risk assessment, GxP compliance, control testing, audit readiness, and measurable results where supported.

Which resume layout works well for this role?

Choose a layout with clear headings and a simple reading order. This helps recruiters scan your risk, compliance, and control experience, and can make resume sections easier for applicant tracking systems to read.

How can I show GRC results on my resume?

Describe the risk or control issue, the action you took, and the outcome. Add figures when you can support them, such as reduced preparation time or faster issue closure.

Should I include tools and certifications?

Include relevant tools you have used and current credentials, such as CISA or CRISC when applicable. Keep the skills section focused on the requirements and evidence most relevant to this role.
ATS Score 98%

How we calculate this score

  • Keywords: 60% of the total. AI extracts keywords from your job description. If you do not provide one, a standard job description for the title matching your resume is used. This is not a match to a specific vacancy.
  • Text-based resume: 20%. The text resume assessed here receives 100 for this part.
  • Resume quality: 20%. We start at 100 and subtract points for issues found by our resume checks, down to a minimum of zero.
  • Keyword coverage = round(100 × confirmed matches ÷ total keywords). Exact matches and supported equivalents verified by AI receive full credit; unsupported keywords receive none. Live text checks use the saved equivalents and do not request a new AI review. Without keywords, no overall ATS score is available.
  • Final score = 60% of keyword coverage + 20% of the text score + 20% of the quality score, rounded to a whole number. Without keywords, no overall ATS score is available.

What this score means

Our scores are estimates, not employer ratings. They may contain errors and do not guarantee accurate parsing, a ranking, an interview, or a job. Check your document against the employer’s requirements. You are responsible for relying on this score.

Terms and Conditions

Score weights: Keywords 60% · Text based resume 20% · Resume quality 20%

Keyword coverage: 31 of 32 (97%) · Resume quality: 100%

Resume quality 100% · Weight 20% · Issues (0)

Details
  • ✓Name present: Aisha Rodgers
  • ✓Email format: aisha.rodgers@example.com
  • ✓Phone format: (919) 555-XXXX
  • ✓Experience 1: Job title: Senior GRC and Information Security Analyst
  • ✓Experience 1: Company name: Confidential
  • ✓Experience 1: Work location: Raleigh, NC
  • ✓Experience 1: Employment dates: 2020 - Present
  • ✓Experience 1: Description or achievements: Present
  • ✓Experience 2: Job title: GRC and IT Risk Analyst
  • ✓Experience 2: Company name: Confidential
  • ✓Experience 2: Work location: Raleigh, NC
  • ✓Experience 2: Employment dates: 2016 - 2020
  • ✓Experience 2: Description or achievements: Present
  • ✓Experience 3: Job title: Information Security Compliance Analyst
  • ✓Experience 3: Company name: Confidential
  • ✓Experience 3: Work location: Raleigh, NC
  • ✓Experience 3: Employment dates: 2013 - 2016
  • ✓Experience 3: Description or achievements: Present
  • ✓No placeholder fields
  • ✓No repeated achievement bullets
  • ✓No empty bullets

No issues found by the current checks.

Text Based Resume 100% · Weight 20%

Parsed text
Aisha Rodgers
Senior GRC and Information Security Professional
(919) 555-XXXX
aisharodgers
aisha.rodgers@example.com
Raleigh, NC 27609
STRENGTHS
Risk translation
Turn technical findings into clear exposure statements and treatment choices, helping business owners understand what needs attention first.
Audit readiness
Organize control evidence around requirements and ownership, making inspection requests easier to answer and follow-up more direct.
Stakeholder partnership
Bring IT, OT, vendors, and business contacts into practical risk discussions so decisions reflect both security needs and operating realities.
Governance discipline
Connect policies, control expectations, and testing records, giving teams a consistent path from documented requirements to remediation.
Clear reporting
Use concise findings and KPI views to make control gaps and emerging concerns visible to leaders who need to act on them.
SUMMARY
Senior GRC and information security professional with 13+ years of experience advancing compliance, IT risk management, audit readiness, and information governance in pharmaceutical manufacturing and enterprise technology. Apply a practical understanding of GxP guidelines and regulations to assess threats, vulnerabilities, and issues across business applications, IT services, and OT sites, then translate risk exposure into actionable treatment plans. Partner with executives, IT site leaders, vendors, service delivery teams, and cross-functional groups to strengthen controls and communicate security priorities. Develop KPI dashboards that clarify control performance and emerging concerns, and use AI and automation in compliance workflows with human review and audit-ready records. Hold CISA and CRISC credentials.
EXPERIENCE
Senior GRC and Information Security Analyst
Confidential
2020 - Present
Raleigh, NC
Advise pharmaceutical manufacturing IT and OT teams on security governance, aligning project decisions with policy, regulations, industry standards, and GxP obligations across operational sites.
Assess functional and operational risks, threats, vulnerabilities, and issues; explain exposure to business and technical owners and recommend safeguards, treatment plans, and accountable follow-up.
Applied data classification and storage and transmission guidance to an OT information governance review, documenting data flows and control owners to strengthen audit and inspection readiness.
Implemented risk and control frameworks and internal controls for manufacturing applications, then tested operating evidence and tracked remediation to support ongoing control monitoring.
Built KPI dashboards from risk and issue records to show control status, aging findings, and emerging cybersecurity and data privacy regulatory impacts to executives and IT site leaders.
Automated risk assessment intake, control documentation, evidence testing, issue management, and audit support with workflow scripts and human review, reducing preparation time by 30%.
GRC and IT Risk Analyst
Confidential
2016 - 2020
Raleigh, NC
Coordinated Operations IT service delivery reviews for manufacturing systems, documenting control gaps, assigning owners, and tracking risk treatment through verified closure.
Reviewed vendor security evidence and cross-functional control responses, clarifying risk exposure and technical safeguards for application and infrastructure stakeholders.
Created a centralized control evidence register and recurring test schedule, improving traceability between policy requirements, test results, remediation, and inspection requests.
Information Security Compliance Analyst
Confidential
2013 - 2016
Raleigh, NC
Supported GxP compliance reviews for pharmaceutical manufacturing applications by mapping security controls to documented requirements and organizing evidence for inspections.
Assessed access, data handling, and operational risks with IT partners, recording vulnerabilities and issues and escalating treatment decisions to accountable stakeholders.
Prepared clear written risk summaries and presented findings to technical teams and business contacts, helping align remediation plans with security policies and regulatory obligations.
SKILLS
GRC compliance
Internal controls
Issue management
GxP compliance
KPI reporting
Risk treatment
Information governance
OT security compliance
Regulatory analysis
Vendor partnership
IT risk management
Data classification
Risk assessment
Audit readiness
Control testing
EDUCATION
Bachelor of Science
North Carolina State University
2010
Raleigh, NC
LANGUAGES
English
Native
Spanish
Intermediate
CERTIFICATIONS
Certified Information Systems Auditor (CISA)
2018
Certified in Risk and Information Systems Control (CRISC)
2020
TECHNICAL SKILLS
Security Platforms: Microsoft Defender, Splunk, IBM QRadar
Governance Platforms: ServiceNow GRC, Archer, OneTrust
Cloud Platforms: Microsoft Azure, AWS, Google Cloud Platform
Identity Management: Microsoft Entra ID, Active Directory, Okta
Endpoint Management: Microsoft Intune, SCCM, CrowdStrike Falcon
Vulnerability Tools: Tenable Nessus, Qualys, Rapid7 InsightVM
Data Protection: Microsoft Purview, Varonis, Symantec DLP
Automation Languages: Python, PowerShell, SQL
Workflow Tools: ServiceNow, Jira, Microsoft Power Automate
Reporting Tools: Microsoft Power BI, Tableau, Microsoft Excel
Documentation Platforms: Microsoft SharePoint, Confluence, Google Drive
Network Security: Palo Alto Networks, Cisco ASA, Fortinet FortiGate
MY CAREER
14Years
Senior GRC and Information Security Analyst at Confidential (6.8 Years)
GRC and IT Risk Analyst at Confidential (4.1 Years)
Information Security Compliance Analyst at Confidential (3.1 Years)
PROFESSIONAL AFFILIATIONS
ISACA, professional membership supporting continued engagement in information systems audit, risk, and control practice.
Information Systems Security Association (ISSA), professional membership participating in the information security community.

Matched keywords (31)

  • 13+ years of experience advancing compliance, IT risk management, audit readiness, and information governance in pharmaceutical manufacturing and enterprise technology.Original keyword in JD: 8+ years of business information security, compliance, IT risk management, audit management, information governance, or GRC experience
  • Bachelor of ScienceOriginal keyword in JD: University degree in a business, technical, or scientific field OR comparable education and experience
  • CISAOriginal keyword in JD: CISM OR CRISC OR CISA OR CISSP OR CCSP
  • GxP guidelines and regulationsOriginal keyword in JD: Good Practice Quality (GxP) guidelines and regulations
  • Assess functional and operational risks, threats, vulnerabilities, and issuesOriginal keyword in JD: Risk, vulnerability, and issue management
  • Information Security Compliance
  • OT security complianceOriginal keyword in JD: IT/OT security compliance
  • security governanceOriginal keyword in JD: Information security governance
  • Assess functional and operational risksOriginal keyword in JD: Operational risk management
  • Assess functional and operational risksOriginal keyword in JD: Functional risk management
  • recommend safeguards, treatment plans, and accountable follow-upOriginal keyword in JD: Risk assessment and treatment
  • translate risk exposure into actionable treatment plansOriginal keyword in JD: Risk exposure analysis
  • technical safeguards
  • Internal controls
  • risk and control frameworks
  • Information governance
  • Data classification
  • Applied data classification and storage and transmission guidance to an OT information governance reviewOriginal keyword in JD: Data storage and transmission guidance
  • audit and inspection readiness
  • Implemented risk and control frameworks and internal controls for manufacturing applications, then tested operating evidence and tracked remediation to support ongoing control monitoring.Original keyword in JD: Control implementation and monitoring
  • Built KPI dashboardsOriginal keyword in JD: KPI reporting and dashboards
  • emerging cybersecurity and data privacy regulatory impactsOriginal keyword in JD: Cybersecurity and data privacy regulatory impact assessment
  • aligning project decisions with policy, regulations, industry standards, and GxP obligationsOriginal keyword in JD: Security policy and regulatory alignment
  • Advise pharmaceutical manufacturing IT and OT teams on security governance, aligning project decisions with policy, regulations, industry standards, and GxP obligations across operational sites.Original keyword in JD: Manufacturing environment policy implementation
  • pharmaceutical manufacturing
  • Partner with executives, IT site leaders, vendors, service delivery teams, and cross-functional groupsOriginal keyword in JD: Vendor and cross-functional partnership
  • Operations IT service delivery
  • use AI and automation in compliance workflows with human review and audit-ready records.Original keyword in JD: AI and automation for risk and compliance workflows
  • Automated risk assessment intake, control documentation, evidence testingOriginal keyword in JD: Control documentation and testing
  • Issue management
  • EnglishOriginal keyword in JD: Written and spoken English

Missing keywords (1)

  • Senior executive and IT site leader stakeholder management
Disclaimer: All names, images, contact information, employment histories, achievements, security clearances, military credentials, and other qualifications shown in this content are fictional and used for illustrative purposes only. Any resemblance to actual persons, living or deceased, is purely coincidental.

Resume and cover-letter examples and recommendations in this article reflect general best practices and professional experience and are provided for guidance only. Results may vary based on role, industry, region, and hiring organization.

Content Accuracy and Verification: To the fullest extent permitted by applicable law, we do not represent or warrant that resume or cover-letter guidance, examples, recommendations, or related information are accurate, complete, current, error-free, or suitable for any particular purpose. You are responsible for independently reviewing and verifying the information before relying on it.

ATS and Cover-Letter Scores: ATS scores are estimates calculated using our own formula, informed by publicly available guidance on resume formatting and keyword matching. They are not scores issued or endorsed by an ATS provider or employer. Cover-letter scores are also our own assessments. Parsing, weighting, screening criteria, and results vary between systems, employers, job descriptions, and document formats. No score guarantees successful parsing, a particular ranking, an interview, or employment. Use scores as general guidance and independently check your documents against the employer’s requirements. To the fullest extent permitted by applicable law, we accept no liability for errors in scores or parsing, or losses arising from reliance on these assessments. Nothing in this notice excludes liability or limits consumer rights that cannot lawfully be excluded or limited.

Terms and Conditions
 
> JP 1 1
PDF Footer and Margins Setup
The margins are applied to the document, and the footer shows up in the preview and the PDF

Footer Font Settings

Are you applying for a specific job
so we can tailor your resume to it?
Are you applying for a specific job
so we can tailor your cover letter to it?

Your data stays private and is never used for training.Privacy Policy

Type your details as text to generate a personalized resume Type your details as text to generate a personalized cover letter
Website link found! Ready to create resume from:

Your data stays private and is never used for training.Privacy Policy

Drag the into the box to verify you're human.
Drop here

My Resumes

Displaying {number_of_files} files (out of {total_of_all_files} total)
Name File Type Last Modified: Description:

Rename File

Filename already exists!

Delete Files

Warning: This action is irreversible. Once you click submit, the files will be permanently deleted.

Heading text
Upload From Computer Upload
Select From Existing
LinkedIn
Drag & Drop files anywhere in this tab, or

Uploaded Files

Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

My Files

Resumes or cover letters you create will appear here. No files available yet.
Delete Name Last Updated Use This File
Select this to use the file for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Add LinkedIn Profile PDF

You can download your LinkedIn profile as a PDF by opening linkedin.com in a web browser, clicking your profile photo, selecting the “More” or “Resources” button, and choosing “Save to PDF.” You can then attach the PDF using the Upload From Computer tab.

Paste Your LinkedIn Profile Text

If you have copied the LinkedIn profile text, paste it below. See how to copy your profile from LinkedIn

Select this to use the LinkedIn profile text for generating your resume and cover letter. Only one source—uploaded file, selected file, or LinkedIn text—can be used.

Try these controls

<
>